项目说明
!InfraGuard Logo
Red team infrastructure tracker and C2 redirector -- a modern alternative to RedWarden.
InfraGuard sits between the internet and your C2 teamserver, every inbound request against your malleable C2 profile and blocking anything that doesn't conform. Scanners, bots, and blue team probes get redirected to a decoy site while legitimate beacon traffic passes through to your teamserver.
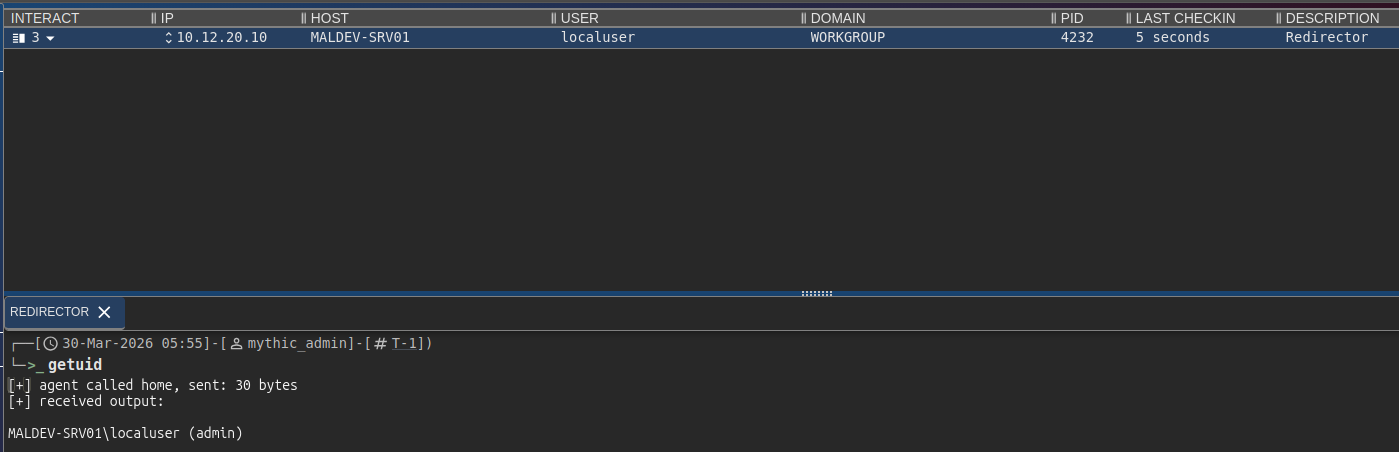
!Mythic Callbacks Xenon
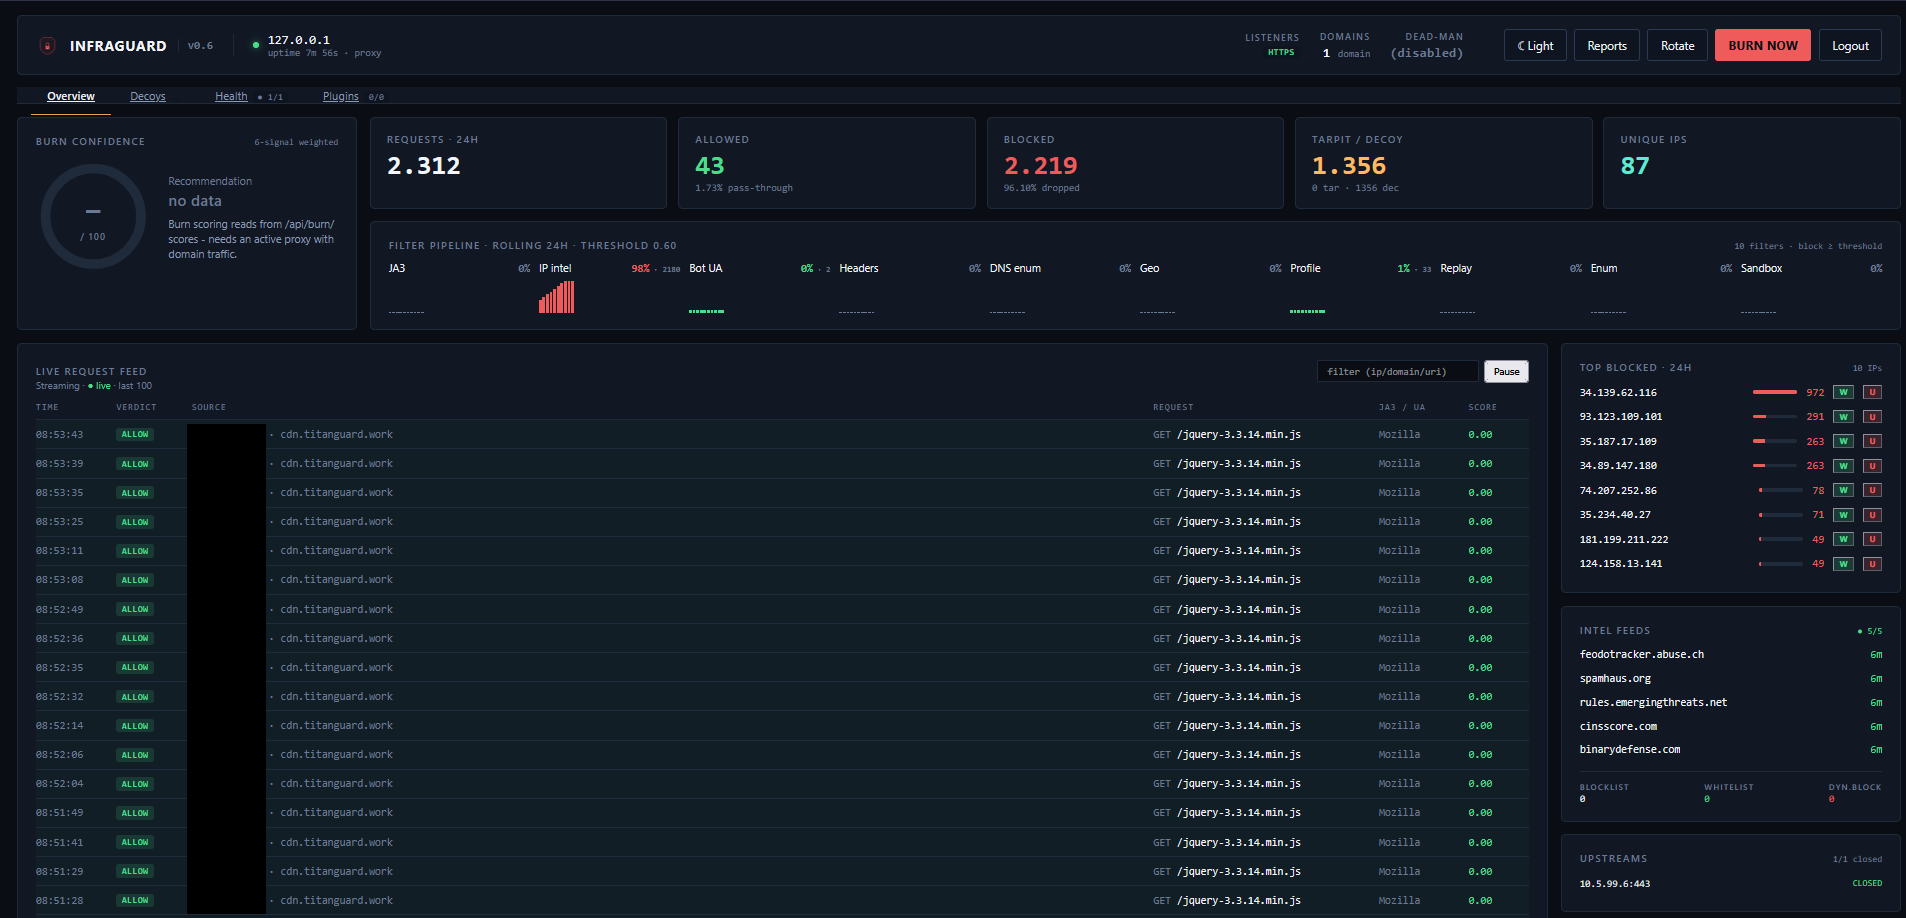
!InfraGuard Dashboard
Architecture
!Architecture Diagram
Features
Proxying & Listeners
Multi-domain proxying -- proxy multiple domains simultaneously, each with independent C2 profiles, upstreams, and rulesMulti-protocol listeners -- HTTP/HTTPS, HTTP/3 (QUIC), WebSocket, gRPC, DNS, MQTT, and TCP-tunnel listeners running simultaneously with shared IP intelligence and event trackingCircuit breaker -- per-upstream failure protection with closed/open/half-open states; falls through to the domain's drop action when backends are unreachableProtocol failover -- automatic failover and failback between listener protocols ranked by priorityC2 Profile Support
C2 profile -- parse and enforce Cobalt Strike, Mythic, Brute Ratel C4, Sliver, Havoc, Nighthawk, and PoshC2 profiles as redirector rulesHot-swappable profiles -- swap a domain's active C2 profile at runtime from the dashboard without restarting the proxyProfile generation wizard -- generate new C2 profiles from scratch for all 8 supported types via a guided form, or import and upload existing profiles with automatic type detection and AI-assisted profile generation -- optional Ollama integration provides a chat panel in the dashboard for profile creation help and OPSEC adviceFilter Pipeline
Scoring-based filter pipeline -- 10 filters each contribute a 0.0--1.0 score; configurable threshold determines block/allow. Filters: JA3, IP, bot, header, DNS, geo, profile, replay, enumeration, sandbox.JA3 TLS fingerprint filtering -- block Masscan, ZGrab2, Shodan, curl, Python requests, and Nmap at the TLS handshake layer before any HTTP data is exchanged; works header or custom asyncio protocol; optional allowlist mode enforces beacon JA3Sandbox and headless browser detection -- score-accumulation across HTTP signals: HeadlessChrome UA, missing Accept-Language, Chrome without sec-ch-ua, Safe Links and msnbot scanner UAs, non-browser Accept orderingPath enumeration detection -- per-IP unique URI tracking in a sliding window; blocks dirbuster/ffuf/gobuster before they map URI spaceDNS subdomain enumeration detection -- tracks NXDOMAIN responses per client IP; auto-blocks source IPs on threshold breachAnti-bot / anti-crawling -- 40+ known scanner/bot User-Agent patterns, header anomaly detectionReplay protection -- reject duplicate requests by content hash; hashes persisted to SQLite so protection surviDrop actions -- redirect, TCP reset, proxy to decoy site, or tarpit (slow-drip response to waste scanner time)Intelligence
IP intelligence -- built-in CIDR blocklists for 19 security ranges (Shodan, Censys, Rapid7, etc.), GeoIP filtering, reverse DNS keyword matchingThreat intel feeds -- auto-update blocklists from public sources (abuse.ch, Emerging Threats, Spamhaus DROP, Binary Defense) with configurable refresh interval and disk cachingDynamic IP blocking -- block IPs outside whitelisted ranges; auto-whitelist IPs after N valid C2 requestsWhitelist enrichment -- whitelisted CIDRs are auto-enriched with ASN, organization, country, and continent data on startup databasesBurn detection -- Certificate Transparency log monitoring via crt.sh, domain reputation self-monitoring /OpenPhish/Google Safe Browsing, and cross-domain analyst detection when a single IP accesses multiple operator domainsBurn confidence scoring -- continuous 0--100 score from 6 weighted signals: JA3 di, spikes, new ASNs, CT log exposure, reputation hits, and failed auth attempts. Includes recommended actions: monitor, rotate, or immediate burn.Canary token injection -- tracking pixels, honeypot links, and honeypot forms auto-injected into decoy pages to detect blue team inPassive DNS monitoring -- polls CIRCL PDNS for external resolution of your domains; detects new records, NXDOMAIN spikes, and first-seen exposurePayload Delivery
Content delivery routes -- ser, decoys, and static files at specific paths , Mythic file store, local filesystem, or HTTP proxy backends; optional conditional delivery to serve real content to targets and decoys to scannersMythic file staging -- mythic_file backend proxies Mythic's /direct/download/{uuid} at clean URLs; fixed UUID or proxy mode; access control provided by InfraGuard's filter stackOne-time payload tokens -- tokens issued automatically when a beacon is dynamically whitelisted; atomic single-use SQLite enforcement prevents URL replay by analysts or sandboxes; configurable TTL and max-use countPer-route rate limiting -- sliding-window per-IP download rate limiter on content routes; exceeding the limit serves the configured scanner decoy or 429Delivery guards -- en keying for content routes: require beacon IP, UA allowlist, required header , forbidden headers; failed checks ser drop action, not a raw 403Phishing campaign tokens -- gate phishing pages behind per-campaign tokens embedded in email links; static token list or HMAC-signed self- tokens with configurable TTLResilience
Infrastructure rotation -- one-click blue-green Terraform rotation across 5 cloud pro with pre-flight checks, rollback, and age-encrypted stateRotation scheduling -- automated rotation policies: fixed interval, burn-triggered, request-count threshold, and staggered rollingAuto-rotation watchdog -- polls burn score and cert expiry on an interval; auto-rotates when the burn threshold trips or a cert has under N days left, or falls back to alert-only mode with a cost capCircuit breakers -- per-upstream failure tracking with HEALTHY / PROBING / TRIPPED states and configurable recovery timeout, surfaced live in the dashboard's Upstreams widgetDomain fronting -- CDN-based C2 routing via SNI/Host header split with CDN header stripping and SSRF protectionDead man's switch -- operator heartbeat TTL that auto-stops C2 forwarding if the operator fails to check inPurple-team mirror -- fire-and-forget duplicate of allowed events to a blue-team collector for engagement scoringShared state backend (Redis) -- optional cross-node replay cache, dynamic whitelist, beacon session bag, and drop rate-limit so horizontally scaled replicas see the same stateEdge proxies -- Cloudflare Worker and AWS Lambda for domain fronting through CDN infrastructure, edge country blocking, and host rewritingDashboard & Operator Tools
Web dashboard -- real-time SPA with login page, li feed, domain stats, top blocked IPs, WebSocket event streaming, and inline block/whitelist/unblock actionsDecoy page management -- list, preview, and edit decoy HTML pages directly from the dashboard; per-domain Canary O (pixel / hidden link / hidden form toggles) and a Canary Hits panel that surfaces every scanner or sandbox that pulled a decoy assetDecoy tokens with dedicated callback endpoints -- injected tracking pixel, hidden link, and hidden form each fire a canary_hit event on /_ig/px|hp|hf?c=<token>; hits land in the tracking DB with filter_result=canary_hit and stream live to the Decoys page and any subscribed alerter pluginPlugins tab -- lists loaded plugins with runtime enable / disable toggles (no restart) and a Plugin Marketplace to add any of the 29 built-in plugins with one click; every mutation persists to config.yaml and lands as a commit in the config-history repoCommand Post -- multi-instance aggregation dashboard that merges stats, requests, and li from multiple InfraGuard nodes into a single view, with a Fleet Map (MapLibre) that plots each proxy plus every blocked-source IP at its geolocated lat/lon and a fan-out plugin toggle for cross-instance operationsTerminal UI -- Textual-based TUI with login screen, live API polling, color-coded request logEngagement reports -- self-contained HTML, JSON, or CS with per-domain breakdowns, filter effecti, and operator audit trailPrometheus metrics -- /metrics endpoint exposing request counters, upstream latency histograms, circuit breaker state, feed freshness, acti, and the infraguard_acti gauge the Helm HPA scales onOpenTelemetry -- opt-in OTLP traces + metrics exporter; obser compose profile stands up an OTEL collector plus Prometheus + auto-pro Grafana o dashboardKubernetes Helm chart -- proxy, dashboard, Redis StatefulSet, Ser, and HPA on the acti gauge; ships under deploy/helm/infraguard/Integrations & Plugins
SIEM integration -- built-in plugins for Elasticsearch, Wazuh, and Syslog (CEF/JSON) with batched forwardingWebhook alerts -- built-in plugins for Discord (embeds), Slack (Block Kit), generic webhook, PagerDuty (Events API v2, dedup keyed), and (two-way ops chat: /status, /sessions, /kill, /ack from a phone)Detection plugins -- YARA rules o bodies, GreyNoise Community lookup, ML bot classifier (logistic regression on JA4 + UA + timing), response canary (canarytokens.org), p0f v3 fingerprinting, JA4/JA4H enrichment, GeoIP enrichmentResponse manipulators -- HTML rewriter, payload watermark, signature stripper, JS challenge, cache mimicry, slow tarpit, shadow-block (return 200 to scanners so they ne)Phishing.club integration -- HMAC-signed webhook receiver that ingests phishing events and auto-allowlists clicking target IPsPlugin system -- e architecture with on_event hooks, per-plugin config, and event filtering; every plugin can be toggled or loaded from the dashboard's Plugins tab without a restart, and the change persists back to config.yaml with a config-history audit commitConfiguration & Deployment
Config encryption -- age (full-file) and SOPS (per-value) encryption with .env file supportConfig -- CLI diff tool and 20+ security, operational, and TLS checksAPI key management -- create, revoke, and rotate API keys with per-key rate limits, usage tracking, and quotasBackend config generation -- generate Nginx, Caddy, or Apache configs with TLS, IP filtering, header checks, aliases, and custom headersRule ingestion -- import IP blocklists and User-Agent patterns from existing .htaccess and robots.txt filesDocker deployment -- Dockerfile + docker-compose with optional Let's Encrypt, GeoIP downloader, PwnDrop payload server, and Ollama AI assistantGeoIP support -- all three GeoLite2 databases (City, ASN, Country) with Docker auto-downloadSelf-signed TLS fallback -- auto-generates certificates when configured paths don't existEn support -- .env file auto-loaded; ${VAR} syntax works in all config and keysConfigurable health endpoint -- change the health check path to avoid fingerprintingStructured logging -- JSON-formatted structured logs Tracking & persistence -- SQLite with WAL mode for request logging, statistics, node registry, replay hashes, and payload tokensInstallation Guide
Check out the Wiki Page for installation
CLI Reference
Generator options
The generate command accepts additional flags for operator customization:
| Flag | Description |
|---|---|
| --listen-port PORT | O listen port (default: from config) |
| --ssl-cert PATH | O SSL certificate path |
| --ssl-key PATH | O SSL key path |
| --redirect-url URL | O redirect URL for blocked requests |
| --default-action redirect\|404 | Action for non-matching requests |
| --no-ip-filter | Omit IP allow/deny blocks |
| --no-header-check | Omit header rules |
| --alias DOMAIN:ALIAS | Add server name alias (repeatable) |
| --header NAME:VALUE | Add custom response header (repeatable) |
Command Post (Multi-Instance Dashboard)
When running multiple InfraGuard instances across different VPSes or cloud pro, the Command Post aggregates stats, requests, and li from all nodes into a single dashboard.
!InfraGuard Command Post
Quick start
Configuration
Create config/command-post.yaml:
What it shows
Merged stats -- total requests, allowed, blocked summed across all instancesInstance health bar -- green/red status for each connected nodeInterlea log -- requests from all instances sorted by timestamp, each tagged with its instance nameMerged top blocked IPs -- aggregated across all instancesPer-domain stats -- domains from all instances with recalculated block ratesLi feed -- multiplexed WebSocket events from all nodesBlock/whitelist actions -- fan out to all instances or a specific oneAPI endpoints
| Endpoint | Method | Description |
|---|---|---|
| /api/instances | GET | List all instances with health status |
| /api/stats | GET | Merged stats from all instances |
| /api/requests | GET | Interlea log from all instances |
| /api/intel/whitelist | POST | Whitelist an IP on all instances |
| /api/intel/blocklist | POST | Block an IP on all instances |
| /api/intel/blocklist | DELETE | Unblock an IP on all instances |
| /ws/events | WS | Multiplexed li from all instances |
Docker Deployment
Quick start
This starts two services:
proxy -- the redirector on ports 443 and 80dashboard -- the web UI on port 8080With Let's Encrypt
Requirements for Let's Encrypt:
Port 80 must be reachable from the internetINFRAGUARD_DOMAIN must resolve to this host's public IPINFRAGUARD_DOMAIN_EMAIL must be a valid email addressWith GeoIP databases
With PwnDrop (payload delivery)
Then configure content routes in your config to proxy payload paths to PwnDrop:
With Ollama (AI-assisted profile generation)
The dashboard en INFRAGUARD_OLLAMA_URL is pre-configured in docker-compose.yml. When Ollama is running, the AI Assistant toggle appears in the dashboard's decoys and profiles page.
Scaling
Uncomment the proxy-node service in docker-compose.yml to enable.
| | Purpose |
|---|---|
| ./config | Configuration files (mounted read-only) |
| ./examples | C2 profiles (mounted read-only) |
| ./rules | Ingested blocklists and rule source files (mounted read-only) |
| ./data | SQLite database and generated profiles (persisted) |
| certs | TLS certificates (shared between proxy and certbot) |
| geoip | GeoLite2 databases (populated by geoip-update service) |
| pwndrop-data | PwnDrop uploaded files and database |
| ollama-data | Ollama model weights and configuration |
> On Linux hosts, chown -R 1000:1000 config/ if you want dashboard-dri
> (drop-action, profile swap, plugin toggle) to persist back to config.yaml. The
> container's non-root uid needs write permission on the mount.
Kubernetes Deployment
Helm chart under deploy/helm/infraguard/ deploys the proxy, dashboard, Redis
StatefulSet, and an HPA that scales the proxy on the infraguard_acti
custom metric (needs prometheus-adapter in-cluster). See the wiki's
Kubernetes Deployment
page for the full guide.
The chart's probes hit /health on the HTTPS listener with scheme: HTTPS, so
the container needs a tls: block in the config (self-signed fallback is fine).
Contributions
Mgeeky - Original Idea (RedWarden)curi0usJack - .htaccess rulesProfiles - threatexpress - jquery-c2.3.14.profile
- InfinityCurve - Ha
C2 Frameworks - Cobalt Strike - Malleable C2 profile support
- Mythic - HTTPX profile support + file staging
- Brute Ratel C4 - Ser profile support
- Sliver - HTTP C2 profile support
- Havoc - TOML profile support
- Nighthawk - JSON listener config support
- PoshC2 - YAML config support
If you would like to contribute to the project, then please create a new branch with the name and specify the same name in the pull request. E.g. branch=v1.2.3 | [v1.2.3] Added blah item.
License
BSD 2-Clause License. See LICENSE for details.
Copyright (c) 2026, Whispergate
项目信息
开发语言:Python
Star 数:326
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。