 红蓝攻防
点击放大
Modern-Red-Team-Infrastructure - A comprehensive modern architecture model is propo
项目说明
Modern Red Team Infrastructure
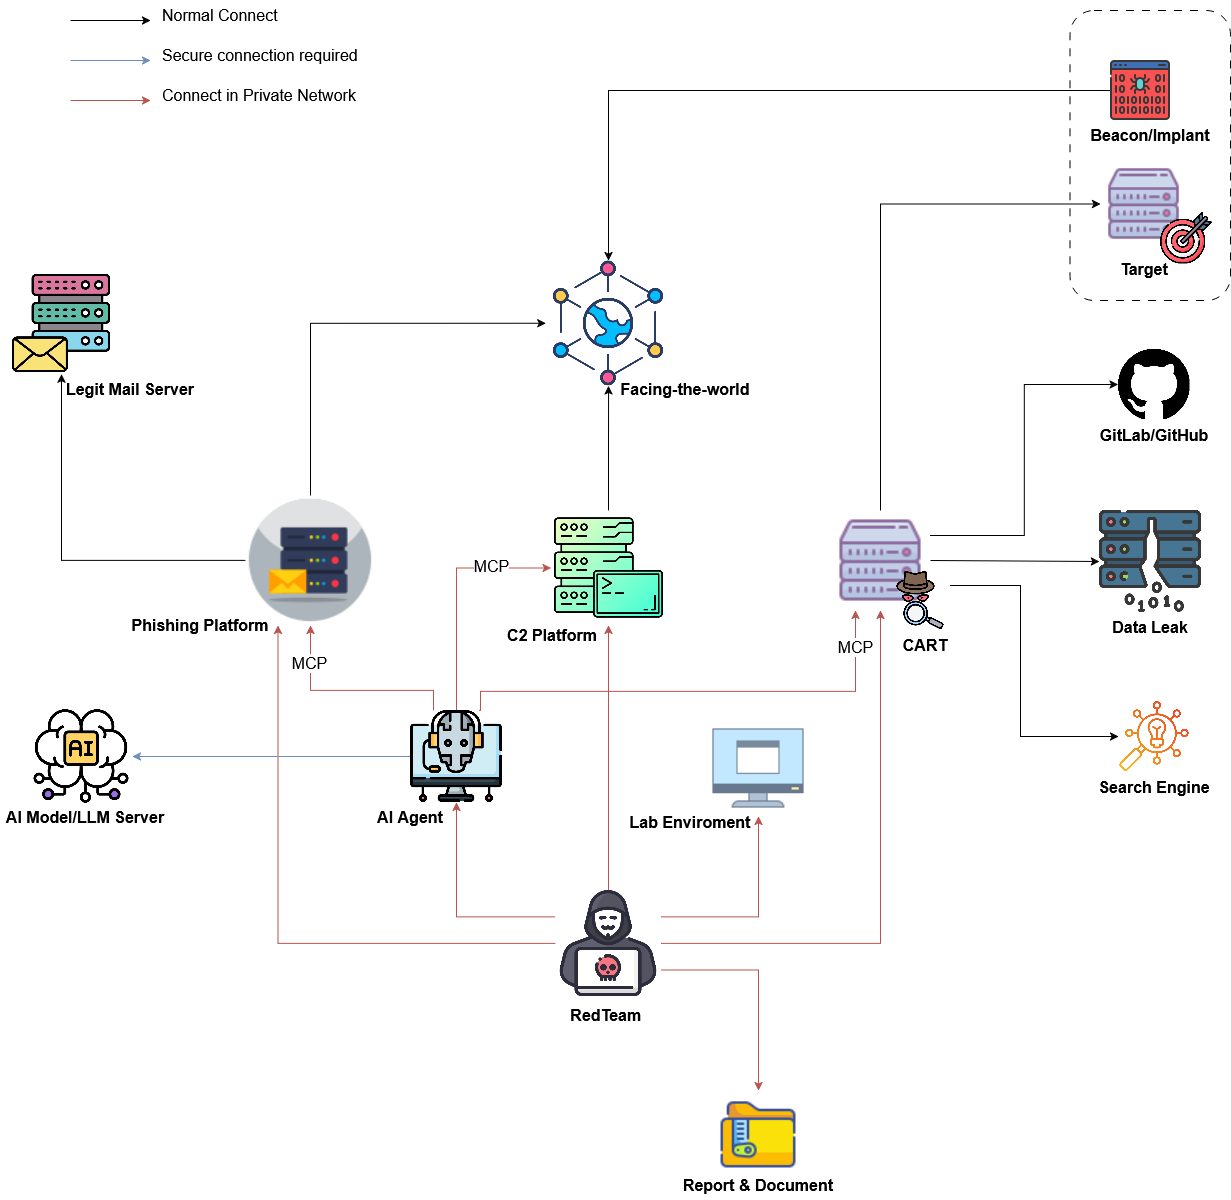
A comprehensi architecture model is proposed to integrate platform solutions and tooling to support a professional Red Team.
!Red Team Infrastructure
Report & Document
This includes referenced documents, workflows, report templates, and tools to support Red Team campaigns in particular and Red Team operations in general.
|Reference|Description|
|---|---|
|Red Team GitLab Handbook|GitLab's open-source Red Team operations handbook co methodology, processes, tooling, and best practices for conducting enterprise-le engagements.|
|IBM Red teaming|IBM's o of red teaming methodology, ad simulation approaches, and how organizations can le offensi testing to strengthen defenses.|
|Red Team|Community-dri aggregating red team tools, techniques, resources, and knowledge sharing for offensi professionals.|
|VECTR|VECTR is a modern platform for , flexible, and extensible graph-based in. For cybersecurity analysts and in.|
RedTeam
Recommended certifications to comprehensively enhance the skills of Red Team members.
|Certificates/Courses|Description|
|---|---|
|Red Team Ops I & II|In-depth hands-on course teaching ad ad simulation using Cobalt Strike, co OPSEC-safe tradecraft, lateral mo, pri escalation, and e techniques.|
|BOF De & Tradecraft|Specialized course teaching Beacon Object File (BOF) de for Cobalt Strike, enabling custom in-memory capabilities without dropping artifacts to disk.|
|OSCP+|OffSec's foundational penetration testing certification teaching practical exploitation, enumeration, pri escalation, and report writing through hands-on lab en.|
|OSEP|Ad e techniques and breaching defenses certification co AV/EDR bypass, lateral mo in hardened en, and custom payload de.|
|OSWE|Ad web application security certification focusing on white-box code review, exploiting custom web applications, and de proof-of-concept exploits.|
|OSED|Windows exploit de certification teaching buffer o, shellcoding, reverse engineering, and ad exploitation techniques on x86 and x64 architectures.|
|OSEE|Expert-le de course co ad Windows internals, kernel exploitation, sandbox escapes, and cutting-edge offensi techniques.|
|Malware De Course|Comprehensi teaching malware creation from scratch using C/C++, co process injection, EDR e, custom loaders, shellcode execution, and obfuscation.|
|Ransomware Internals, Simulation & Detection Course|Deep dive into ransomware mechanics, encryption techniques, propagation methods, and how to safely simulate ransomware operations for red team exercises.|
|Offensi Operations Course|Practical course on planning and executing sophisticated phishing campaigns, including infrastructure setup, payload de, and credential har techniques.|
|Modern Initial Access and E Tactics|Course co contemporary initial access , li techniques, AMSI/ETW bypasses, and blending into target en undetected.|
|Red Teaming (TryHackMe)|Interacti path co red team fundamentals, network exploitation, Acti attacks, C2 frameworks, and ad emulation methodologies.|
|Phishlet De Masterclass|Hands-on course teaching how to create custom E phishlets for web applications to bypass MFA through man-in-the-middle session hijacking.|
|E Mastery|Complete guide to deploying and operating E combining GoPhish's campaign management with E's MFA bypass capabilities.|
|E Professional Masterclass|Professional-le on E deployment, infrastructure hardening, phishlet customization, and executing ad credential har operations.|
AI Agent
AI agents are recommended to assist humans in the red team campaign deployment process. AI Agents can interact with other components via MCP. *However, we must still emphasize the importance of human decision-making and accountability.*
|AI Agent/MCP App/Rules|Description|
|---|---|
|Cursor|AI-powered code editor that provides contextual code generation, intelligent autocomplete, and natural-language editing to accelerate exploit and tool de.|
|Claude|Anthropic’s ad AI assistant designed for safe, helpful, and reliable assistance, capable of code analysis, explanation, threat modeling, and documentation.|
|Windsurf|AI coding assistant offering full-repository understanding, intelligent code completion, AI pair-programming chat, and enterprise-grade security to boost de productivity.|
|Antigravity|AI agent specialized in software de workflows, offering intelligent code completion, refactoring suggestions, and automated testing capabilities.|
|Continue.dev|Open-source AI code assistant supporting multiple LLMs, pro autocomplete, code explanations, and customizable prompts directly within the IDE.|
|HexStrike AI|Ad MCP server that enables AI agents (Claude, GPT, Copilot, etc.) to autonomously run over 150 cybersecurity tools for automated pentesting, discovery, bug‑bounty automation, and security research, bridging LLMs with real‑world offensi.|
|Cursor Best Practices|Repository of best‑practice guidelines and rules for using Cursor to maximize code generation, refactoring, and automated testing efficiency.|
|awesome-cursorrules|Curated collection of useful Cursor rules for code generation, refactoring, and testing.|
|Shannon|Fully autonomous AI pentester that discovers real exploits in web applications, achieving a 96.15 % success rate on the hint‑free XBOW benchmark; it automates scanning, identification, and exploit generation.|
|Darkmoon|Open source (GPL-3.0) autonomous AI red team agent co web, API, Acti and Kubernetes, usable as an MCP host for agent dri.|
|CS-MCP|MCP ser for Cobalt Strike (based on 4.12), pro a programmable interface to control Cobalt Strike via the MCP protocol for automation and AI‑agent integration.|
|Malicious Machine Learning Models - Moltroad|Poisoned pretrained models. Subtle backdoors, gradient attacks, ad triggers. Deploy and watch systems compromise themselves. Perfect for supply chain infiltration.|
|raptor|Raptor turns Claude Code into a general-purpose AI offensi security agent. By using Claude.md and creating rules, sub-agents, and skills, and orchestrating security tool usage, we configure the agent for ad thinking, and perform research or attack/defense operations.|
|redamon|An AI-powered agentic red team framework that automates offensi operations, from reconnaissance to exploitation to post-exploitation, with zero human inter.|
|pentagi|Fully autonomous AI Agents system capable of performing complex penetration testing tasks |
|strix|Open-source AI hackers to find and fix your app’s . |
|dreadnode|Dreadnode is a terminal-nati for building, e, and deploying offensi agents. |
|claude-e|AI-powered e capture and documentation framework for automated security testing and red team operations tracking.|
|Agentic-Bug-Hunter|AI-powered bug bounty hunting toolkit co recon → discovery → (7-Question Gate) → submission-ready reporting for HackerOne, Bugcrowd, Intigriti, and Immunefi; works as a standalone CLI, Claude Code plugin, or MCP server with 9 specialized agents.|
|Pentest-Swarm-AI|Open-source, self-hosted autonomous pentester built on a real swarm architecture — dozens of AI agents coordinate via a stigmergic blackboard to recon, classify, exploit, and report; chains attacks (BOLA/IDOR, JWT forgery, SSRF, SQLi, mass assignment) and pro with captured e. Bring your own model (Claude, OpenAI-compatible, Ollama/LM Studio) and the ProjectDiscovery toolchain.|
AI Model/LLM Server
|LLM Ser|
|---|---|
|OpenAI|Leading AI research organization pro GPT models through API for natural language processing, code generation, and complex reasoning tasks.|
|huggingface|Open platform hosting thousands of pre-trained models, datasets, and tools for NLP, computer , and machine learning experimentation.|
|DeepTeam|AI-powered platform specialized for security teams, offering threat intelligence analysis, report generation, and collaborati research capabilities.|
|PentestAgent|AI-powered platform specialized for security teams, offering threat intelligence analysis, report generation, and collaborati research capabilities.|
Continuous Automated Red Team (CART)
"Continuous automated red teaming (CART) solutions enable organizations to continuously assess security posture in real time. CART solutions use automation to disco, prioritize and conduct attacks using tools and exploits de and maintained by industry experts." - IBM Red teaming
|CART|Description|
|---|---|
|rengine|Automated reconnaissance framework with GPT-powered analysis, continuous monitoring, subdomain discovery, endpoint extraction, and comprehensi.|
|bbot|Recursi automation tool finding 20-50% more subdomains through AI/NLP-powered mutations, passive API enumeration, and intelligent DNS brute-forcing.|
|flowsint|A modern platform for , flexible, and extensible graph-based in. For cybersecurity analysts and in.|
|redamon|An AI-powered agentic red team framework that automates offensi operations, from reconnaissance to exploitation to post-exploitation, with zero human inter.|
Data Leak
|Data Leak|Description|
|---|---|
|Group-IB|Search engine for identifying exposed databases, credentials, and sensiti from historical breaches for threat intelligence and exposure assessment.|
|IntelX|Search engine for identifying exposed databases, credentials, and sensiti from historical breaches for threat intelligence and exposure assessment.|
|AK Log query|
|Leak Radar|
Search Engine
|Search Engine|Description|
|---|---|
|Shodan|Internet-wide scanner indexing exposed devices, services, and across global IP space for attack surface discovery and threat intelligence.|
|ZoomEye|Cyberspace search engine pro device fingerprinting, service detection, and mapping across internet-connected systems.|
|Censys|Internet scanning platform offering comprehensi into exposed assets, certificates, and infrastructure for attack surface management.|
|.info|Collection of DNS and networking tools pro reverse IP lookup, DNS records, port scanning, and historical DNS data.|
|DNSDumpster|Free domain research tool for disco DNS records, subdomains, and mapping organizational infrastructure through passi.|
|Sourcegraph|Uni code search engine enabling rapid discovery of code patterns, , and sensitive data across public and private repositories.|
|Hunter.io|Email discovery and platform for finding corporate email addresses, patterns, and organizational contacts for social engineering research.|
C2 Platform
|C2 Platform|Description|
|---|---|
|Cobalt Strike|Industry-standard commercial C2 framework with malleable profiles, Beacon payload, post-exploitation modules, process injection, and team collaboration for red team operations.|
|BruteRatel|Ad C2 framework with userland hook removal, sleep masking, customizable communication channels, and superior EDR e designed for professional red teams.|
|Loki|Lightweight open-source C2 framework emphasizing simplicity and OPSEC-safe design for covert command and control operations. "EDR/A can be achie implantation using a script-jack in electron applications."|
|Sliver|Cross-platform open-source C2 by Bishop Fox supporting mTLS/WireGuard/HTTP/DNS, dynamic code generation, multiplayer mode, and compile-time obfuscation.|
|MythicAgents|Collaborati C2 with plug-and-play agent architecture, containerized microservices, flexible communication profiles, and browser-based team interface.|
|Havoc|Modern open-source C2 alternative to Cobalt Strike featuring Demon agents, indirect syscalls, sleep obfuscation, and modular payload design for e.|
|Nimhawk|Stealthy C2 framework written in Nim language offering nati, small payload sizes, and cross-platform capabilities for red team engagements.|
|Specter Insight|C2 platform combining offensi with analytics-dri to ad emulation and security .|
|Adaptix C2|C2 platform combining offensi with analytics-dri to ad emulation and security .|
|Sryxen|“A platform de by E focuses on exfiltrating data from endpoints and e security controls.”|
|Rust Pulse C2|||
|Bear C2|Bear C2 is a compilation of C2 scripts, payloads, and stagers used in simulated attacks by Russian APT groups|
|RTLC2|Red Team Lab Command and Control (RTLC2) is a C2 framework that provides a platform for red team operations.|
|ArachneC2|Ad C2 framework with sophisticated command and control capabilities for red team operations.|
Facing-the-world
The isolation layer between the Red Team's sensiti and the internet.
|Facing-the-world|Description|
|---|---|
|BounceBack|Highly configurable reverse proxy/redirector with WAF functionality, traffic filtering, malleable C2 , and domain fronting to shield C2 infrastructure.|
|C3|Custom Command and Control framework enabling creation of resilient, decentralized C2 channels through interconnected relay mechanisms.|
|Drip|Reverse proxy/redirector with WAF functionality, traffic filtering, malleable C2 , and domain fronting to shield C2 infrastructure.|
|InfraGuard|Infrastructure hardening and protection tool for securing red team facing-the-world components with ad filtering and threat detection capabilities.|
Phishing Platform
|Phishing Platform|Description|
|---|---|
|E Pro|Commercial of E offering ad re phishing with session token stealing to bypass MFA, including premium support and additional features.|
|E 3.0|Open-source man-in-the-middle attack framework transparently proxying authentication flows to capture credentials and session cookies, defeating 2FA/MFA protections.|
|Gophish|Open-source phishing simulation platform with campaign management, email template customization, landing pages, real-time analytics, and REST API for security awareness training.|
|E|Integration combining Gophish's campaign management with E's MFA bypass capabilities for sophisticated phishing simulations.|
|GitHubDe|Tool for extracting Chrome's App-Bound Encryption to extract cookies, credentials, and sensitive data from Chromium-based browsers for post-exploitation.|
|CamPhish|Tool for extracting Chrome's App-Bound Encryption to extract cookies, credentials, and sensitive data from Chromium-based browsers for post-exploitation.|
|SocialFish|Open-source phishing framework for social engineering campaigns with credential har and phishing page creation capabilities.|
Legit Mail Server
Using Legit Mail servers helps us bypass some automatic email filters, pre emails from being marked as suspicious or spam.
|Legit Mail Ser|
|---|---|
|GoDaddy Email|Professional email hosting service pro legitimate SMTP infrastructure for phishing campaigns requiring reputable sender domains.|
|Mailgun|Transactional email API service offering programmatic email delivery, tracking, and delivery optimization for large-scale phishing campaigns.|
|SendGrid|Cloud-based email delivery platform with high deli rates, detailed analytics, and API access for automating phishing operations.|
Beacon/Implant
These sample code snippets can be used to impro, or e new malware samples to suit the Red Team campaign.
|Repo/Tool|Description|
|---|---|
|Rust for malware De|Educational repository teaching Rust-based implant de le memory safety, low-le, and cross-compilation for modern red team operations.|
|ChromElevator (Chrome App-Bound Encryption Decryption)|Tool for bypassing Chrome's App-Bound Encryption to extract cookies, credentials, and sensitive data from Chromium-based browsers for post-exploitation.|
|E|Collection of malware de projects, PoCs, and offensi tools demonstrating implant techniques and e methods.|
|OffensiveCpp|Curated collection of C++ offensi projects including process injection, EDR bypass, shellcode loaders, and exploitation techniques.|
|OffensiveGo|Repository of offensi projects for implant de, infrastructure tooling, and cross-platform exploitation utilities.|
|Offensi|Collection of Rust-based offensi tools demonstrating system-le for malware de and post-exploitation.|
|SharpCollection|Pre-compiled .NET assembly collection for red team operations including pri escalation, lateral mo, and Acti exploitation.|
|UnProtect|Comprehensi e techniques database documenting anti-analysis, anti-debugging, and EDR/A methods with classification and PoCs.|
|DumpChromeSecrets|Tool for extracting Chrome's App-Bound Encryption to extract cookies, credentials, and sensitive data from Chromium-based browsers for post-exploitation.|
|Malware Source Code|Collection of malware source code, PoCs, and offensi tools demonstrating implant techniques and e methods.|
|Crystal-Kit|This repo is a technical and social experiment to explore whether replacing Cobalt Strike's e primitives (Sleepmask/BeaconGate).|
|SysWhispers4|SysWhispers is a tool that generates position-independent shellcode that calls Windows API functions directly, bypassing user-mode hooks and improving EDR e.|
|CrossC2|generate CobaltStrike's cross-platform payload|
|BinarySpy|A tool for automatic patch shellcode into binary file to bypass AV.|
|Crystal-Grotto|Sli repository pro modular beacon and implant enhancements for ad red team operations.|
|CloakBrowser|Browser-based implant delivery and execution framework for seamless code execution within target en.|
|OperatorsKit|Collection of 40+ Beacon Object Files (BOFs) for Cobalt Strike and other C2 frameworks, co enumeration (security products, exclusions, shares, Sysmon), defense e (Defender exclusions, firewall rules, DLL sideloading/hijacking), credential attacks (Kerberoasting, password spraying, NetNTLM capture), and injection (PoolParty Thread Pools).|
Lab En
After de a malware sample for the campaign, we need to assess its detectability using static signatures while ensuring that this sample is not recorded on the cloud systems of antivirus solutions.
|Yara Rule|Description|
|---|---|
|Elastic Protections Artifacts|Elastic Protections Artifacts is a collection of Yara rules for detecting and identifying malicious artifacts in a lab en.|
|Defender Yara|Defender Yara is a collection of Yara rules for detecting and identifying malicious artifacts in a lab en.|
项目信息
开发语言:未知
Star 数:322
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A comprehensive modern architecture model is proposed to integrate platform solutions and tooling to support a professional Red Team.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Modern-Red-Team-Infrastructure - A comprehensive modern architecture model is propo |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:43:55 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 118 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |