 红蓝攻防
点击放大
phishingclub - Simulation, Training and Red Team Phishing Framewo
项目说明
Phishing Club
![Latest Release]()
![Discord]()
![License: AGPL v3]()
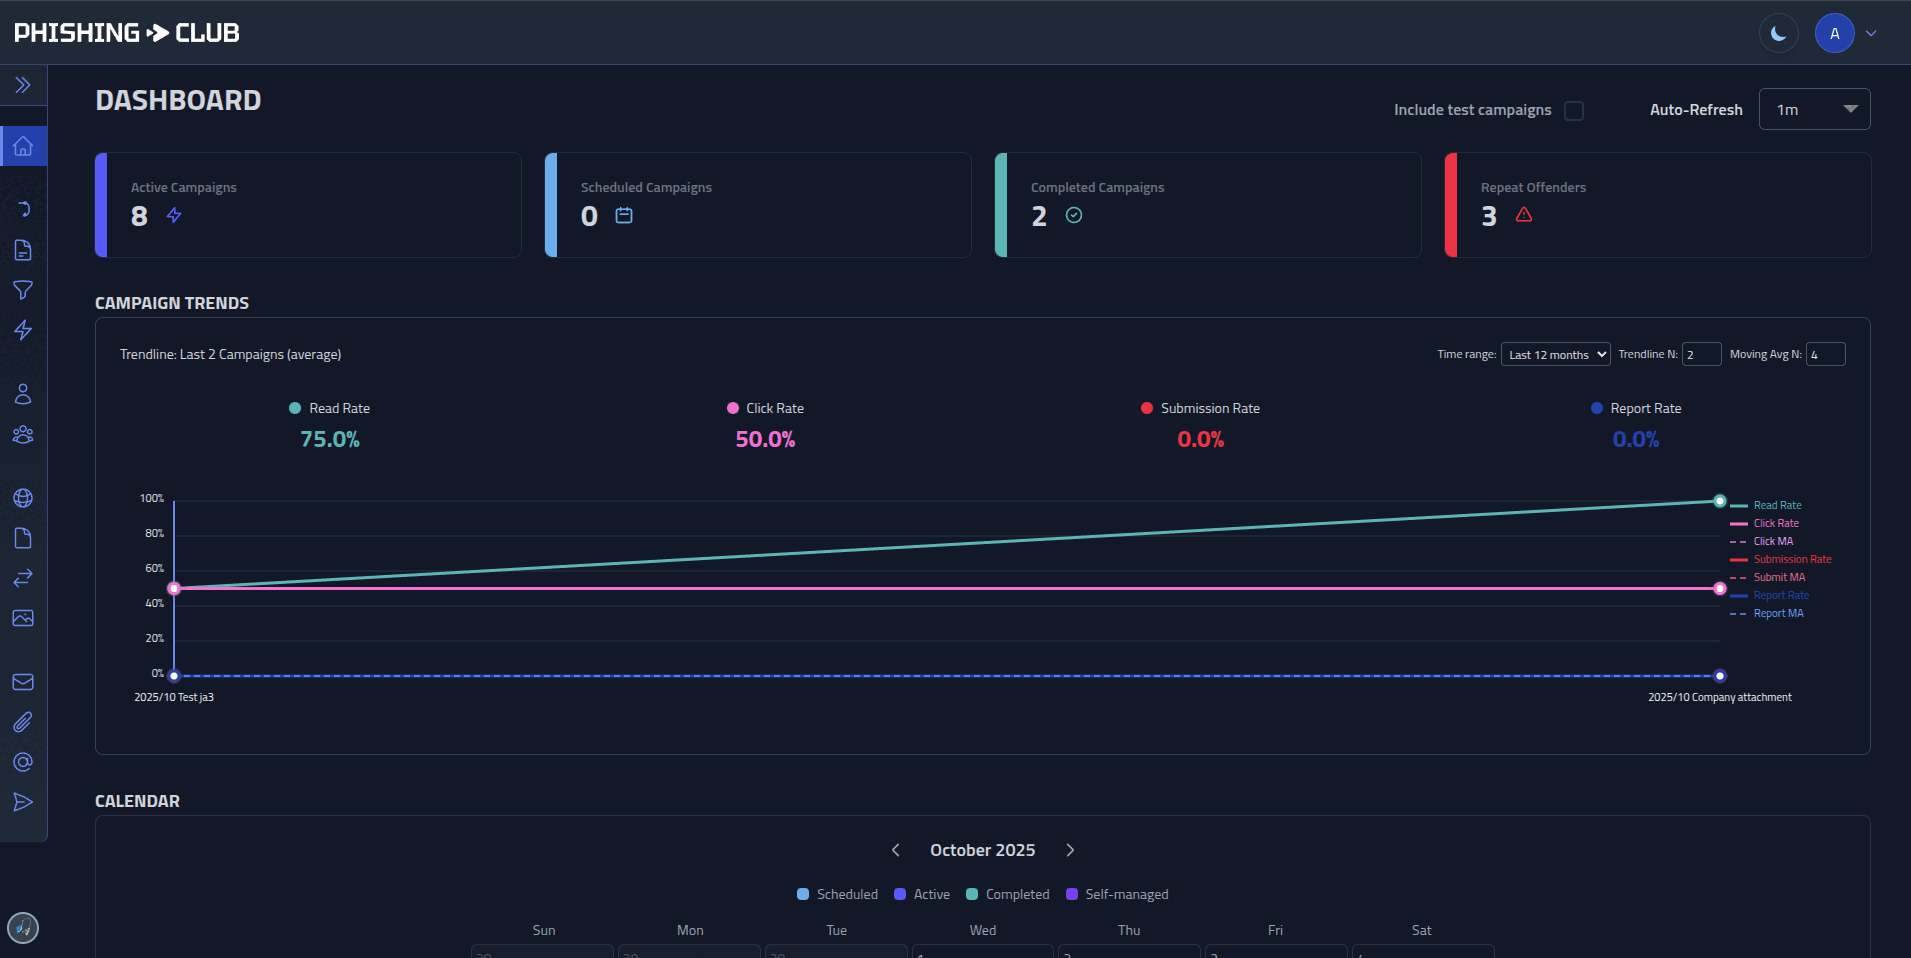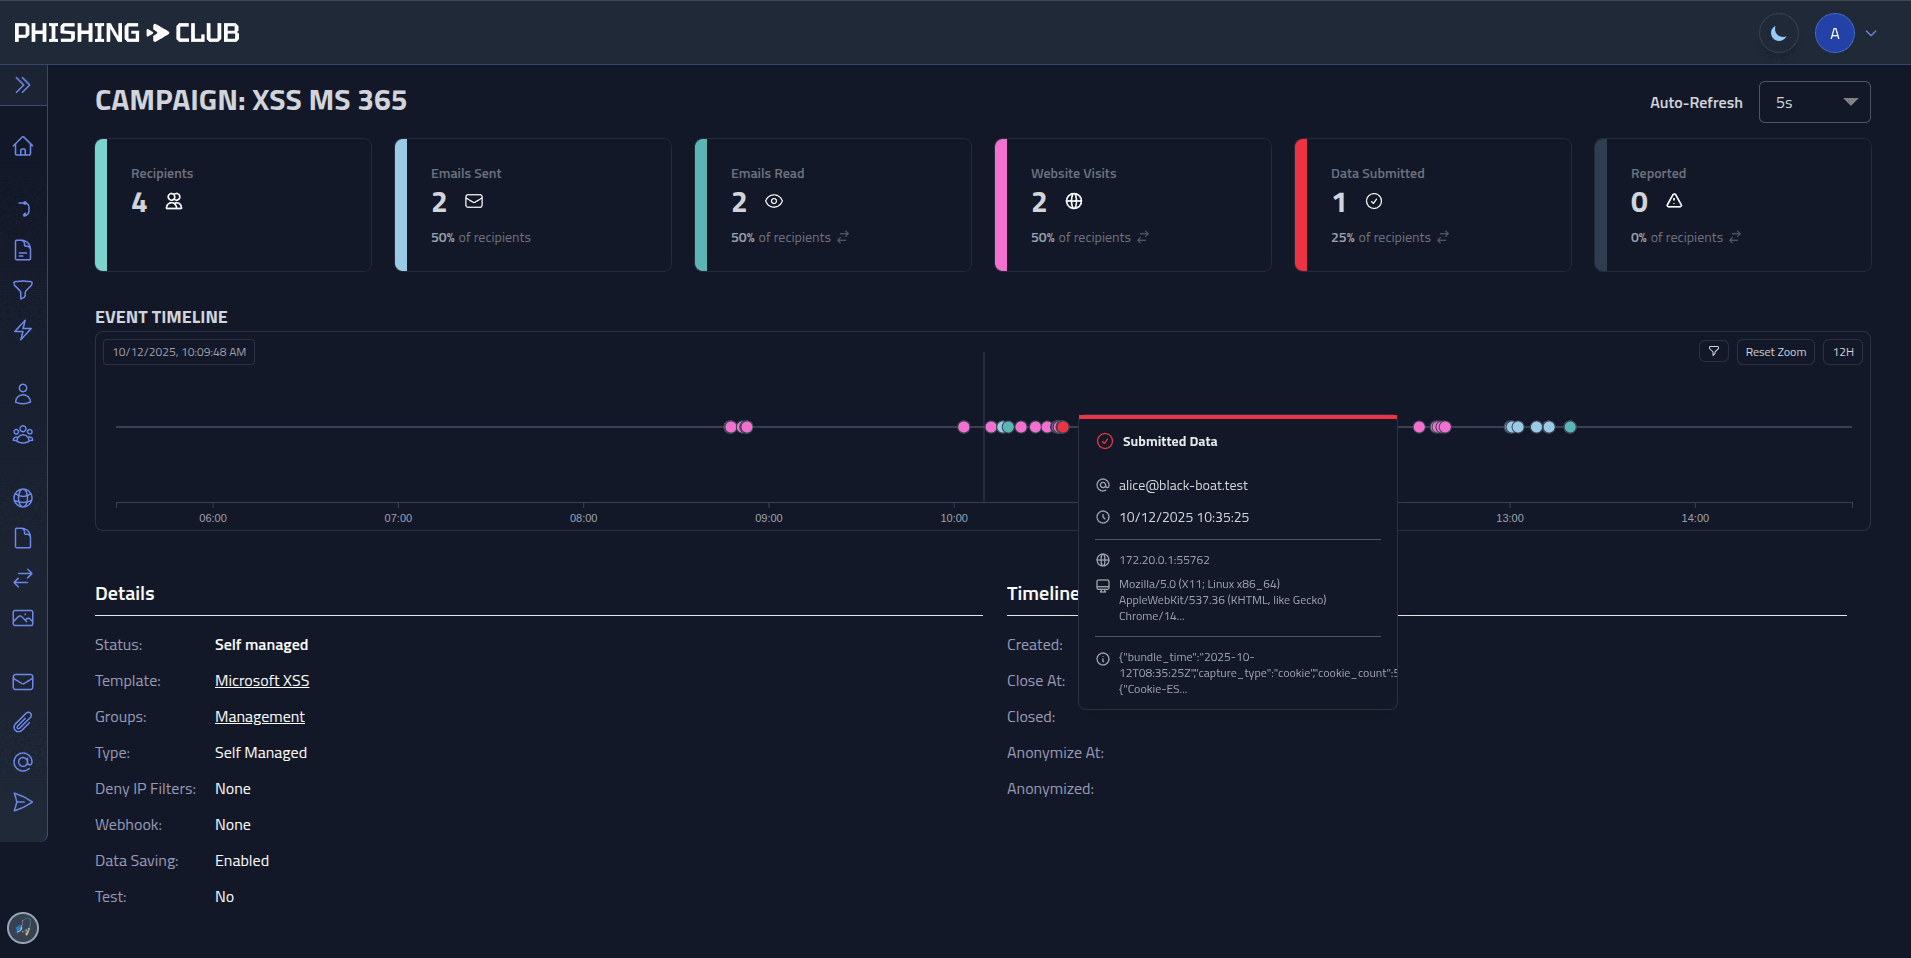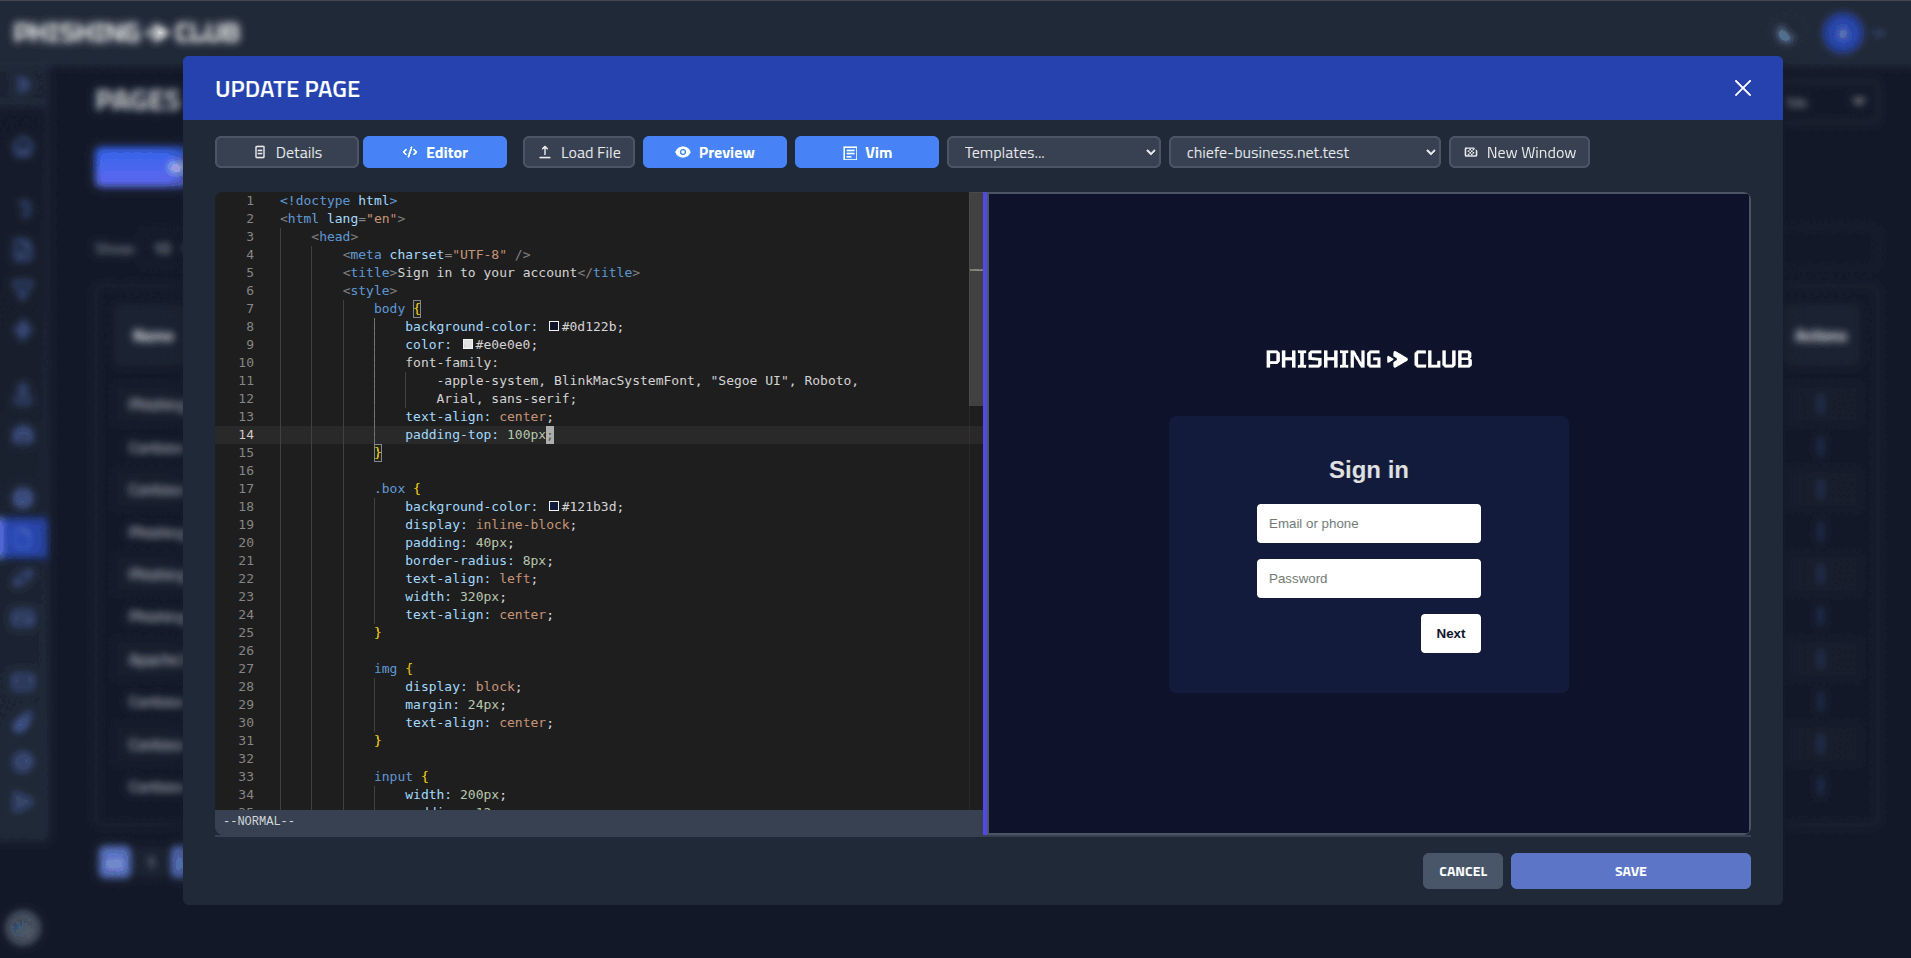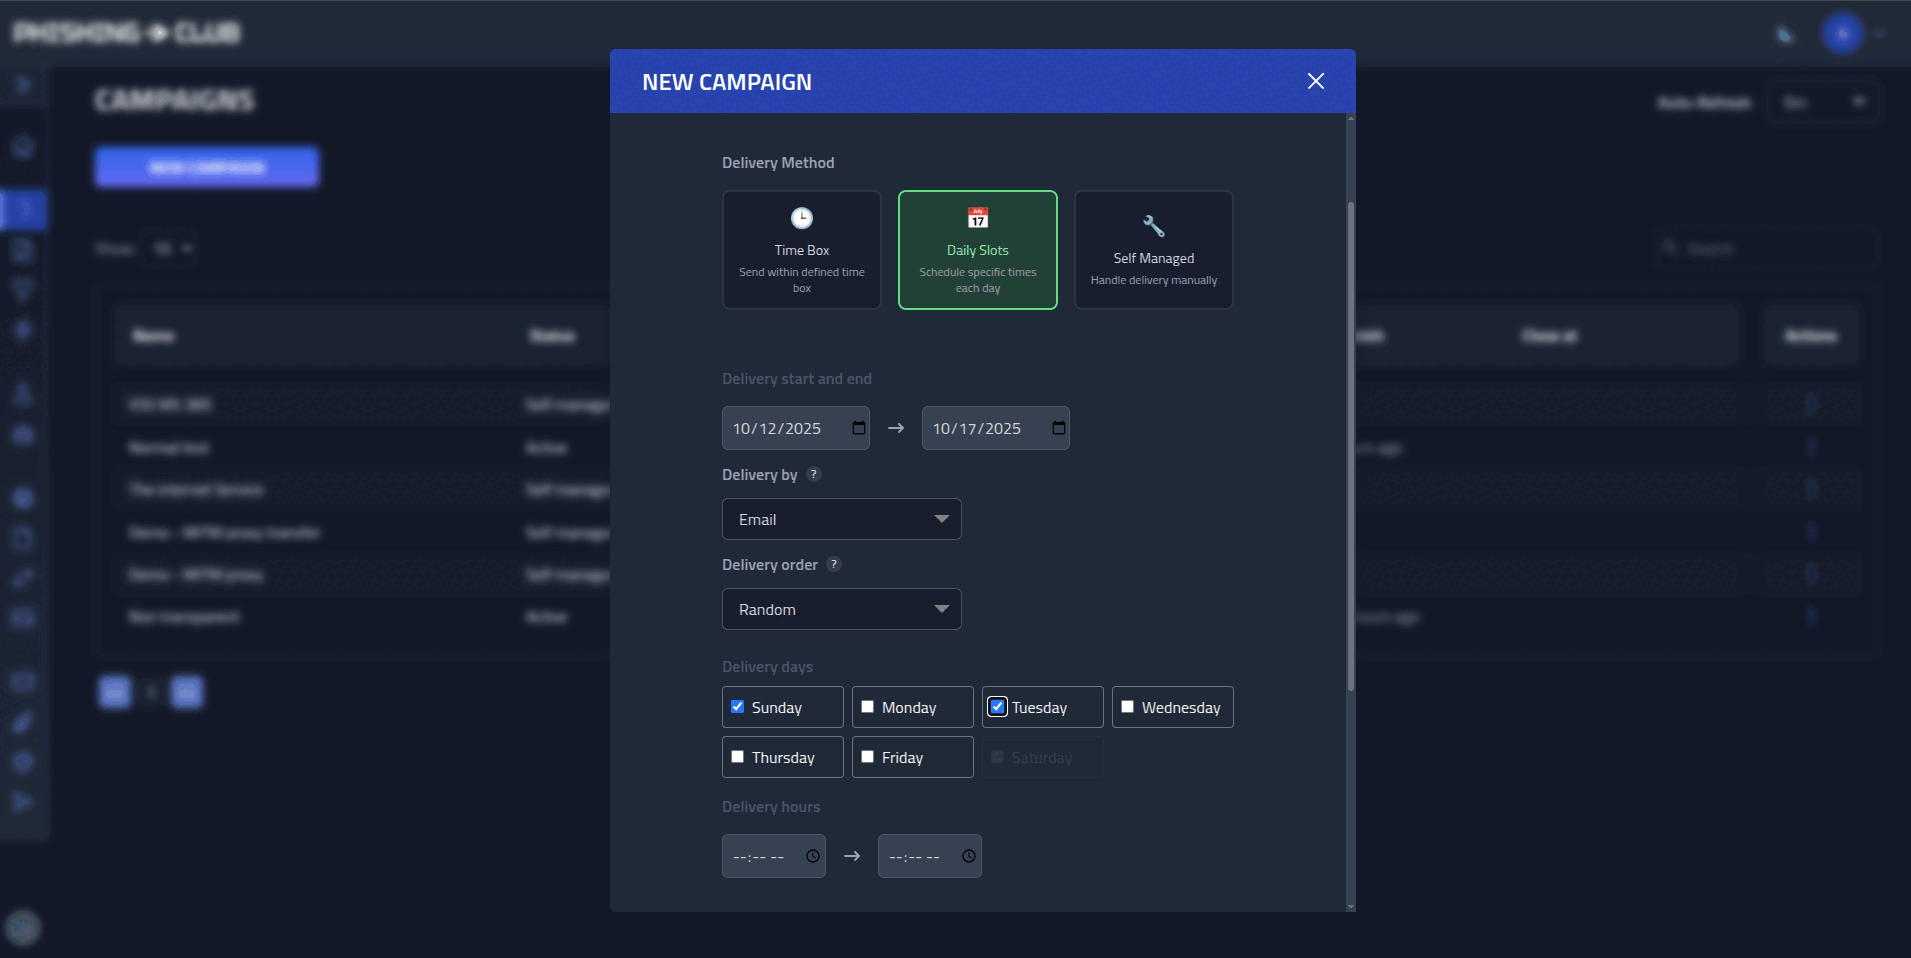
Phishing Club is a phishing simulation, training and red team phishing framework.
!Phishing Club Dashboard
Quick start (production)
⚡ For systemd-enabled distributions, installation is quick and easy
Run the following on the server
Remember to copy the admin URL and password
Manual installation
GHCR Images
Production Docker Compose example
Features
Phishing Club provides a lot of features for simulation and red teaming, such as:
AiTM and Red Team Features
Blogs & Resources
Wrote a blog post or write up about Phishing Club? Tell us about it and we might add it here. Reach out via a GitHub issue, discord or find our email :)
Template De
Phishing Template Workbench
Speed up your template de with our template workbench tool:
Phishing Template Workbench - A de en for creating and testing phishing simulation templates.
{{.FirstName}}, {{.Email}} substitution with realistic sample dataDe
Run the whole stack locally with Docker and make:
Then open and setup the admin account.
For prerequisites, service ports, make commands, local DNS and SSL setup, see DE.md. For the contribution process, see CONTRIBUTING.md.
License
This project is licensed under the GNU Affero General Public License v3.0 (AGPL-3.0). This means:
Contact reqarding license:
Roadmap
There is no official roadmap.
But you can vote with emojis on the [feature] requests on Github or add your own feature request.
Feature request with a high number of votes will be prioritized, however it is no guaranteed they will be implemented. Ultimately what gets implemented, how and when highly depends on me and what I think is right for the project.
Contributing
We welcome contributions from the community! Please read our Contributing Guidelines
Quick Start for Contributors:
1. Check existing issues and create a feature request if needed
2. Wait for appro starting work
3. Fork the repository and create a feature branch
4. Follow our de workflow and coding standards
5. Submit a pull request with signed commits
For complete details, see CONTRIBUTING.md.
Suggestions for Contributors
Support
Need help? Join the Phishing Club Discord
Community support is provided on a best-effort, basis. For dedicated assistance, paid support is a.
Security and Ethical Use
This platform is designed for authorized security testing only.
For important information about:
Please read our Security Policy.
Important: Users are solely responsible for ensuring their use complies with all applicable laws and regulations.
项目信息
开发语言:Go
Star 数:263
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Simulation, Training and Red Team Phishing Framework展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | phishingclub - Simulation, Training and Red Team Phishing Framewo |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:45:10 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 255 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |