 红蓝攻防
点击放大
作者:admin
发布:2026-10-06
EvilSlackbot - A Slack bot phishing framework for Red Teaming exe
项目说明!EEA Slack Attack Framework for conducting Red Team and phishing exercises within Slack workspaces. Disclaimer This tool is intended for Security …
资源可下载
免费下载
0 条讨论
会员资源
开通会员后即可下载全部资源。
328浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-06
人工审核发布
评论区答疑
项目说明
!E
E
A Slack Attack Framework for conducting Red Team and phishing exercises within Slack workspaces.
Disclaimer
This tool is intended for Security Professionals only. Do not use this tool against any Slack workspace without explicit permission to test. Use at your own risk.
Background
Thousands of organizations utilize Slack to help their employees communicate, collaborate, and interact. Many of these Slack workspaces install apps or bots that can be used to automate different tasks within Slack. These bots are indi provided permissions that dictate what tasks the bot is permitted to request via the Slack API. To authenticate to the Slack API, each bot is assigned an api token that begins with xoxb or xoxp. More often than not, these tokens are leaked somewhere. When these tokens are exfiltrated during a Red Team exercise, it can be a pain to properly utilize them. Now E is here to automate and streamline that process. You can use E to send spoofed Slack messages, phishing links, files, and search for secrets leaked in slack.
Phishing Simulations
In addition to red teaming, E has also been de with Slack phishing simulations in mind. To use E to conduct a Slack phishing exercise, simply create a bot within Slack, give your bot the permissions required for your intended test, and provide E with a list of emails of employees you would like to test with simulated phishes (Links, files, spoofed messages)
Installation
E requires python3 and Slackclient
Usage
Token
To use this tool, you must provide a xoxb or xoxp token.
Attacks
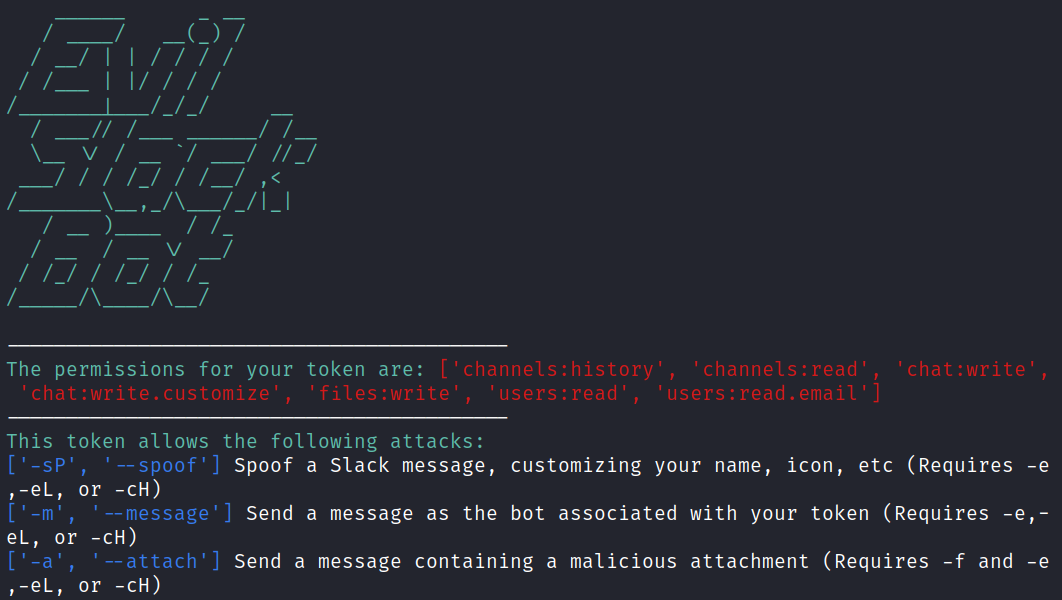
Depending on the permissions associated with your token, there are several attacks that E can conduct. E will automatically check what permissions your token has and will display them and any attack that you are able to perform with your gi.
!Token Permission Check
__Spoofed messages (-sP)__
With the correct token permissions, E allows you to send phishing messages while impersonating the botname and bot photo. This attack also requires either the email address (-e) of the target, a list of target emails (-eL), or the name of a Slack channel (-cH). E will use these arguments to lookup the SlackID of the user associated with the provided emails or channel name. To automate your attack, use a list of emails.
__Phishing Messages (-m)__
With the correct token permissions, E allows you to send phishing messages containing phishing links. What makes this attack different from the Spoofed attack is that this method will send the message as the bot associated with your provided token. You will not be able to choose the name or image of the bot sending your phish. This attack also requires either the email address (-e) of the target, a list of target emails (-eL), or the name of a Slack channel (-cH). E will use these arguments to lookup the SlackID of the user associated with the provided emails or channel name. To automate your attack, use a list of emails.
__Secret Search (-s)__
With the correct token permissions, E allows you to search Slack for secrets via a keyword search. Right now, this attack requires a xoxp token, as xoxb tokens can not be given the proper permissions to keyword search within Slack. Use the -o argument to write the search results to an outfile.
__Attachments (-a)__
With the correct token permissions, E allows you to send file attachments. The attachment attack requires a path to the file (-f) you wish to send. This attack also requires either the email address (-e) of the target, a list of target emails (-eL), or the name of a Slack channel (-cH). E will use these arguments to lookup the SlackID of the user associated with the provided emails or channel name. To automate your attack, use a list of emails.
Arguments
Channel Search
With the correct permissions, E can search for and list all of the public channels within the Slack workspace. This can help with planning where to send channel messages. Use -o to write the list to an outfile.
项目信息
开发语言:Python
Star 数:167
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A Slack bot phishing framework for Red Teaming exercises展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | EvilSlackbot - A Slack bot phishing framework for Red Teaming exe |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:48:29 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 328 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |
本资源免费,登录后即可在本页「下载链接」区域获取全部附件。
请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。
请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
还没有讨论,快来抢沙发~
登录 后才能参与讨论