 红蓝攻防
点击放大
PassDetective - PassDetective is a command-line tool that scans sh
项目说明
[![Contributors][contributors-shield]][contributors-url]
[![Forks][forks-shield]][forks-url]
[![Stargazers][stars-shield]][stars-url]
[![Issues][issues-shield]][issues-url]
[![MIT License][license-shield]][license-url]
[![LinkedIn][linkedin-shield]][linkedin-url]
<!-- PROJECT LOGO -->
<br />
<p align="center">
<a href="
</a>
<h3 align="center">PassDetective</h3>
<p align="center">
<br />
<a href=" Post »</strong></a>
<br />
<br />
·
<a href=" Bug</a>
·
<a href=" Feature</a>
</p>
</p>
<!-- TABLE OF CONTENTS -->
<details open="open">
<summary>Table of Contents</summary>
<ol>
<li>
<a href="#getting-started">Getting Started</a>
<ul>
<li><a href="#installation">Installation</a></li>
</ul>
</li>
<li>
<a href="#usage">Usage</a>
<ul>
<li><a href="#extract-shell-history">Analyze ZSH History</a></li>
<li><a href="#extract-secrets">Regex Scan on Shell History</a></li>
</ul>
</li>
<li><a href="#reports">Reports</a></li>
<li><a href="#roadmap">Roadmap</a></li>
<li><a href="#contributing">Contributing</a></li>
<li><a href="#license">License</a></li>
<li><a href="#contact">Contact</a></li>
</ol>
</details>
<!-- GETTING STARTED -->
Getting Started
PassDetective is a command-line tool that scans your shell command history for mistakenly written passwords, API keys, and secrets. It uses regular expressions to identify potential sensiti and helps you avoid accidentally exposing sensitive data in your command history.
Installation
Kali Linux
<img width="1727" alt="image" src="
For Nix or NixOS is pre-packed module
a. The lastest release is usually present in the `unstable channel.
Features
<!-- USAGE EXAMPLES -->
Usage
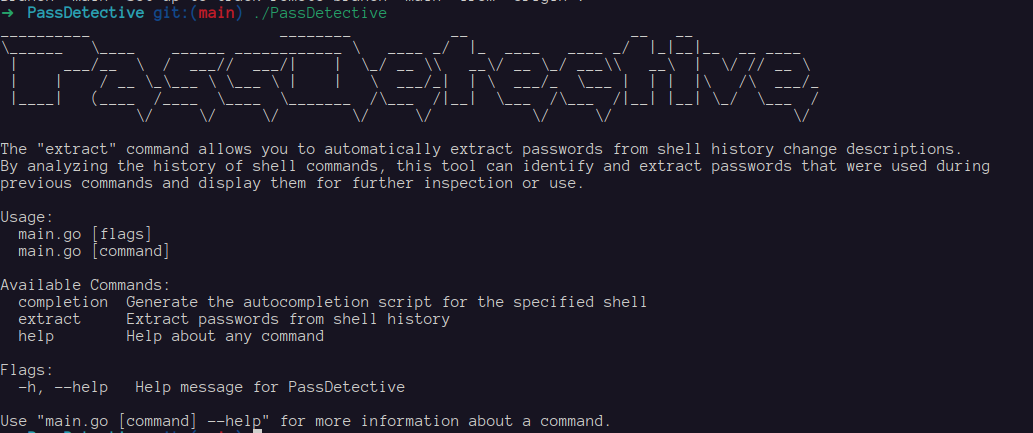
!PassDetective Help
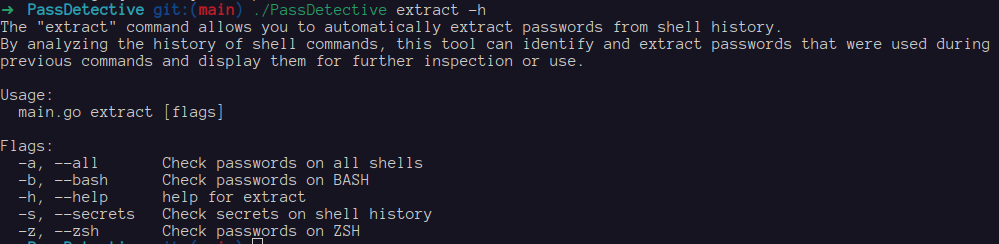
Extract Shell History
!Extract History
After you ha requirements , you can simply analyze the image via:
!Extract All
Extract Secrets
If you want to specify directory use this command:
!Secrets
Regular Expressions
PassDetective uses the following regular expressions to identify potential sensiti:
Source :
Roadmap
See the open issues for a list of proposed features (and known issues).
<!-- CONTRIBUTING -->
Contributing
Contributions are what makes the open source community such an amazing place to learn, inspire, and create. Any
contributions you make are greatly appreciated.
1. Fork the Project
2. Create your Feature Branch (git checkout -b feature/AmazingFeature)git commit -m 'Add some AmazingFeature'
3. Commit your Changes ()git push origin feature/AmazingFeature
4. Push to the Branch ()
5. Open a Pull Request
<!-- LICENSE -->
License
Distributed under the Apache License 2.0 License. See LICENSE` for more information.
<!-- CONTACT -->
Contact
<img target="_blank" src=" title="LinkedIn"> <img target="_blank" src=" title="Github"> <img target="_blank" src=" title="Instagram"> <img target="_blank" src=" title="LinkedIn">
<!-- MARKDOWN LINKS & IMAGES -->
<!-- -->
[contributors-shield]:
[contributors-url]:
[forks-shield]:
[forks-url]:
[stars-shield]:
[stars-url]:
[issues-shield]:
[issues-url]:
[license-shield]:
[license-url]:
[linkedin-shield]:
[linkedin-url]:
[product-screenshot]: data/images/base_command.png
[latest-release]:
项目信息
开发语言:Go
Star 数:149
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕PassDetective is a command-line tool that scans shell command history to detect mistakenly written passwords, API keys, and secrets. Using regular expressions, it helps prevent accidental exposure of sensitive information in your command history. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | PassDetective - PassDetective is a command-line tool that scans sh |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:49:18 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 400 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |