 红蓝攻防
点击放大
noWatch - Implant drop-in for EDR testing
项目说明
noWatch
---
noWatch is an interacti application that allows tampering with EDR userland hooks and testing EDR detection capabilities. It is meant to be used as a standalone binary or con with
donut and remotely injected. In general, it is designed as a drop-in replacement for testing what C2 framework features can get detected without deploying C2 in an Internet-isolated detection lab.> update: integrated SW2 and SW2 with trampolines to test RX allocations (credits )
> update: integrated rad9800's DLL load proxying
> update: added a createthread command for CreateThread and directthread/indirectthread for thread creation with syscalls
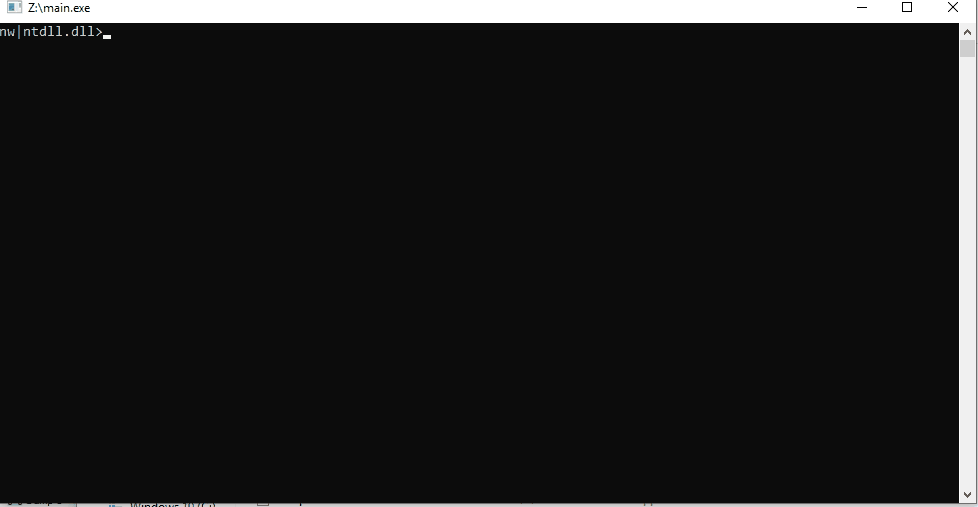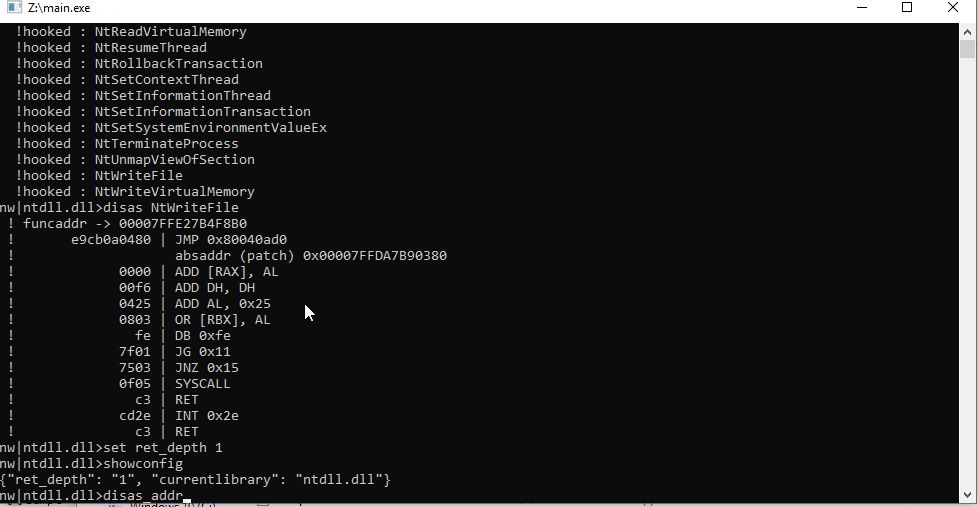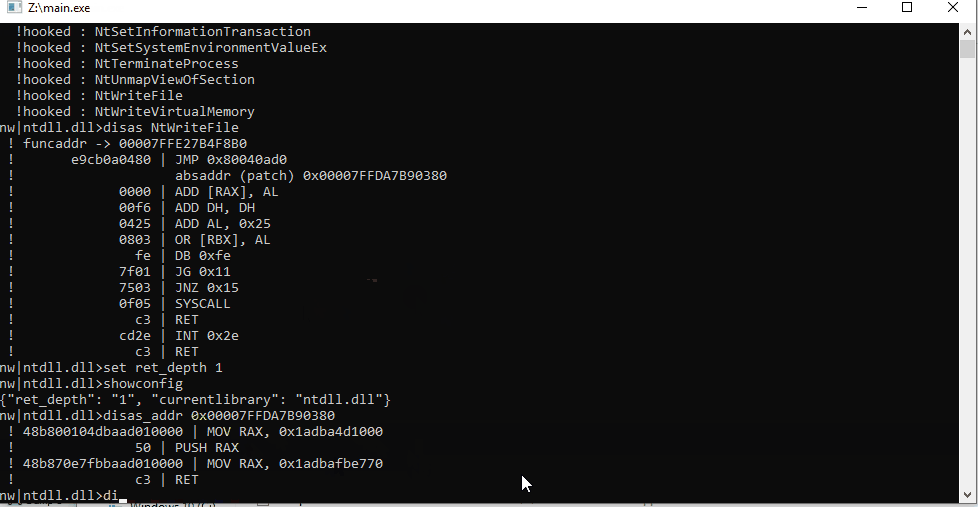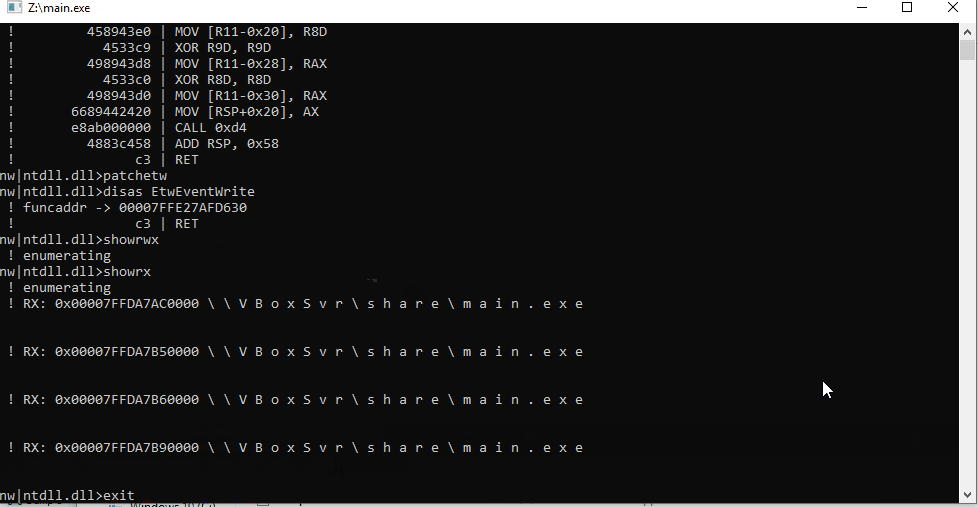
Usage demo:
---
!nowatch_0 0 1
noWatch capabilities are divided into discovery commands and attacks. Discovery commands are simple and few:
Attacks are pretty simple, as they are meant to test malicious activity primitives:
dependencies&building
$ nimble install winim ptr_math memlibFor injection, you'll need to compile the executable with a relocation table with --passL:-Wl,--dynamicbase.
credits and offensive Nim resources
sli, trustedsec and rsmudge for the bofs项目信息
开发语言:C
Star 数:144
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Implant drop-in for EDR testing展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | noWatch - Implant drop-in for EDR testing |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:49:44 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 527 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |