 红蓝攻防
点击放大
kali-pentest - Kali Linux penetration testing skill for AI agents
项目说明
English | 简体中文
kali-pentest
A penetration testing skill built on Kali Linux for AI agents such as Claude Code, OpenClaw, and Hermes Agent. Currently includes 269 CLI tools across 14 categories. Built-in co matrices, zero-findings fallbacks, and objecti conditions for each scenario ensure testing depth.
Unlike traditional automated penetration testing tools, the AI agent connects to a Kali en via SSH or Docker, then autonomously plans the attack path based on the target, selects tools, integrates and analyzes results across phases to adapt the penetration strategy, and produces a structured report — with mandatory authorization checks and human appro for high-risk actions.
> [!WARNING]
> Authorized Use Only — This project is intended solely for authorized penetration testing, security research, and educational purposes. Always obtain explicit written permission before testing any target. Unauthorized access to computer systems is illegal.
---
Demo
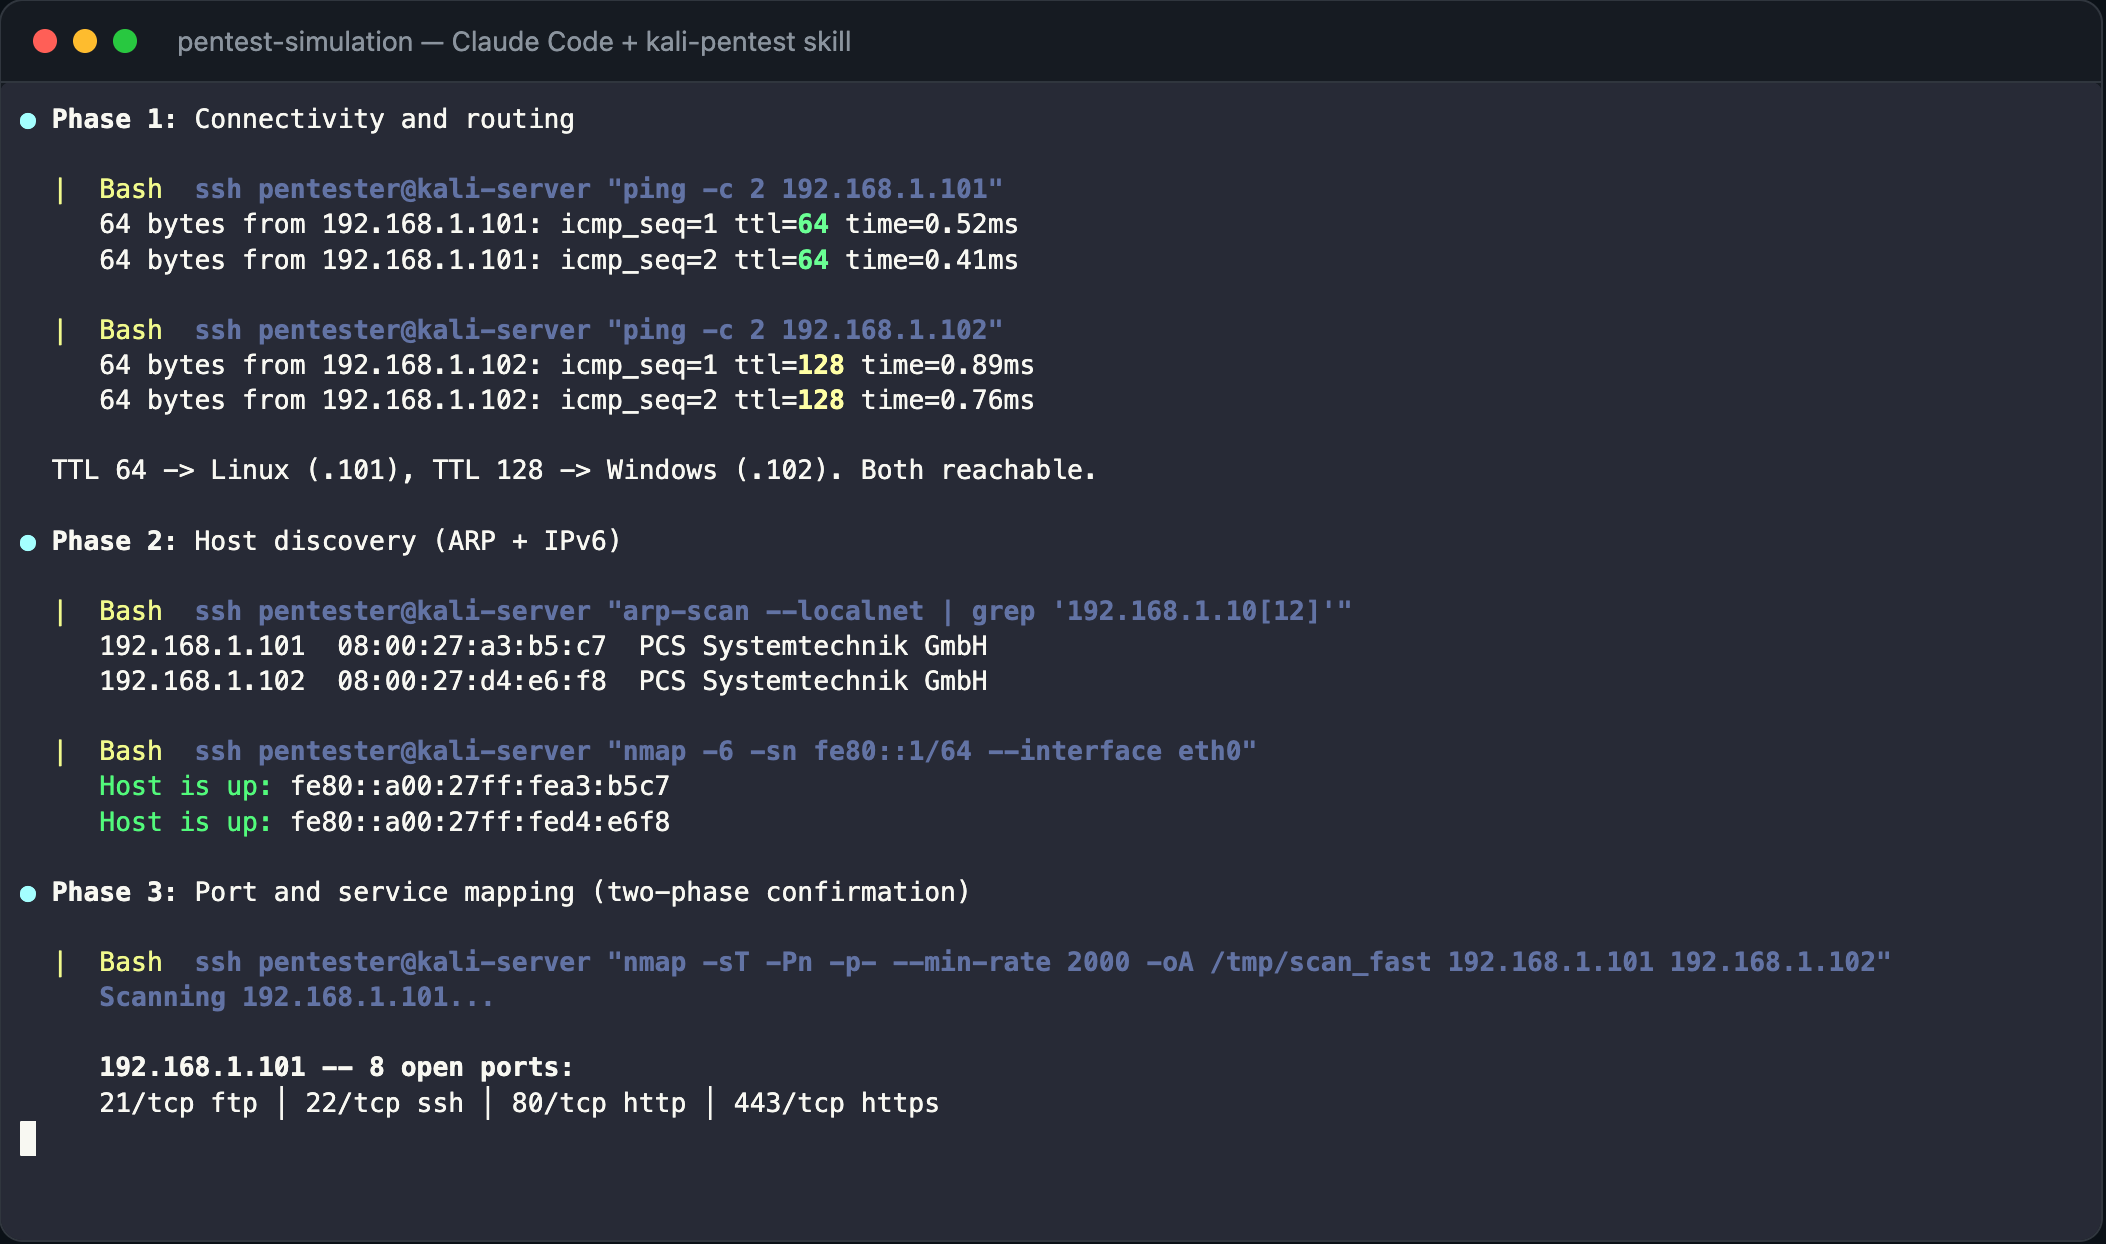
A simulated end-to-end penetration test with mock data.
Targets: 192.168.1.101 (Ubuntu 24 — 8 services) + 192.168.1.102 (Windows Server 2022 — 8 services).
Initial phases — connectivity , host discovery, and port scanning:
!screenshot-1
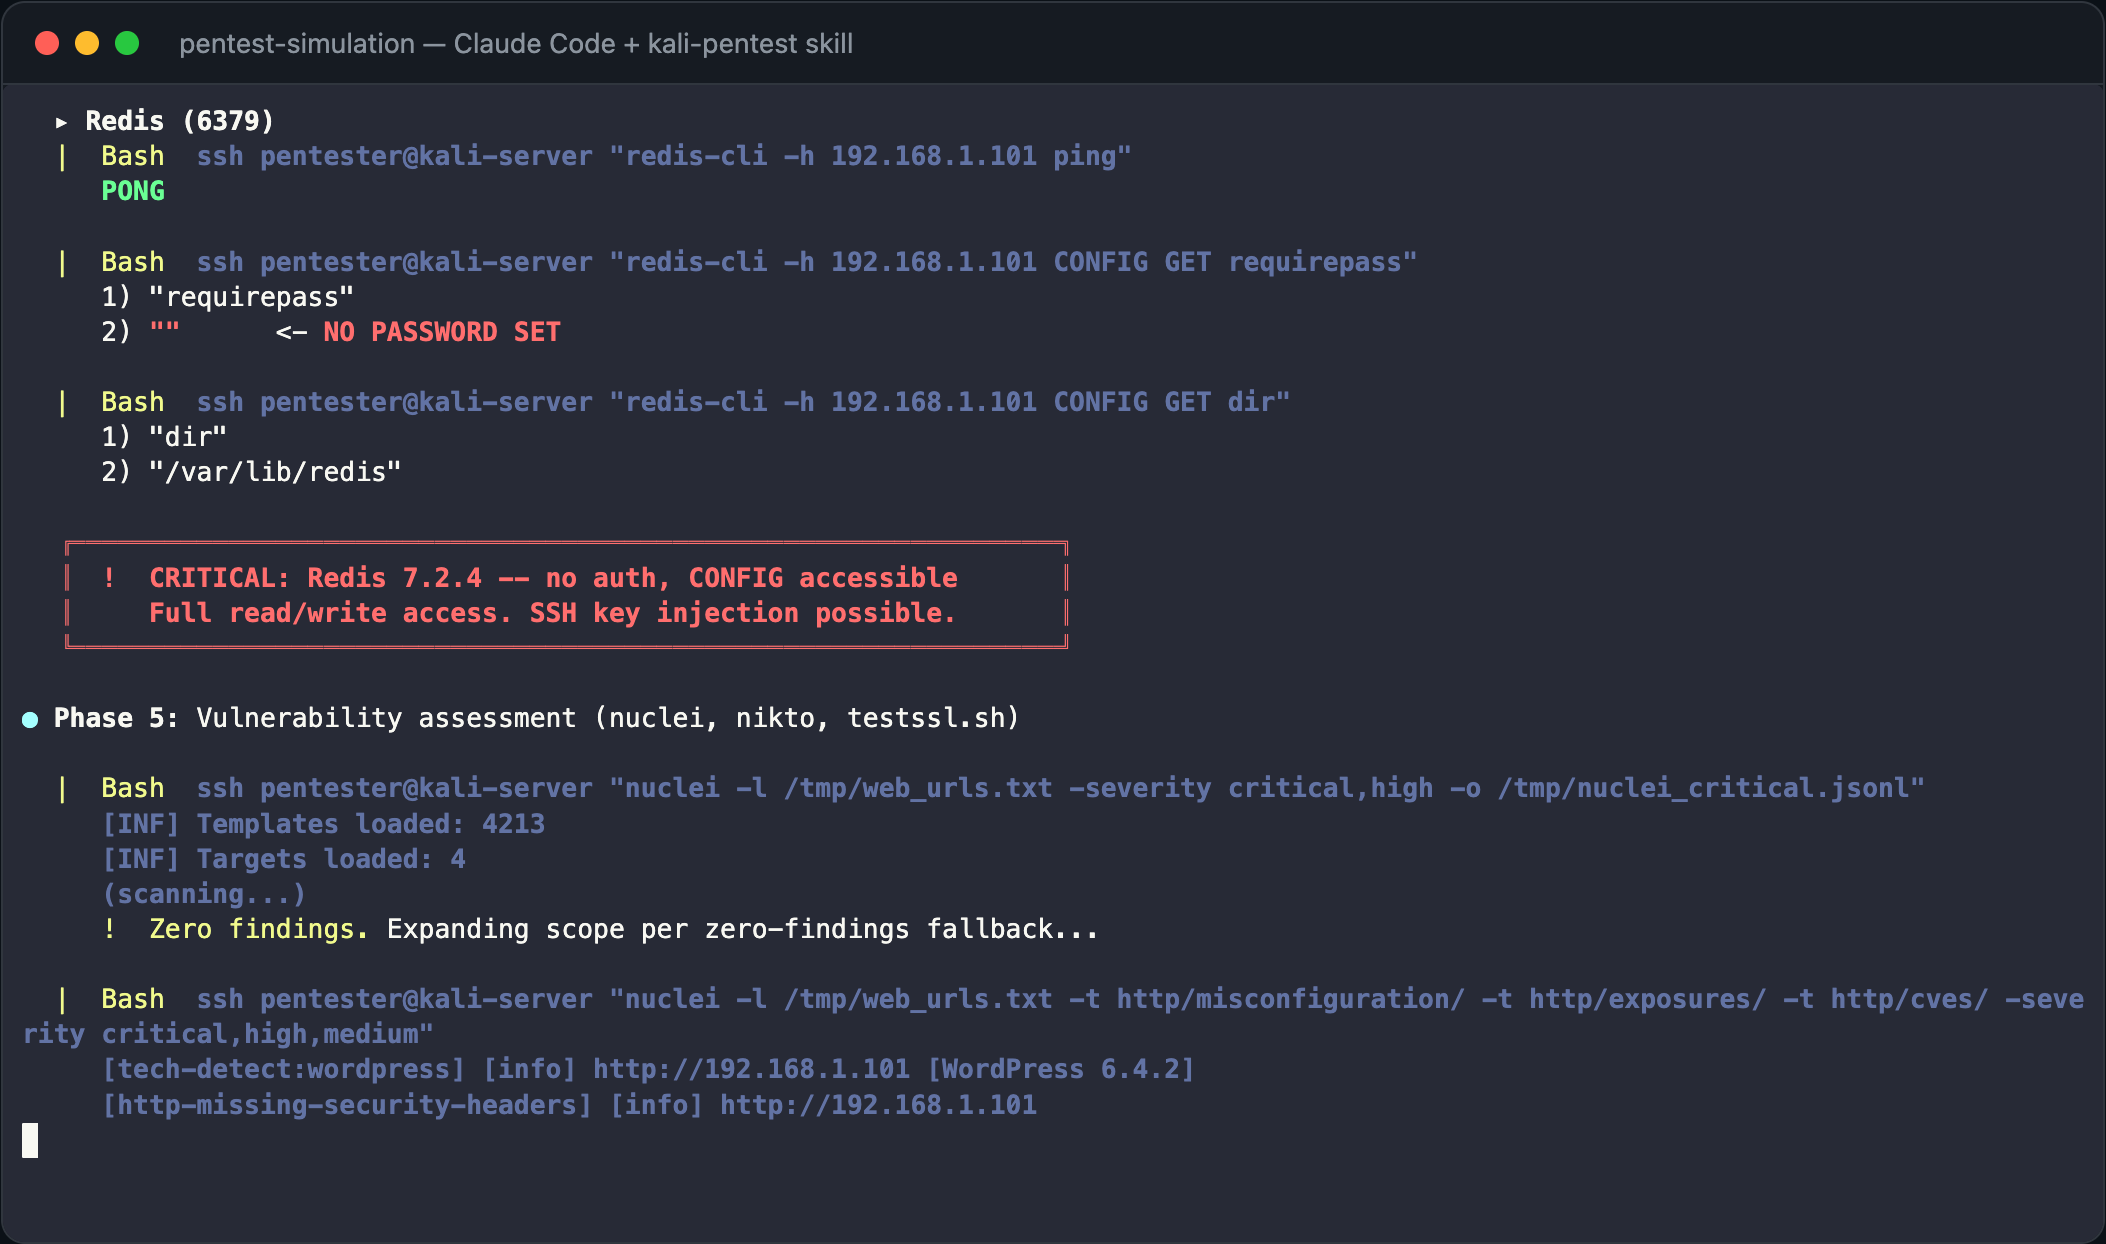
Deep testing phase — detection and zero-findings fallback:
!screenshot-2
Attack chain discovered: Redis no-auth → SSH shell → SUID privesc → root → path tra reads MSSQL creds → xp_cmdshell → credential reuse → domain admin → secretsdump
<a href="
<picture>
<img src=" alt="Play simulation">
</picture>
</a>
Open demo/player.html in a browser to watch the recording with the asciinema player. Or play from the command line:
Report attachments:
demo/simulation-report.md — Full Markdown report with e, reproduction steps, and remediationdemo/simulation-report.html — Beautified HTML report (dark theme, attack chain diagram, se badges)---
Workflow
O Workflow
Execution Detail (Step 3)
---
Getting Started
1. Install the skill
Copy the skill directory into your AI agent's skills folder:
| Agent | Skills path |
|---|---|
| Claude Code | ~/.claude/skills/ (personal) or .claude/skills/ (project) |
| OpenClaw | ~/.openclaw/skills/ |
| Hermes Agent | ~/.hermes/skills/ |
2. Provide Kali access
The agent needs a Kali Linux en. Three options:
Documentation: Kali installation guide, Local mode guide.
Documentation: Kali installation guide, Server mode guide.
Documentation: Kali Docker guide, Docker mode guide.
Tell the agent how to connect:
Or use a remote Kali server (SSH key recommended):
Or use Docker locally:
*For OpenClaw and similar AI assistants, you can also configure Kali connection details in TOOLS.md so the agent reads them automatically without asking each time.*
3. Invoke
Use natural language to assign a penetration testing task. The agent confirms scope and proceeds autonomously.
Slash command:
For Claude Code and compatible agents.
Con:
For OpenClaw, Hermes Agent, and other AI assistants.
Tested Models
The skill workflow has been optimized and tested with:
claude-opus-4.6claude-sonnet-4.6deepseek-qwen3.6:27b — local fallback for air-gapped en (requires context length ≥ 128K)---
Usage Examples
The agent supports three testing depths — Quick (fast check), Standard (default), and Deep (maximum co). Control it with natural language in your task description:
| Phrase in your prompt | Depth |
|---|---|
| "quick scan", "fast check" | Quick |
| *(no qualifier)* | Standard |
| "full assessment", "comprehensive", "deep" | Deep |
Example 1 (Quick) — "quickly scan":
Example 2 (Standard) — no depth qualifier:
Example 3 (Deep) — "in-depth":
> [!TIP]
> A thorough, deep penetration test may require multiple con turns to complete. If the agent finishes too early or co is insufficient, you can point out the issue directly, or follow up with:
> - "Did you fully utilize Kali Linux tools during the penetration test?"
> - "Are the current pentest results comprehensive and deep enough?"
> - "Check the playbook's Stop When conditions — have all checklist items been satisfied?"
<details>
<summary>More examples (API, cloud, mobile, wireless, source code, VoIP/ICS)</summary>
</details>
---
Architecture
Directory Structure
The kali-pentest-zh/ directory is the Chinese mirror and stays structurally synchronized with kali-pentest/.
Document Layering
The skill uses a four-layer document hierarchy. Each layer has a distinct responsibility, and the agent reads top-down:
| Layer | Files | Responsibility |
|-------|-------|----------------|
| Entry point | SKILL.md | Global workflow (Steps 1–5), execution standards, general testing principles |
| Scenario workflows | playbooks/*.md | Phase-by-phase procedures, decision trees, concrete command pipelines, depth-enforcement directives, stopping conditions |
| Tool selection | <category>/README.md | Category o, tool comparison, selection guidance |
| Tool reference | <category>/tools/<name>.md | Parameters, command examples, installation, notes, official links |
General principles live in SKILL.md (brief, no code blocks). Scenario-specific implementations live in playbooks (concrete commands, test matrices, co requirements). The layered structure prevents duplication while ensuring both global co and per-scenario depth.
Depth Enforcement
Each playbook includes bold-labeled directives at key workflow decision points to prevent the agent from doing shallow, surface-level work:
Every playbook has objecti stopping conditions — not "testing is complete" but specific artifacts, matrices, and checklists that must be filled. Every confirmed finding must include the complete reproducible command and its actual output as e.
Cross-Reference Logic
Playbooks form a connected graph. When a workflow phase discovers targets that belong to a different scenario (e.g., AD signals during internal network scanning, API endpoints during web testing), the playbook directs the agent to switch. All such handoffs are listed in each playbook's Cross-References section.
Reusable methodology (e.g., the scanning procedures in internal-network.md and protocol enumeration in internal-network-protocols.md) can be referenced from other playbooks.
Playbooks
16 scenario workflows with phases, decision trees, risk gates, and stopping conditions:
| Playbook | Scenario |
|---|---|
| internal-network.md | Host discovery, port scanning, service enumeration, pi |
| internal-network-protocols.md | SMB, MSRPC, SNMP, SMTP, DNS, database, RDP protocol-specific enumeration |
| external-attack-surface.md | OSINT, subdomain enumeration, exposed service scanning |
| web-application.md | OWASP Top 10, CMS, injection, auth, business logic |
| api-security.md | REST, GraphQL, gRPC, WebSocket, JWT, BOLA/IDOR |
| acti.md | Kerberoasting, ADCS, relay, ACL abuse, DCSync |
| password-audit.md | Hash cracking, spraying, credential reuse, capture |
| wireless-assessment.md | WPA/WPA3, WPS, evil twin, Bluetooth/BLE |
| cloud-nati.md | AWS/Azure/GCP IAM, Kubernetes, containers, ser |
| mobile-application.md | Android/iOS static + dynamic analysis, SSL pinning bypass |
| post-exploitation.md | Pri escalation, lateral mo, persistence, C2 |
| forensics-triage.md | Disk imaging, memory forensics, log analysis, steganography |
| rfid-nfc.md | NFC/RFID cloning, smart cards, firmware extraction |
| .md | VoIP/SIP, ICS/OT/Modbus, IPMI/BMC (safety-first) |
| source-code-audit.md | Secret scanning, SAST, dependency audit, CI/CD checks |
| reporting-workflow.md | E packaging, C, report generation |
Tool Selection Criteria
All tools are selected for autonomous agent operation:
strings, checksec, radare2 one-shot, Ghidra Headlesstshark instead of Wireshark---
Disclaimer
This project is provided as-is for educational purposes and authorized security testing. Users are solely responsible for obtaining written authorization and complying with applicable laws and regulations. The authors assume no liability for damage caused by this project.
Disclosure
Security discovered during authorized testing must be reported pri to the asset owner through agreed-upon channels. Do not publicly disclose details before the owner has had reasonable time to remediate. Follow responsible disclosure practices and any coordinated disclosure agreements in your engagement scope.
Contributing
Issues and pull requests are welcome.
项目信息
开发语言:未知
Star 数:134
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Kali Linux penetration testing skill for AI agents (Claude Code, OpenClaw, Hermes Agent). 200+ CLI tools, 15 scenario playbooks. Autonomously plans attack paths, selects tools, and integrates results across phases to adapt the penetration strategy — with human approval gates for high-risk actions.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | kali-pentest - Kali Linux penetration testing skill for AI agents |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:50:42 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 234 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |