 红蓝攻防
点击放大
codasm - Payload encoding utility to effectively lower payl
项目说明
<di="center">
<img width="175px" src="rsrc/codasm.png" />
<h1>CODASM</h1>
<br/>
<p><i>CODASM allows you to encode arbitrary data into pseudo ASM instructions and compile them into the .text section of binaries.<br />Comes with 80-120% o (e.g. 380KB CS shellcode => 870KB CODASM payload).</i></p>
<p><i>Written by <a href=" Thomas</a> from the <a href=" team at <a href="
<br/>
</div>
> [!WARNING]
> Disclaimer: This repository, including all code, scripts, and documentation contained herein, is provided by NVISO exclusively for educational and informational purposes. The contents of this repository are intended to be used solely as a learning resource. The authors of this repository expressly disclaim any responsibility for any misuse or unintended application of the tools, code, or information provided within this repository.
> Users are solely responsible for ensuring that their use of the repository complies with applicable laws and regulations. The authors of this repository do not provide any warranties or guarantees regarding the accuracy, completeness, or suitability of the contents for any particular purpose.
> If you do not agree with these terms, you are advised not to use or access this repository.
Table of Contents
- Shellcode
- 1. IsPE
- 2. ExampleUsage
- 3. Decode
- 4. PEAnalysis
- 5. Shellcode
- 6. CODASMed
- Summary
Installation
Simply clone the repo locally: git clone
* CODASM source code generator:
* Python3
* CODASM shellcode wrapper:
* Python3
* nasm
* mingw-w64
* sed
* grep
* awk
* dd
Usage: Source code generator
Example:
1. Prepare shellcode (e.g. CS/BR shellcode) and save as shellcode.bin
2. Encode shellcode using CODASM: ./codasm.py --i shellcode.bin -oc codasmloader.h
3. Copy codasmloader.h into your fa loader or into a standalone minimal loader (e.g. /demo/codasm.c)
4. Ensure to call CODASM's decode before calling the shellcode:
5. Compile your loader
6. Ensure to strip the resulting binary to remove any debugging information!
Usage: Shellcode wrapper
Example:
1. Prepare shellcode (e.g. CS/BR shellcode) and save as shellcode.bin
2. Generate shellcode wrapper that uses CODASM to encode it: ./codasm_shellcode.sh shellcode.bin shellcode_codasm.bin
3. shellcode_codasm.bin now holds your CODASM'ed shellcode and can be executed.
Concept
Payloads (esp. shellcode) come with pretty high entropy and look out of place in most places in a compiled binary. CODASM aims to hide payloads in a place that comes with a high entropy already: the .text section that contains your binary's compiled code. To do so, CODASM generates legit looking shellcode that can embed any arbitrary payloads.
CODASM is a Python script that generates
1. legit looking shellcode for arbitrary payloads
2. a C header file you can use in your program to embed the shellcode into a binary and retrieve it at run-time
For encoding payloads, CODASM does the following:
- Embed payload bytes into instruction operands (e.g.
mov eax, <4 bytes of payload>)- XOR encrypt the embedded payload bytes
For decoding payloads, the generated C header file does the following:
- Detect indi instructions, determine whether they contain payload bytes
- If an instruction contains payload bytes, extract and decrypt them
Shellcode
The shellcode wrapper simply holds the CODASM encoded payload, the abo decoder and a brief ASM stub that calls the decoder.
Example
> Note that the compiled binary wasn't stripped, hence there's identifiers like payload showing up.
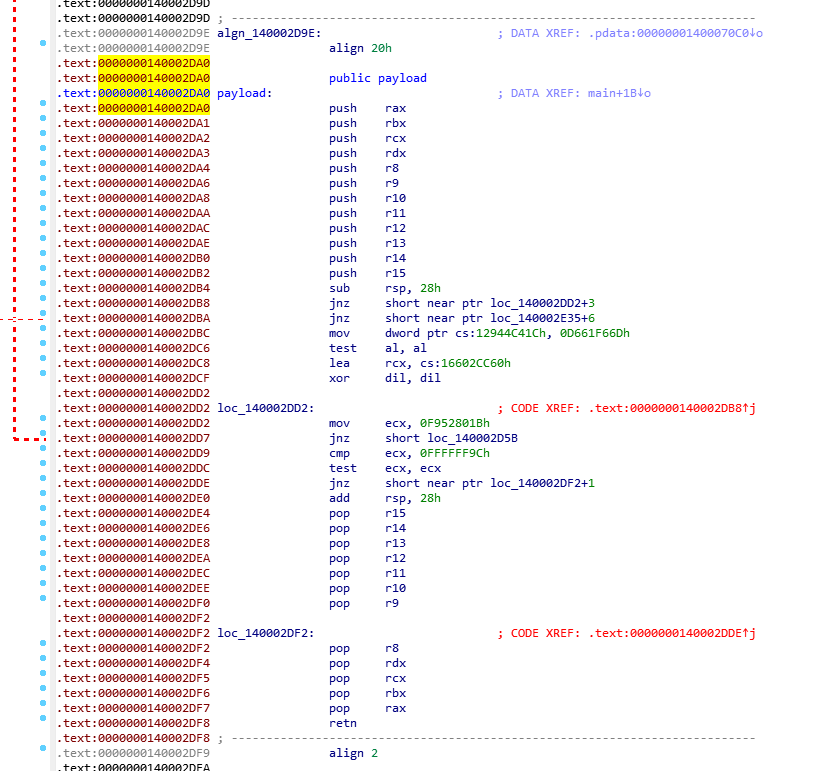
The embedded payload looks like this in IDA:

Detection
You can use the following YARA rules to potentially detect a PECOFF file that embeds output generated by CODASM. You can find a brief description of the rules below the code block.
#### 1. IsPE
0x5A4D, which corresponds to the "MZ" header used in PE (Portable Executable) files.#### 2. ExampleUsage
- $AllocDecode: This string pattern matches a sequence of instructions that include loading from memory, performing a malloc call, and subsequent operations in the
.data section.- $PseudoCall: This string pattern detects a pseudo-class which is ne.
- Condition: This rule is triggered if both the
$AllocDecode and $PseudoCall patterns are found in a file that is identified as a PE file by the IsPE rule.#### 3. Decode
- $NullTest: Matches a sequence of instructions that perform null-checks on parameters.
- $ReturnMinusTwo: Matches an instruction that sets the return value to -2.
- $PseudoCall: Matches a sequence of instructions that perform a pseudo call to the RBX register with a specific value.
- Condition: This rule is triggered if all three patterns (
$NullTest, $ReturnMinusTwo, and $PseudoCall) are found in a file that is identified as a PE file by the IsPE rule.#### 4. PEAnalysis
- Condition: This rule checks if the
.text section of a PE file is larger than or equal to 90% of the total file size and has an entropy value between 5.0 and 7.0. The rule iterates over all sections in the PE file and applies the condition to the .text section.#### 5. Shellcode
- Condition: This rule checks whether the bytes making up the ASM stub and the in of the shellcode and
return 0x420 are present in the file.#### 6. CODASMed
ExampleUsage, Decode, and PEAnalysis.- Condition: This rule is triggered if either the
ExampleUsage rule, both the Decode and PEAnalysis rules or the Shellcode rule are satisfied.Summary
.text sections and specific entropy ranges.ExampleUsage, Decode, and PEAnalysis to detect complex patterns in PE files.Contributing
Please feel free to contribute. It's as simple as:
项目信息
开发语言:Python
Star 数:129
技术要点
该项目属于红蓝攻防方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Payload encoding utility to effectively lower payload entropy.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | codasm - Payload encoding utility to effectively lower payl |
| 所属分类 | 红蓝攻防 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:51:16 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 260 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |