 漏洞知识库
点击放大
trivy - Find vulnerabilities, misconfigurations, secrets,
项目说明
<di="center">
<img src="docs/imgs/logo.png" width="200">
[![GitHub Release][release-img]][release]
[![Test][test-img]][test]
[![Go Report Card][go-report-img]][go-report]
[![License: Apache-2.0][license-img]][license]
[![GitHub Downloads][github-downloads-img]][release]
![Docker Pulls][docker-pulls]
[📖 Documentation][docs]
</div>
Trivy ([pronunciation][pronunciation]) is a comprehensive and security scanner.
Trivy has *scanners* that look for security issues, and *targets* where it can find those issues.
Targets (what Trivy can scan):
Scanners (what Trivy can find there):
Tri most popular programming languages, operating systems, and platforms. For a complete list, see the [Scanning Co] page.
To learn more, go to the [Tri][homepage] for feature highlights, or to the [Documentation site][docs] for detailed information.
Quick Start
Get Trivy
Trivy is a in most common distribution channels. The full list of installation options is a in the [Installation] page. Here are a few popular examples:
brew install trivydocker run aquasec/trivyTrivy is integrated with many popular platforms and applications. The complete list of integrations is a in the [Ecosystem] page. Here are a few popular examples:
Canary builds
There are canary builds (Docker Hub, GitHub, ECR images and binaries) generated with every push to the main branch.
Please be aware: canary builds might ha bugs, so they are not recommended for use in production.
General usage
Examples:
<details>
<summary>Result</summary>
</details>
<details>
<summary>Result</summary>
</details>
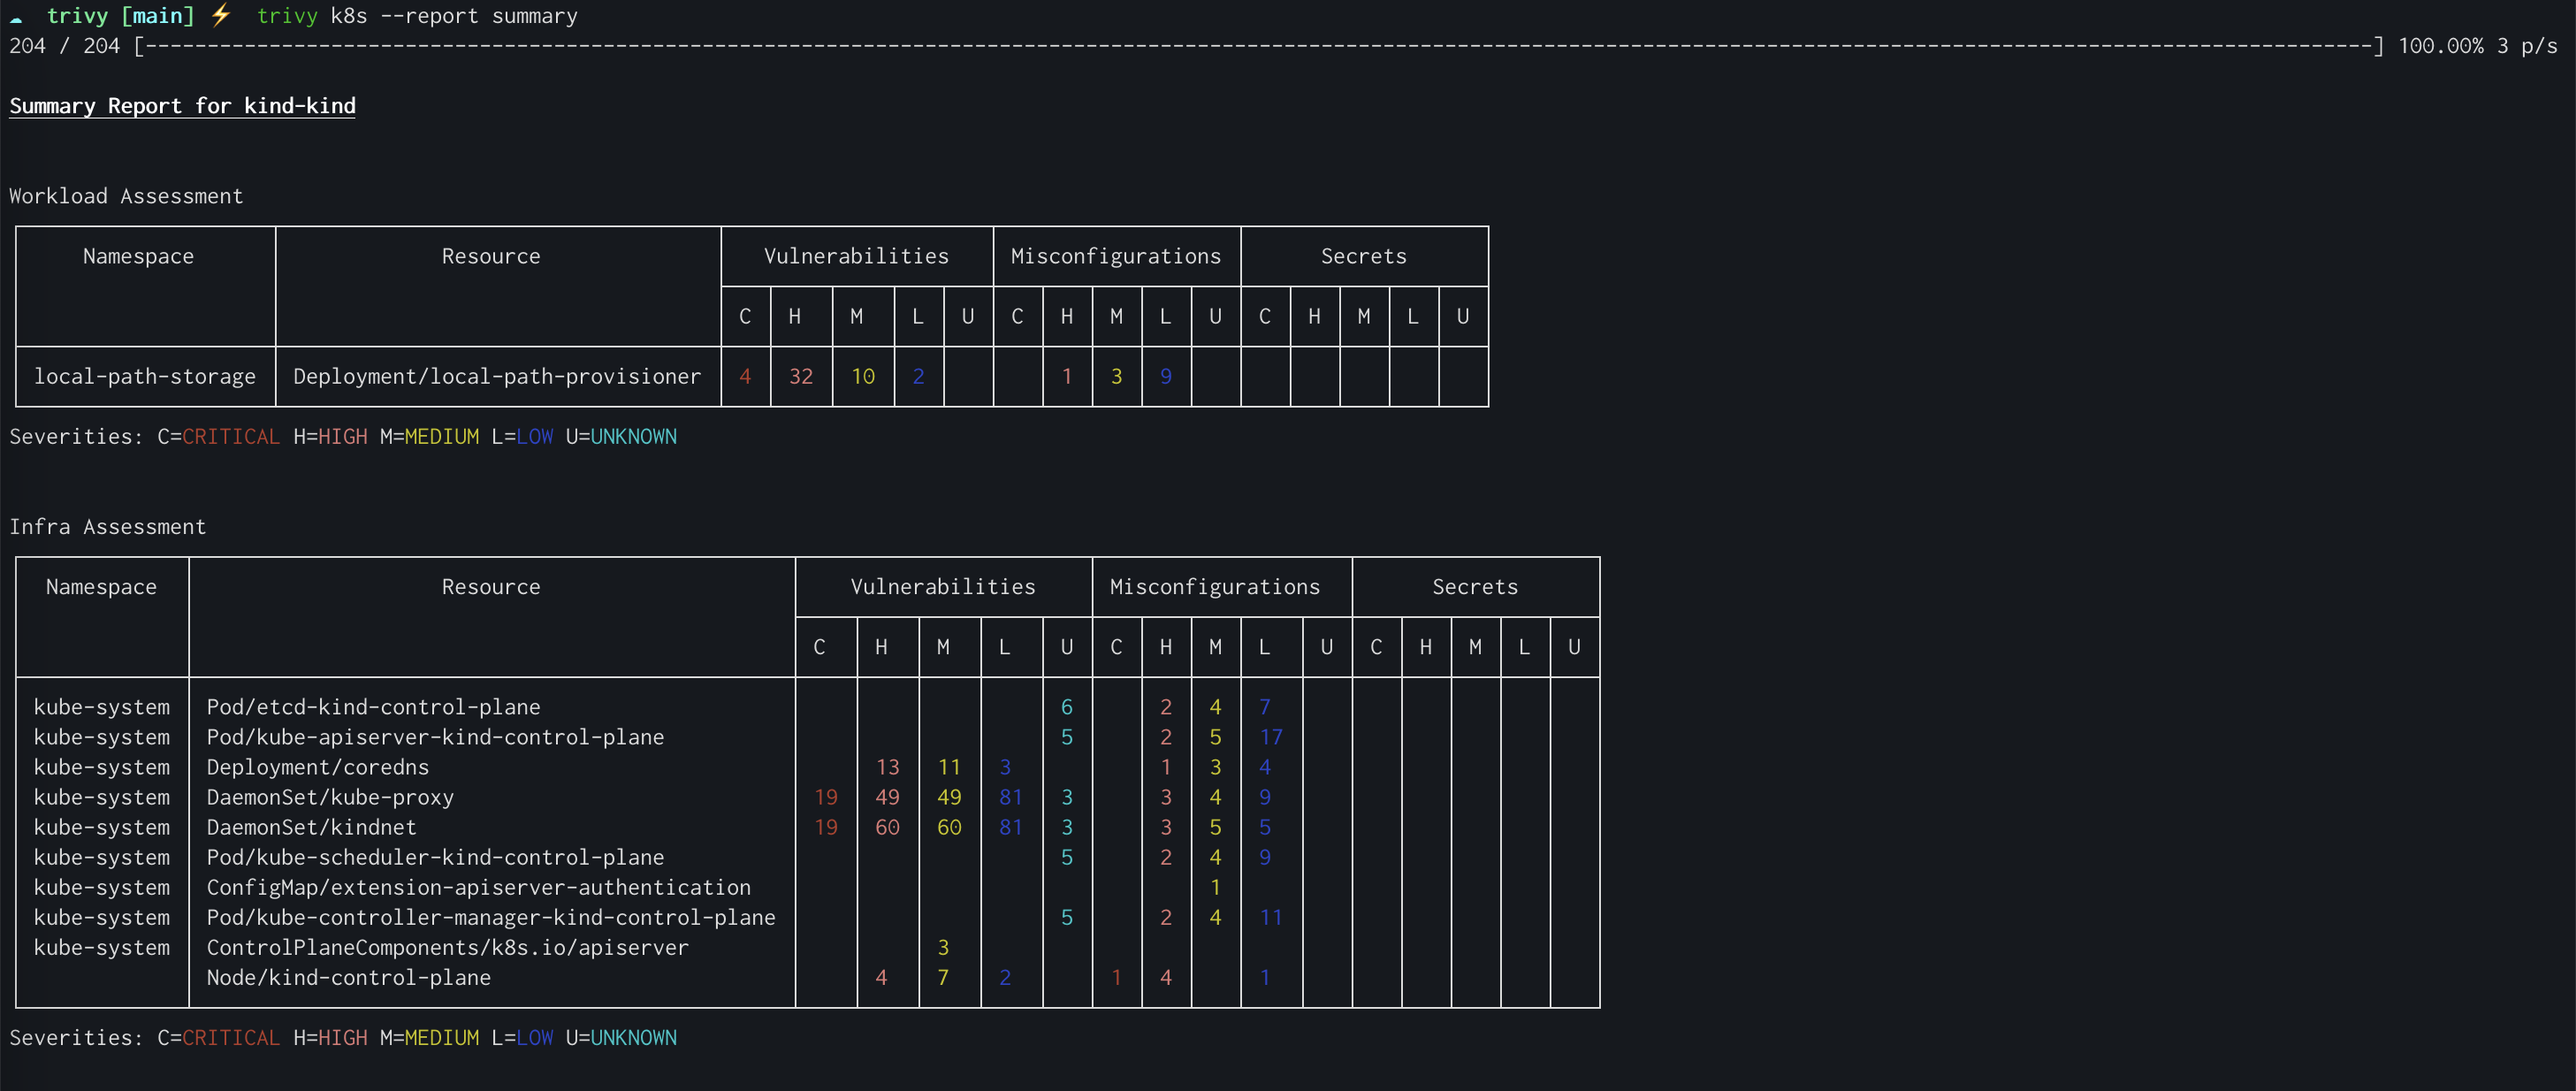
<details>
<summary>Result</summary>
!k8s summary
</details>
FAQ
How to pronounce the name "Trivy"?
tri is pronounced like trigger, vy is pronounced like envy.
Want more? Check out Aqua
If you liked Trivy, you will love Aqua which builds on top of Trivy to provide even more enhanced capabilities for a complete security management offering.
You can find a high le table specific to Tri here.
In addition check out the < website for more information about our products and services.
If you'd like to contact Aqua or request a demo, please use this form: <
Community
Trivy is an [Aqua Security][aquasec] open source project.
Learn about our open source work and portfolio [here][oss].
Contact us about any matter by opening a GitHub Discussion [here][discussions]
Please ensure to abide by our [Code of Conduct][code-of-conduct] during all interactions.
[test]:
[test-img]:
[go-report]:
[go-report-img]:
[release]:
[release-img]:
[github-downloads-img]:
[docker-pulls]:
[license]:
[license-img]:
[homepage]:
[docs]:
[pronunciation]: #how-to-pronounce-the-name-trivy
[code-of-conduct]:
[Installation]:
[Ecosystem]:
[Scanning Co]:
[alpine]:
[rego]:
[sigstore]:
[aquasec]:
[oss]:
[discussions]:
项目信息
开发语言:Go
Star 数:38239
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | trivy - Find vulnerabilities, misconfigurations, secrets, |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:54:44 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 426 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |