 漏洞知识库
点击放大
checkov - Prevent cloud misconfigurations and find vulnerabi
项目说明

![Maintained by Prisma Cloud]()
![build status]()
![security status]()
![code_co]()
![docs]()
![PyPI]()


![Downloads]()
![Docker Pulls]()
![slack-community]()
Checkov is a static code analysis tool for infrastructure as code (IaC) and also a software composition analysis (SCA) tool for images and open source packages.
It scans cloud infrastructure pro using Terraform, Terraform plan, Cloudformation, AWS SAM, Kubernetes, Helm charts, Kustomize, Dockerfile, Ser, Bicep, OpenAPI, ARM Templates, or OpenTofu and detects security and compliance misconfigurations using graph-based scanning.
It performs Software Composition Analysis (SCA) scanning which is a scan of open source packages and images for Common and Exposures (CVEs).
Checkov also powers Prisma Cloud Application Security, the de platform that codifies and streamlines cloud security throughout the de lifecycle. Prisma Cloud identifies, fixes, and prevents misconfigurations in cloud resources and infrastructure-as-code files.
<a href=" title="Try_Prisma_Cloud">
<img src=" align="right" width="120">
</a>
<a href=" title="Docs">
<img src=" align="right" width="120">
</a>
Table of contents
## Features
* Over 1000 built-in policies co and compliance best practices for AWS, Azure and Google Cloud.
* Scans Terraform, Terraform Plan, Terraform JSON, CloudFormation, AWS SAM, Kubernetes, Helm, Kustomize, Dockerfile, Ser framework, Ansible, Bicep, ARM, and OpenTofu template files.
* Scans Argo Workflows, Azure Pipelines, BitBucket Pipelines, Circle CI Pipelines, GitHub Actions and GitLab CI workflow files
* Supports Context-awareness policies based on in-memory graph-based scanning.
* Supports Python format for attribute policies and YAML format for both attribute and composite policies.
* Detects AWS credentials in EC2 Userdata, Lambda en and Terraform pro.
* Identifies secrets using regular expressions, keywords, and entropy based detection.
* E Terraform Provider settings to regulate the creation, management, and updates of IaaS, PaaS or SaaS managed through Terraform.
* Policies support e of to their optional default value.
* Supports in-line suppression of accepted risks or false-positives to reduce recurring scan failures. Also supports global skip from using CLI.
* Output currently a as CLI, CycloneDX, JSON, JUnit XML, CS and github markdown and link to remediation guides.
Screenshots
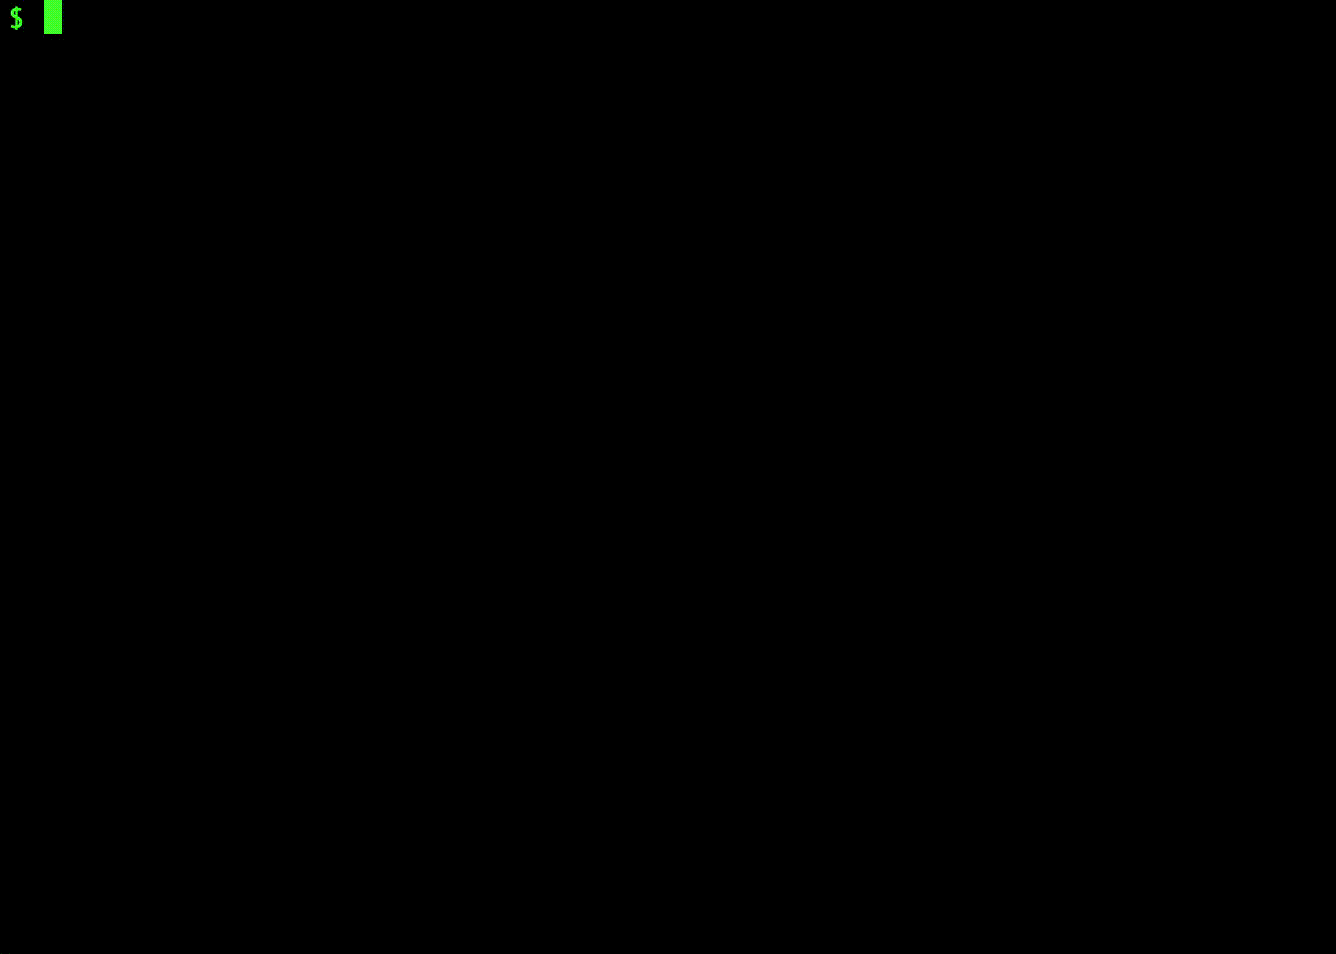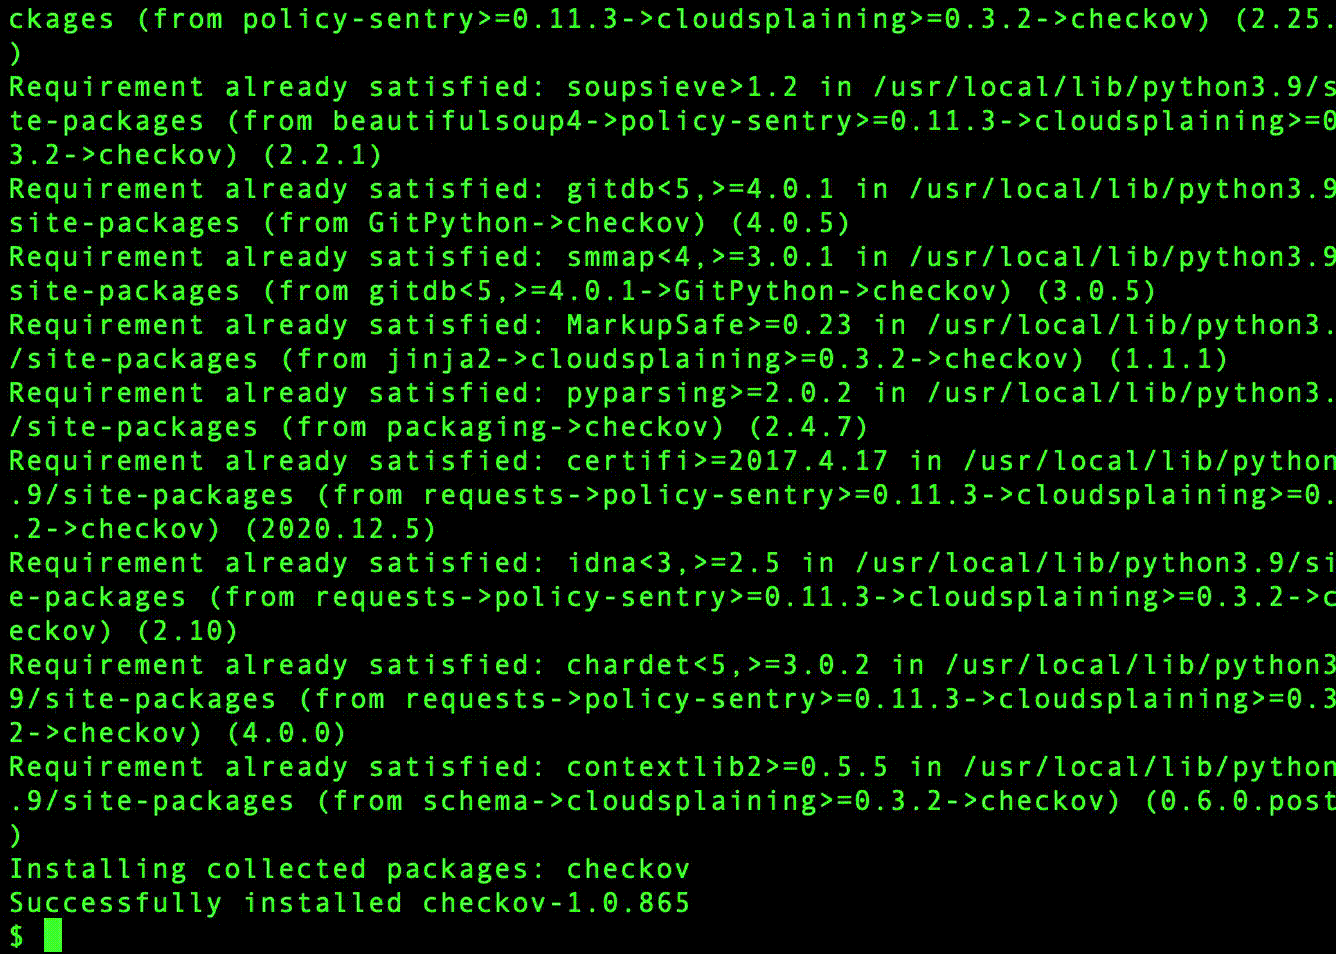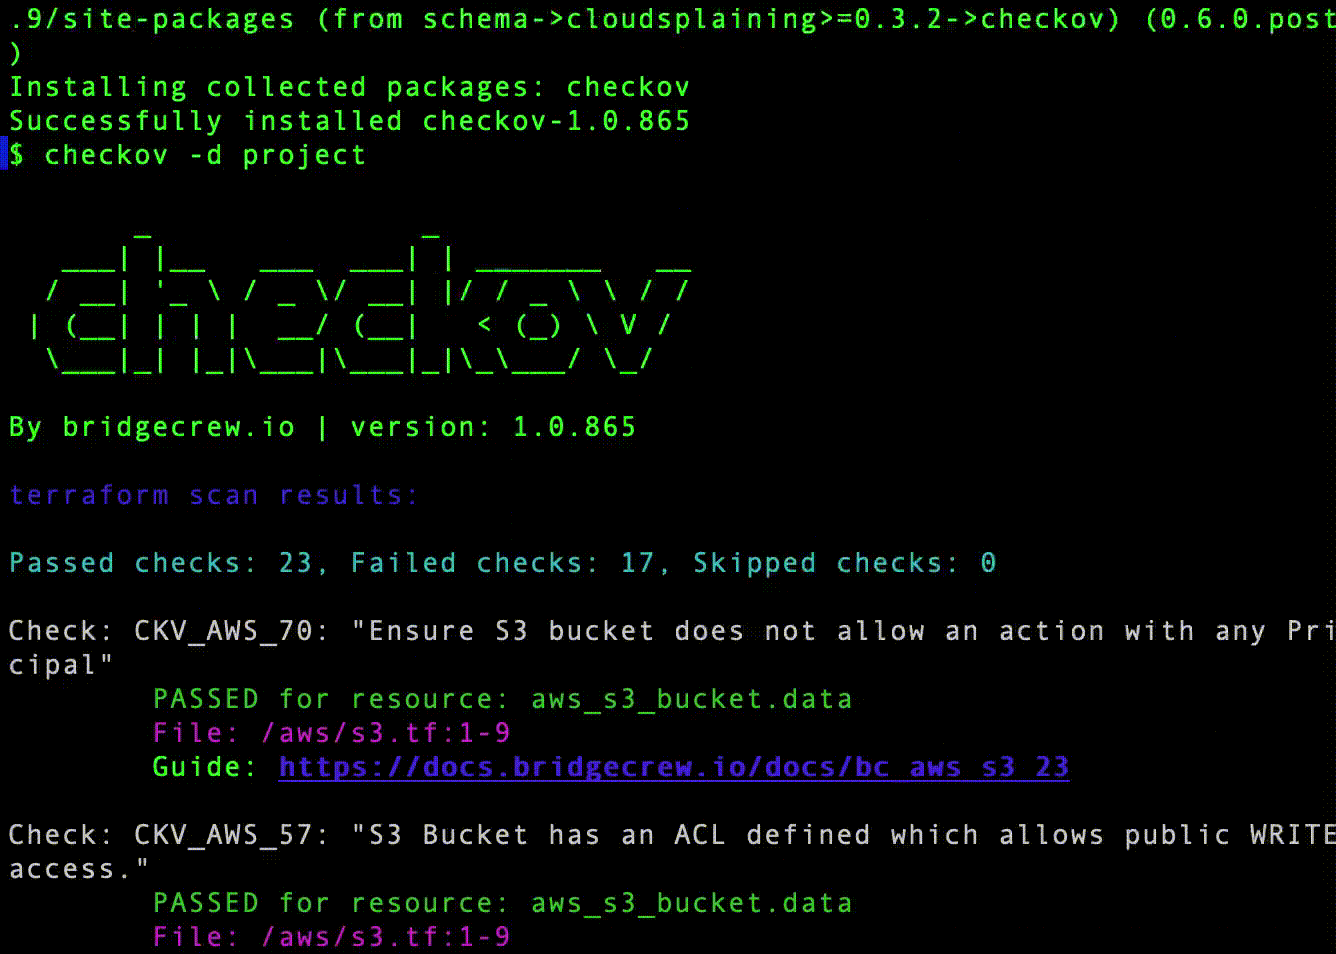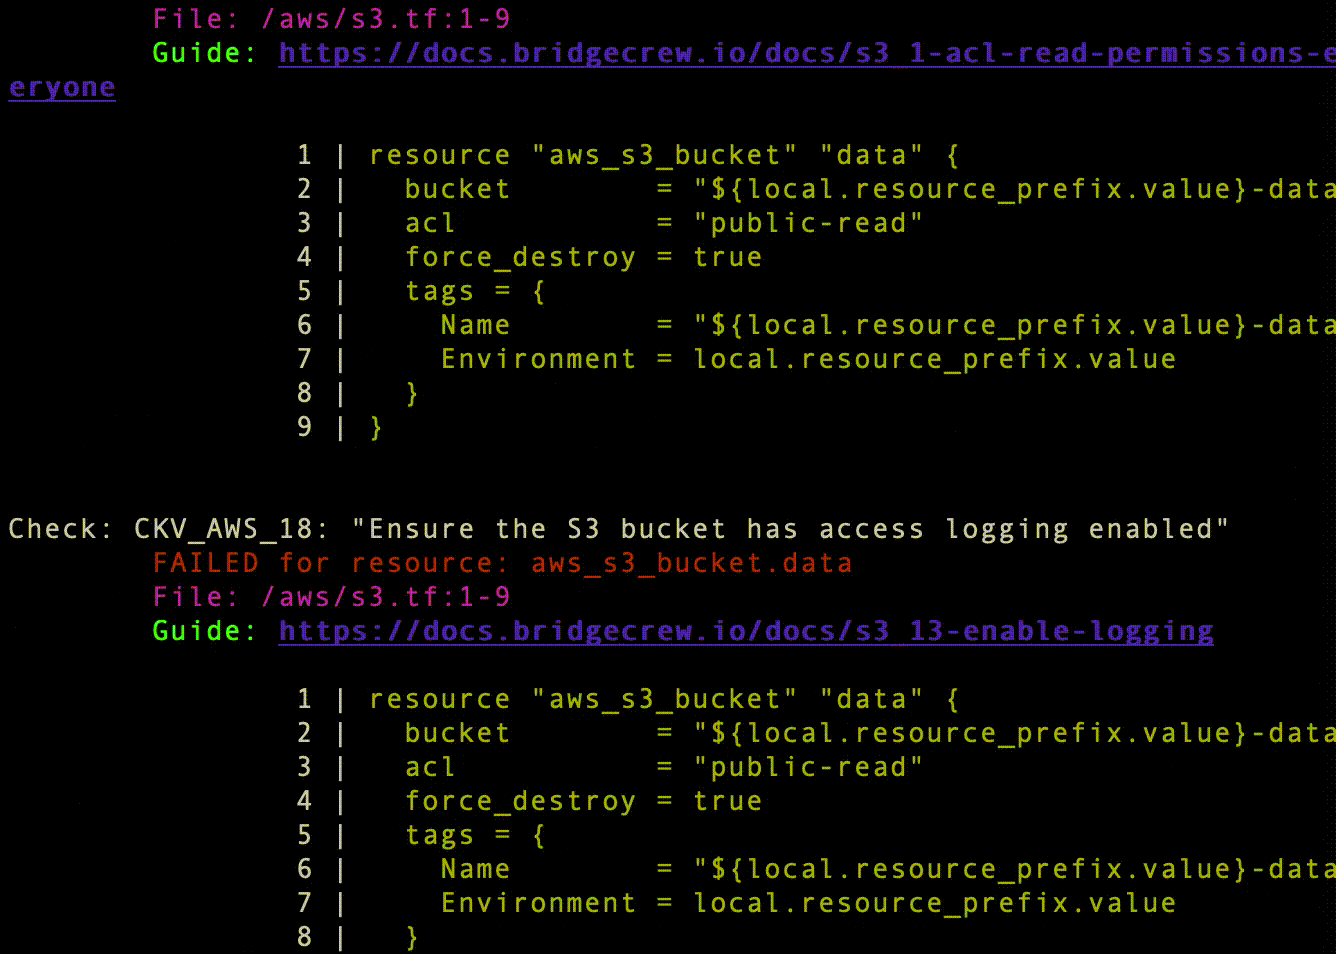
Scan results in CLI
!scan-screenshot
Scheduled scan result in Jenkins
!jenikins-screenshot
Getting started
Requirements
* Python >= 3.9, <=3.12
* Terraform >= 0.12
Installation
To install pip follow the official docs
Certain en (e.g., Debian 12) may require you to install Checkov in a en
or with Homebrew (macOS or Linux)
Enabling bash autocomplete
Upgrade
if you installed checkov with pip3
or with Homebrew
Configure an input folder or file
Or a specific file or files
Or
Or a terraform plan file in json format
Note: terraform show output file tf.json will be a single line.
For that reason all findings will be reported line number 0 by Checkov
If you ha jq you can convert json file into multiple lines with the following command:
Scan result would be much user friendly.
Alternatively, specify the repo root of the hcl files used to generate the plan file, using the --repo-root-for-plan-enrichment flag, to enrich the output with the appropriate file path, line numbers, and codeblock of the resource(s). An added benefit is that check suppressions will be handled accordingly.
Scan result sample (CLI)
Start using Checkov by reading the Getting Started page.
Using Docker
Note: if you are using Python 3.6(Default in Ubuntu 18.04) checkov will not work, and it will fail with ModuleNotFoundError: No module named 'dataclasses' error message. In this case, you can use the docker instead.
Note that there are certain cases where redirecting docker run --tty output to a file - for example, if you want to save the Checko output to a file - will cause extra control characters to be printed. This can break file parsing. If you encounter this, remove the --tty flag.
The --workdir /tf flag is optional to change the working directory to the mounted . If you are using the SARIF output -o sarif this will output the results.sarif file to the mounted (/user/tf in the example above). If you do not include that flag, the working directory will be "/".
Running or skipping checks
By using command line flags, you can specify to run only named checks (allow list) or run all checks except
those listed (deny list). If you are using the platform integration via API key, you can also specify a se threshold to skip and / or include.
Moreover, as json files can't contain comments, one can pass regex pattern to skip json file secret scan.
See the docs for more detailed information about how these flags work together.
Examples
Allow only the two specified checks to run:
Run all checks except the one specified:
Run all checks except checks with specified patterns:
Run all checks that are MEDIUM se or higher (requires API key):
Run all checks that are MEDIUM se or higher, as well as check CKV_123 (assume this is a LOW se check):
Skip all checks that are MEDIUM se or lower:
Skip all checks that are MEDIUM se or lower, as well as check CKV_789 (assume this is a high se check):
Run all checks that are MEDIUM se or higher, but skip check CKV_123 (assume this is a medium or higher se check):
Run check CKV_789, but skip it if it is a medium se (the --check logic is always applied before --skip-check)
For Kubernetes workloads, you can also use allow/deny namespaces. For example, do not report any results for the
kube-system namespace:
Run a scan of a container image. First pull or build the image then refer to it by the hash, ID, or name:tag:
You can use --image flag also to scan container image instead of --docker-image for shortener:
Run an SCA scan of packages in a repo:
Run a scan of a directory with en removing buffering, adding debug level logs:
OR enable the en for multiple runs
Run secrets scanning on all files in MyDirectory. Skip CK check on json files that their suffix is DontScan
Run secrets scanning on all files in MyDirectory. Skip CK check on json files that contains "skip_test" in path
One can mask from scanning results by supplying a configuration file (using --config-file flag) with mask entry.
The masking can apply on resource & value (or multiple , separated with a comma).
Examples:
In the example above, the following will be masked:
Suppressing/Ignoring a check
Like any static-analysis tool it is limited by its analysis scope.
For example, if a resource is managed manually, or using subsequent configuration management tooling,
suppression can be inserted as a simple code annotation.
#### Suppression comment format
To skip a check on a gi definition block or CloudFormation resource, apply the following comment pattern inside it's scope:
checkov:skip=<check_id>:<suppression_comment>
* <check_id> is one of the a check scanners
* <suppression_comment> is an optional suppression reason to be included in the output
#### Example
The following comment skips the CK check on the resource identified by foo-bucket, where the scan checks if an AWS S3 bucket is private.
In the example, the bucket is configured with public read access; Adding the suppress comment would skip the appropriate check instead of the check to fail.
The output would now contain a `SKIPPED check result entry:
To skip multiple checks, add each as a new line.
To suppress checks in Kubernetes manifests, annotations are used with the following format:
checkov.io/skip#: <check_id>=<suppression_comment>
For example:
#### Logging
For detailed logging to stdout set up the en LOG_LEVEL to DEBUG.
Default is LOG_LE.
#### Skipping directories
To skip files or directories, use the argument --skip-path, which can be specified multiple times. This argument accepts regular expressions for paths relative to the current working directory. You can use it to skip entire directories and / or specific files.
By default, all directories named node_modules, .terraform, and .ser will be skipped, in addition to any files or directories beginning with ...
To cancel skipping directories beginning with o CKIES en export CKIES=false
You can o the default set of directories to skip by setting the en CK.CK=mynewdir
Note that if you want to preserve this list and add to it, you must include these . For example, will skip only that directory, but not the others mentioned above. This is legacy functionality; we recommend using the --skip-file flag.
#### Console Output
The console output is in colour by default, to switch to a monochrome output, set the en :
ANSI_COLORS_DISABLED
#### VS Code Extension
If you want to use Checko VS Code, give the Prisma Cloud extension a try.
Configuration using a config file
Checkov can be configured using a YAML configuration file. By default, checko for a .checkov.yaml or .checkov.yml file in the following places in order of precedence:--directory
* Directory against which checkov is run. ()
* Current working directory where checkov is called.
* User's home directory.
Attention: it is a best practice for checko file to be loaded from a trusted source composed by a identity, so that scanned files, check ids and loaded custom checks are as desired.
Users can also pass in the path to a config file via the command line. In this case, the other config files will be ignored. For example:
Users can also create a config file using the --create-config command, which takes the current command line args and writes them out to a given path. For example:
Will create a config.yaml file which looks like this:
Users can also use the --show-config flag to view all the args and settings and where they came from i.e. commandline, config file, en or default. For example:
Will display:
Contributing
Contribution is welcomed!
Start by re the contribution guidelines. After that, take a look at a good first issue.
You can e this with one-click dev in your browser through Gitpod at the following link:
![Open in Gitpod]()
Looking to contribute new checks? Learn how to write a new check (AKA policy) here.
Disclaimer
checkov
 does not sa or share with anyone any identifiable customer information.
No identifiable customer information is used to query Prisma Cloud's publicly accessible guides.
checkov uses Prisma Cloud's API to enrich the results with links to remediation guides.
To skip this API call use the flag --skip-download`.Support
Prisma Cloud builds and maintains Checkov to make policy-as-code simple and accessible.
Start with our Documentation for quick tutorials and examples.
Python Support
We follow the official support cycle of Python, and we use automated tests for supported of Python.
This means we currently support Python 3.9 - 3.13, inclusive.
Note that Python 3.8 reached EOL on October 2024 and Python 3.9 will reach EOL in October 2025.
If you run into any issues with any non-EOL Python , please open an Issue.
项目信息
开发语言:Python
Star 数:9055
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Prevent cloud misconfigurations and find vulnerabilities during build-time in infrastructure as code, container images and open source packages with Checkov by Bridgecrew.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | checkov - Prevent cloud misconfigurations and find vulnerabi |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:55:17 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 481 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |