 漏洞知识库
点击放大
attack_range - A tool that allows you to create vulnerable instru
项目说明
Splunk Attack Range v5
!Attack Range Logo
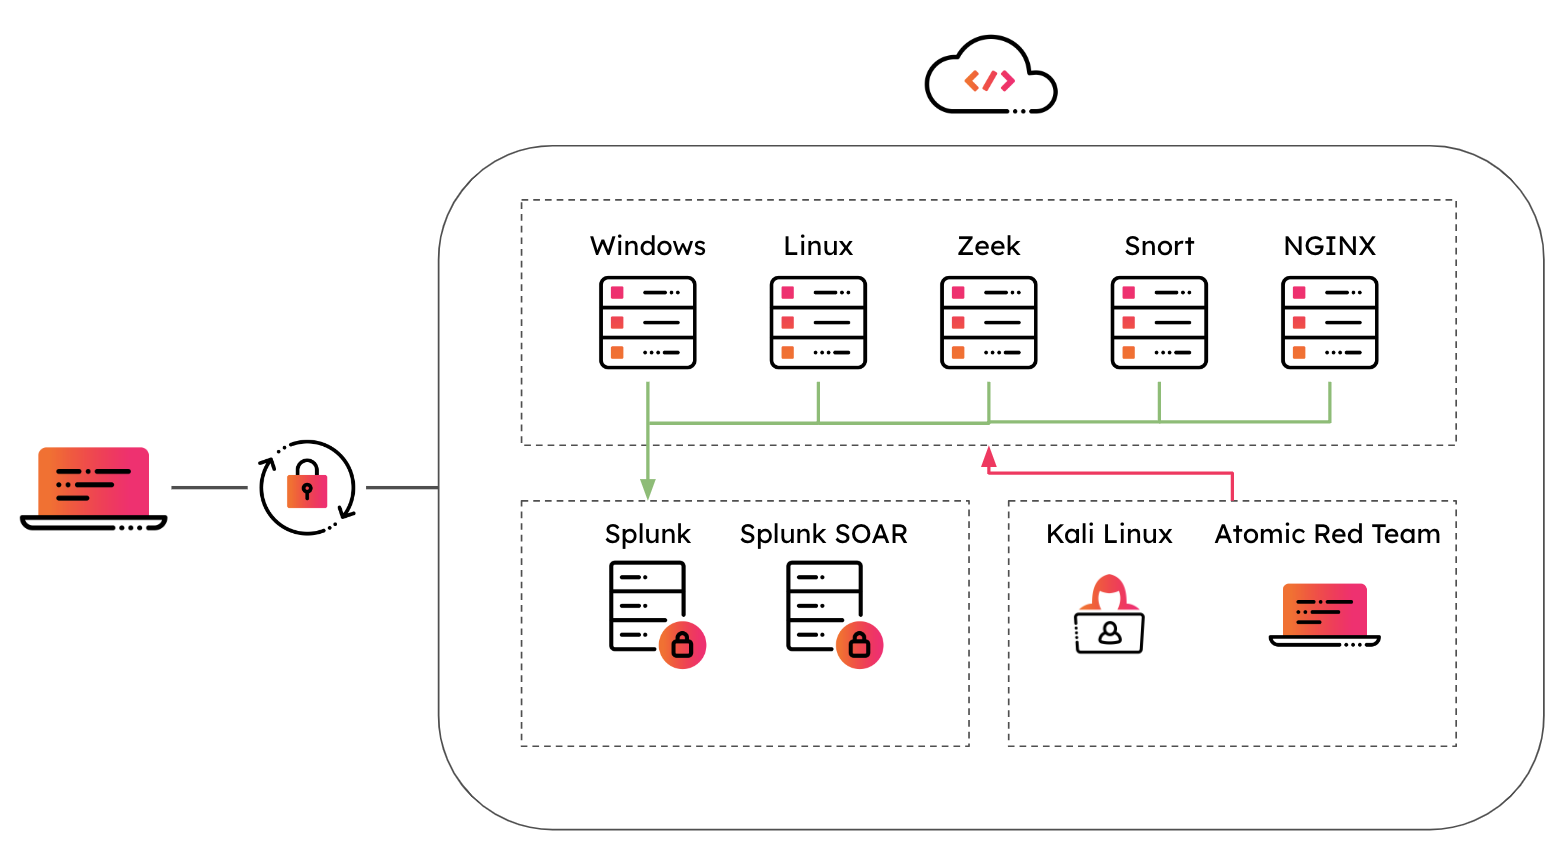
The Splunk Attack Range builds instrumented cloud en (AWS, Azure, GCP), simulates attacks, and forwards data into Splunk for detection de and testing.
!Attack Range Architecture
What it does:
Click the picture to watch the demo 👇
<a href=" target="_blank">
<img src="docs/attack_range_demo.png" alt="Watch the demo" />
</a>
---
Getting started
Preferred: Docker Compose
1. Prerequisites: Docker and Docker Compose. Configure your cloud provider (AWS, Azure, or GCP) and mount credentials as below.
2. Clone and start:
3. Use the app or API:
- Web app: open — build/destroy ranges, view status, run simulations, share access.
- API: — REST API; interactive docs at
4. Build a range (two steps):
- In the app: pick a template (e.g. aws/splunk_minimal_aws) and start the build. When status is *Waiting for VPN*, download the WireGuard config, connect with WireGuard, then continue the build.
- Or via API: POST /attack-range/build with {"template": "aws/splunk_minimal_aws"}, poll GET /attack-range/status/<id>, use the returned WireGuard config, connect, then POST /attack-range/build with {"attack_range_id": "<id>"}.
5. CLI in Docker (optional):
Other actions: destroy, simulate, apply-role, share. See Detailed documentation for CLI usage and flags.
---
Ways to run
| Method | Use case |
|-------|----------|
| Docker Compose (recommended) | Run API + web app + optional CLI with one docker compose; no local Python/Ansible/Terraform. |
| Web app | Build, destroy, simulate, and share via the UI at port 4321. |
| REST API | Automate from scripts or CI; full OpenAPI docs at /openapi/swagger. |
| CLI | attack_range.py build | destroy | simulate | apply-role | share for terminal-based workflows. |
---
Documentation
---
Quick reference
config/<attack_range_id>.yml. Templates live in templates/{aws,azure,gcp}/.~/.aws, ~/.azure, or ~/.config/gcloud and mount them into the containers (see docker/docker-compose.yml).---
Support
Please use the GitHub issue tracker to submit bugs or request features.
If you ha or need support, you can:
* Join the #security-research room in the Splunk Slack channel
* Post a question to Splunk Answers
* If you are a Splunk Enterprise customer with a valid support entitlement contract and have a Splunk-related question, you can also open a support case on the support portal
---
Contributing
We welcome feedback and contributions from the community! Please see our contribution guidelines for more information on how to get in.
---
Author
* Jose Hernandez
* Patrick Bareiß
Contributors
* Bha
* Rod Soto
* Russ Nolen
* Phil Royer
* Joseph Zadeh
* Rico
* Dimitris Lambrou
* Da
* Ignacio Bermudez Corrales
* Peter Gael
* Josef Kuepker
* Shannon Davis
* Mauricio
* Teoderick Contreras
* Lou Stella
* Christian Cloutier
* Eric McGinnis
* Micheal Haag
* Gowthamaraj Rajendran
* Christopher Caldwell
* Zachary Christensen
* JerinSaji0
* Michal Cichorz
项目信息
开发语言:Python
Star 数:2564
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | attack_range - A tool that allows you to create vulnerable instru |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:57:27 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 399 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |