 漏洞知识库
点击放大
AWSGoat - AWSGoat : A Damn Vulnerable AWS Infrastructure
项目说明
AWSGoat : A Damn AWS Infrastructure
!1
Compromising an organization's cloud infrastructure is like sitting on a gold mine for attackers. And sometimes, a simple misconfiguration or a in web applications, is all an attacker needs to compromise the entire infrastructure. Since the cloud is relatively new, many de are not fully aware of the threatscape and they end up deploying a cloud infrastructure.
AWSGoat is a by design infrastructure on AWS featuring the latest released OWASP Top 10 web application security risks (2021) and other misconfiguration based on services such as IAM, S3, API Gateway, Lambda, EC2, and ECS. AWSGoat mimics real-world infrastructure but with added . It features multiple escalation paths and is focused on a black-box approach.
AWSGoat uses IaC (Terraform) to deploy the cloud infrastructure on the user's AWS account. This gives the user complete control over code, infrastructure, and en. Using AWSGoat, the user can learn/practice:
The project will be divided into modules and each module will be a separate web application, powered by tech stacks and de practices. It will le IaC through terraform and GitHub actions to ease the deployment process.
Presented at
De with :heart: by INE
<img src=" alt="drawing" width="200"/>
Built With
* AWS
* React
* Python 3
* Terraform
* PHP
* Docker
The project is scheduled to encompass all significant including the OWASP TOP 10 2021, and popular cloud misconfigurations.
Currently, the project contains the following /misconfigurations.
* XSS
* SQL Injection
* Insecure Direct Object Reference
* Server Side Request Forgery on Lambda En
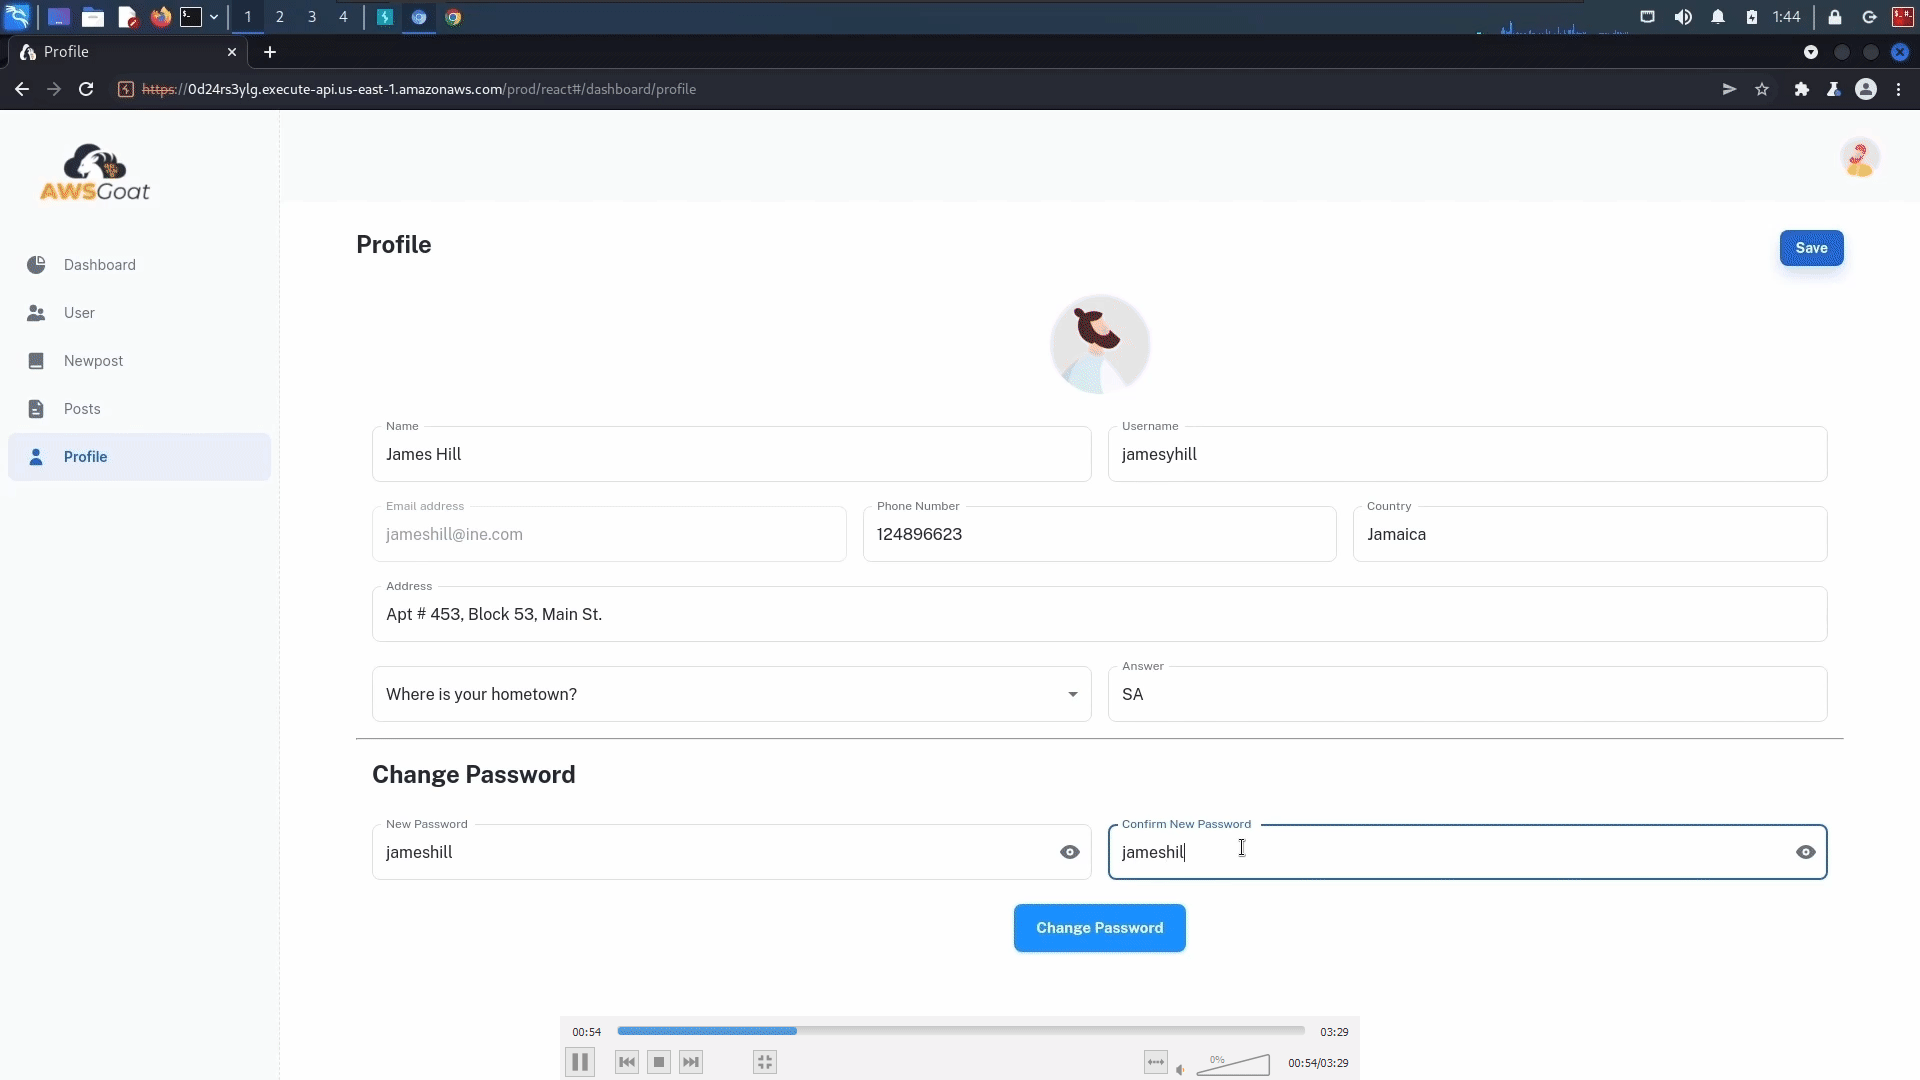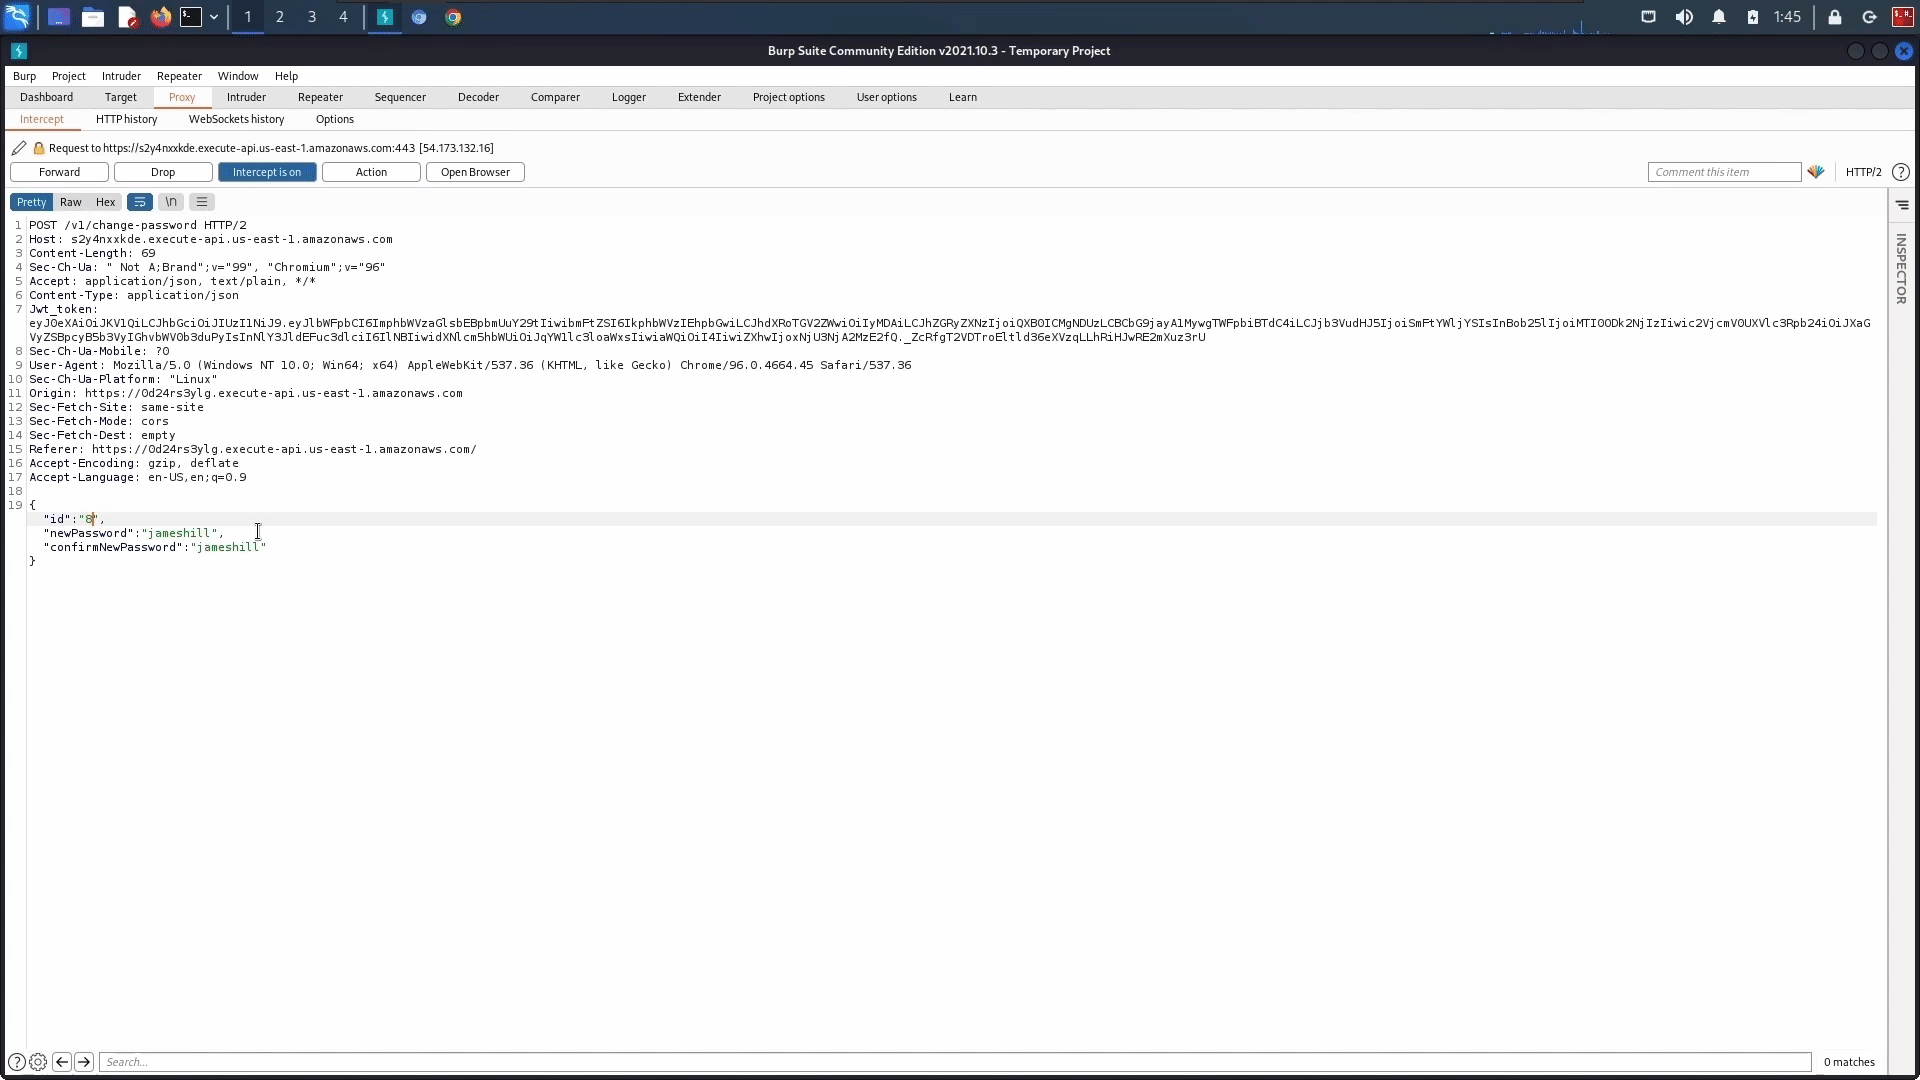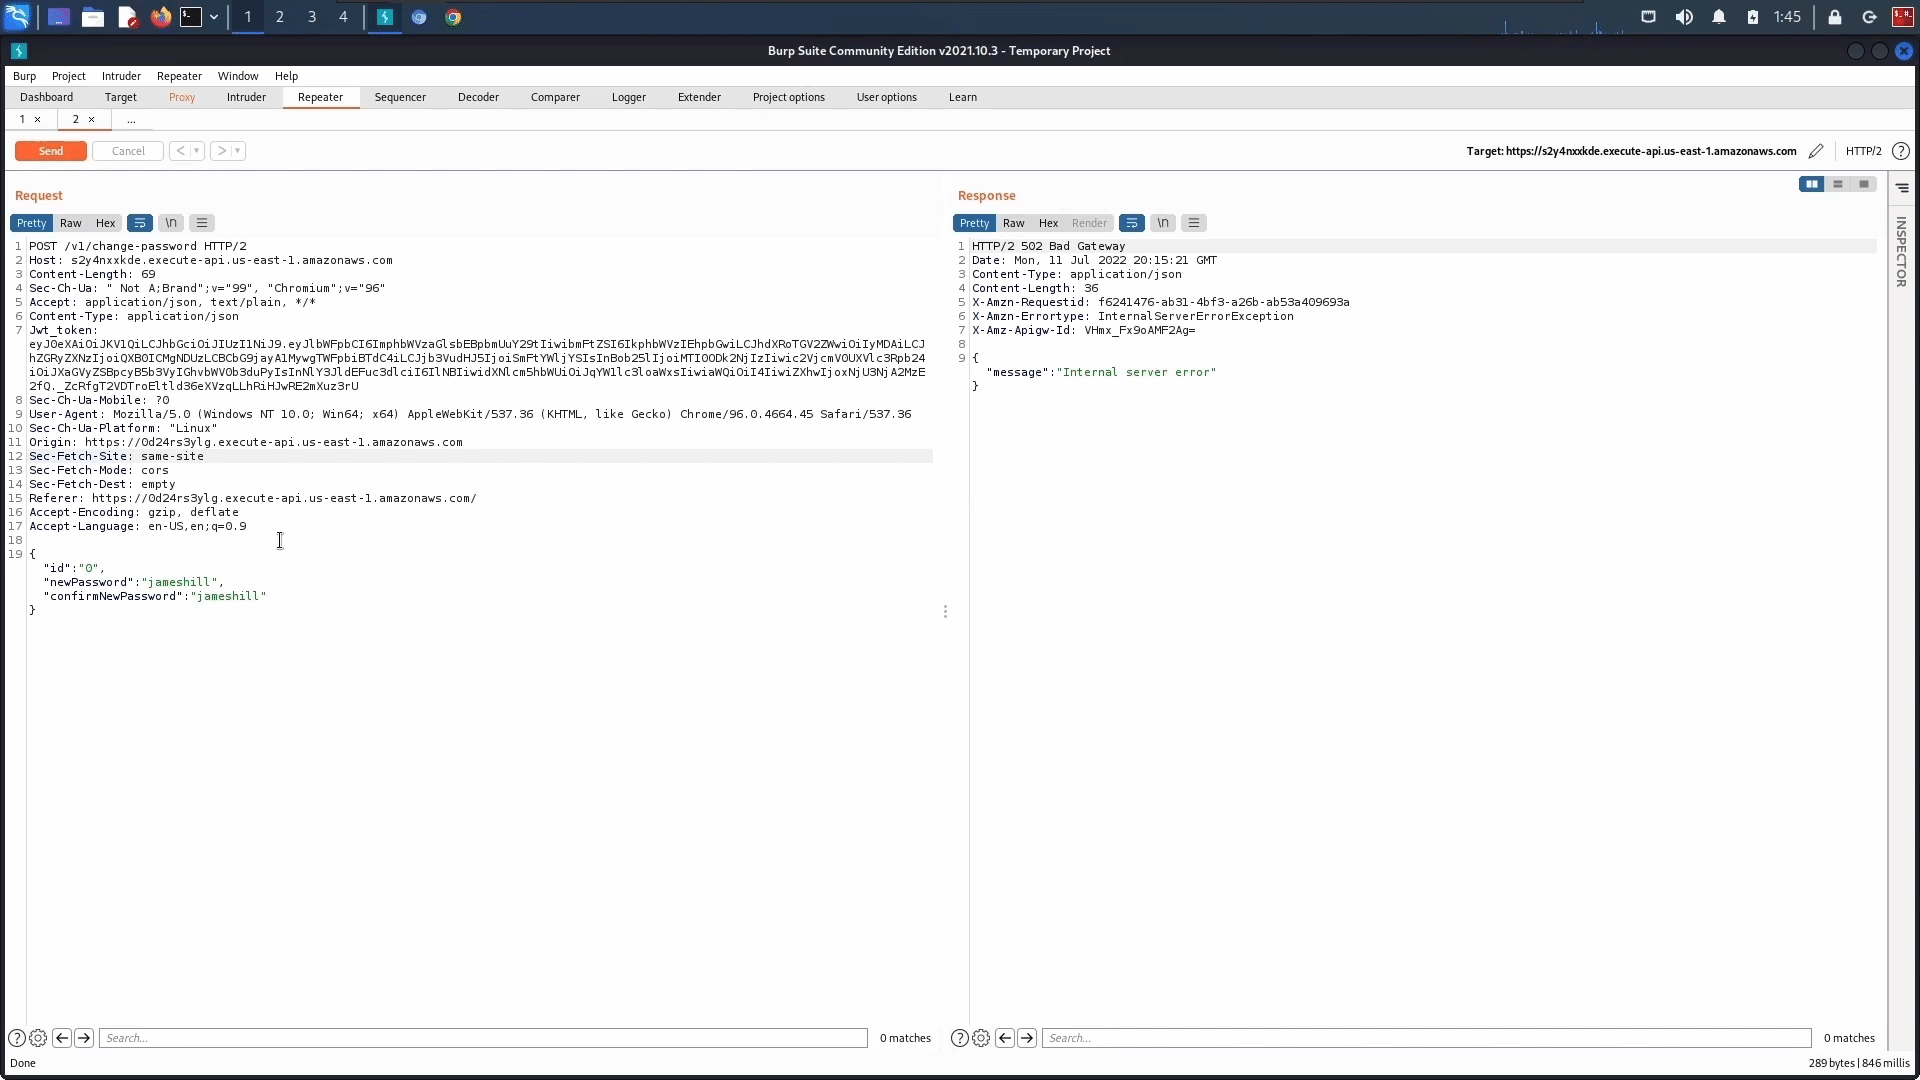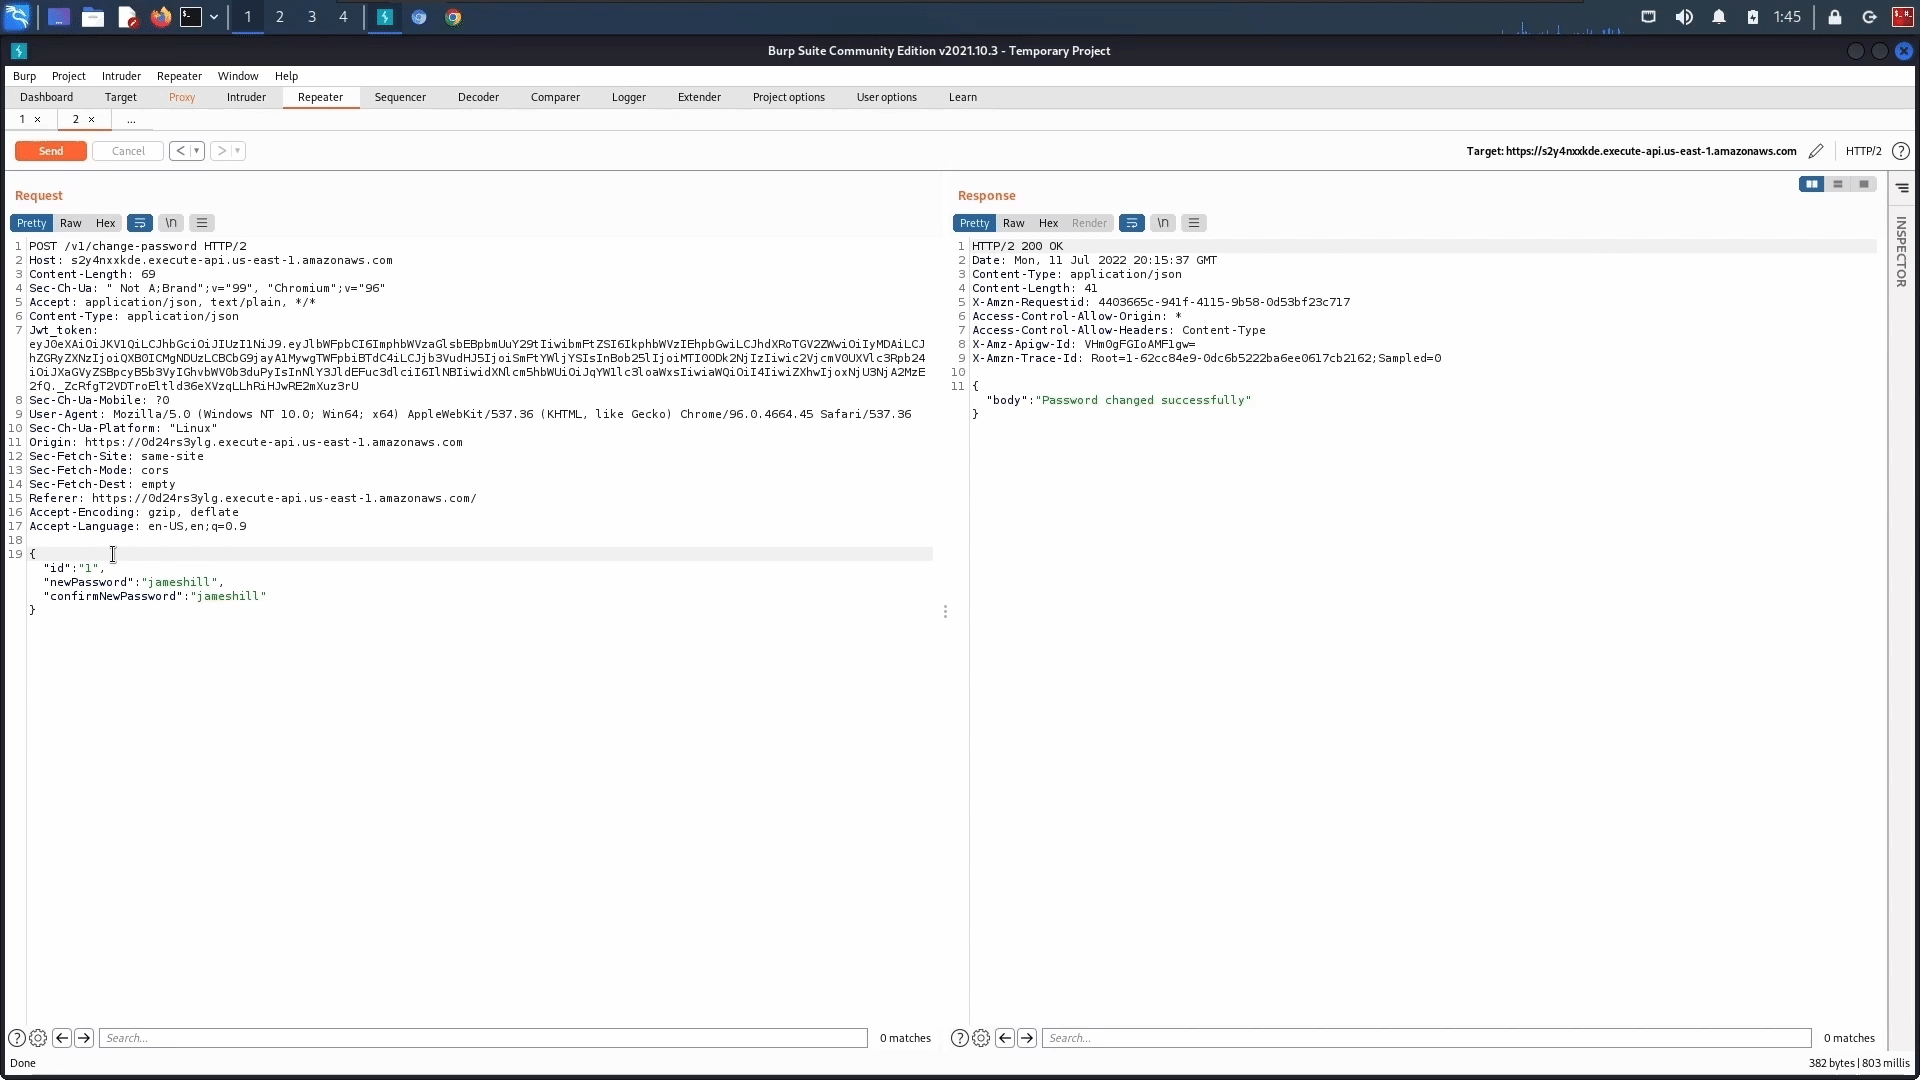
* Sensitive Data Exposure and Password Reset
* S3 Misconfigurations
* IAM Pri Escalations
* ECS Container Breakout
Getting Started
Prerequisites
* An AWS Account
* AWS Access Key with Administrati
* OR use the IAM policy in the policy.json file for the minimum permissions required for an AWS Access Key.
Installation
To ease the deployment process the user just needs to fork this repo, add their AWS Account Credentials to GitHub secrets, and run the Terraform Apply Action. This workflow will deploy the whole infrastructure and output the hosted application's URL.
Here are the steps to follow:
Step 1. Fork the repo
Step 2. Set the GitHub Action Secrets:
<p align="center">
<img src="
</p>
Step 3. From the repository actions tab, select the module to deploy and run the `Terraform Apply Workflow.
<p align="center">
<img src="
</p>
Step 4. Find the application URL in the Terraform output section.
<p align="center">
<img src="
</p>
Manual Installation
Manually installing AWSGoat would require you to follow these steps:
(Note: This requires a Linux Machine, with the /bin/bash shell a)
Step 1. Clone the repo
Step 2. Configure AWS User Account Credentials
Step 3. Traverse into the respecti' directory and use terraform to deploy AWSGoat
Modules
Module 1
The first module features a ser blog application utilizing AWS Lambda, S3, API Gateway, and DynamoDB. It consists of web application and facilitates exploitation of misconfigured AWS resources.
Escalation Path:
<p align="center">
<img src="
</p>
Module 2
The second module features an internal HR Payroll application, utilizing the AWS ECS infrastructure. It consists of web application and facilitates exploitation of misconfigured AWS resources.
Escalation Path:
<p align="center">
<img src="
</p>
Recommended Browser: Google Chrome
Pricing
The resources created with the deployment of AWSGoat will not incur any charges if the AWS account is under the free tier/trial period. However, upon exhaustion/ineligibility of the free tier/trial, the following charges will apply for the US-East region:
Module 1: $0.0125/hour
Module 2: $0.0505/hour
Contributors
Jeswin Mathai, Chief Architect, Lab Platform, INE <>
Nishant Sharma, Director, Lab Platform, INE <>
Sanjee, Software Engineer (Cloud), INE <>
Shantanu Kale, Cloud De, INE <>
Govind Krishna Lal Balaji, Cloud De, INE <>
Litesh Ghute, Software Engineer, INE <>
Solutions
The offensi are a in the attack-manuals directory, and the defensi are a in the defence-manuals directory.
Module 1 Exploitation : <
![11]()
Documentation
For more details refer to the "AWSGoat.pdf" PDF file. This file contains the slide deck used for presentations.
Screenshots
Module 1:
<p align="center">
<img src="
</p>
<p align="center">
<img src="
</p>
<p align="center">
<img src="
</p>
<p align="center">
<img src="
</p>
Module 2:
<p align="center">
<img src="
</p>
<p align="center">
<img src="
</p>
Contribution Guidelines
* Contributions in the form of code impro, module updates, feature impro, and any general suggestions are welcome.
* Impro to the functionalities of the current modules are also welcome.
* The source code for each module can be found in modules/module-<Number>/src` this can be used to modify the existing application code.
License
This program is free software: you can redistribute it and/or modify it under the terms of the MIT License.
You should ha a copy of the MIT License along with this program. If not, see
Sister Projects
项目信息
开发语言:PHP
Star 数:2052
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AWSGoat : A Damn Vulnerable AWS Infrastructure展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AWSGoat - AWSGoat : A Damn Vulnerable AWS Infrastructure |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:58:25 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 283 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |