 漏洞知识库
点击放大
NucleiFuzzer - NucleiFuzzer is a robust automation tool that effi
项目说明
<h1 align="center">
NucleiFuzzer = Nuclei + Paramspider + waybackurls + gauplus + hakrawler + katana + Fuzzing Templates
<br>
</h1>
<p align="center">
<a href=" src="
<a href=" src="
<a href=" src="
</p>
O
NucleiFuzzer is an ad automation tool designed to streamline and optimize web application security testing by integrating a suite of powerful URL discovery and scanning tools. It combines ParamSpider, Waybackurls, Katana, Gauplus, and Hakrawler to comprehensively gather and enumerate potential entry points for web applications. Le the power of Nuclei, it scans these endpoints using fuzzing-templates to effectively uncover a wide range of .The enhanced NucleiFuzzer is built for speed and accuracy, utilizing ad URL , deduplication with uro, and precise HTTP filtering using httpx. This tool provides security professionals, bug bounty hunters, and web de with a seamless workflow to detect and address security risks, ensuring robust web application protection.
Key Features:
1. Comprehensive URL Discovery: Integrates multiple tools (
ParamSpider, Waybackurls, Katana, Gauplus, and Hakrawler) to ensure exhausti of URLs and parameters.2. Enhanced Scanning: Uses
Nuclei with fuzzing-templates to identify critical security issues with precision.3. Ad Filtering and : Remo and irrelevant results using
uro and httpx for cleaner and more focused scanning.4. Rate Limiting for Efficiency: Allows customizable request rates for optimal performance during scans.
5. Customizable and User-Friendly: Easy-to-configure options for domains, files, and output directories, catering to both indi and batch scans.
Take ad of NucleiFuzzer to safeguard your web applications against and attacks with an enhanced, efficient, and reliable security testing solution!
Note: Nuclei + Paramspider + waybackurls + gauplus + hakrawler + katana + Fuzzing Templates = NucleiFuzzer <br><br>
Important: Make sure the tools Nuclei, Paramspider, waybackurls, gauplus, hakrawler, katana, httpx & uro are installed on your machine and executing correctly to use the NucleiFuzzer without any issues.
✨ New Features (Updated)
Tools included:
git clone <br>git clone <br>git clone <br>git clone <br>git clone <br>git clone <br>git clone <br>Templates:
Fuzzing Templates
git clone Screenshot
<img width="1067" height="559" alt="image" src=" />
Output
<img width="1733" height="901" alt="image" src=" />
Usage
This will display help for the tool. Here are the options it supports.
Installation:
To install NucleiFuzzer, follow these steps:
Examples:
Here are a few examples of how to use NucleiFuzzer:
NucleiFuzzer on a single domain:NucleiFuzzer on multiple domains from a file:Practical Demonstration:
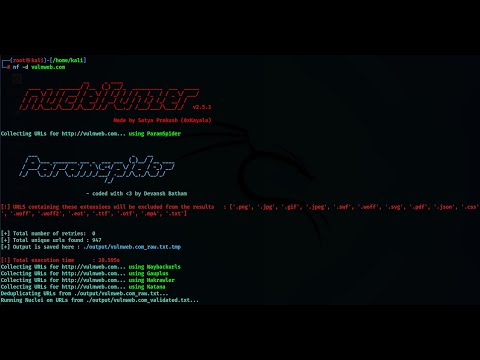
For a Practical Demonstration of the NucleiFuzzer tool see the below video 👇 <br>
<img src=" width="600" height="300"/>
Star History
<a href="
<picture>
<source media="(prefers-color-scheme: dark)" srcset=" />
<source media="(prefers-color-scheme: light)" srcset=" />
<img alt="Star History Chart" src=" />
</picture>
</a>
Contributing
Contributions are welcome! If you'd like to contribute to NucleiFuzzer, please follow these steps:
1. Fork the repository.
2. Create a new branch.
3. Make your changes and commit them.
4. Submit a pull request.
Made bySatya Prakash | 0xKayala \
A Security Researcher and Bug Hunter \
Connect with me:
<p align="left">
<a href=" target="blank"><img align="center" src=" alt="0xkayala" height="30" width="40" /></a>
<a href=" target="blank"><img align="center" src=" alt="0xkayala" height="30" width="40" /></a>
<a href=" target="blank"><img align="center" src=" alt="0xkayala" height="30" width="40" /></a>
<a href=" target="blank"><img align="center" src=" alt="@0xkayala" height="30" width="40" /></a>
<a href=" target="blank"><img align="center" src=" alt="0xkayala" height="30" width="40" /></a>
</p>
Support me:
<p><a href=" <img align="left" src=" height="50" width="210" alt="0xKayala" /></a></p><br><br>
项目信息
开发语言:Python
Star 数:1863
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕NucleiFuzzer is a robust automation tool that efficiently detects web application vulnerabilities, including XSS, SQLi, SSRF, and Open Redirects, leveraging advanced scanning and URL enumeration techniques展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | NucleiFuzzer - NucleiFuzzer is a robust automation tool that effi |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 00:58:55 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 377 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |