 漏洞知识库
点击放大
sast-skills - Collection of agent skills to find vulnerabilities
项目说明
LLM SAST Skills
A collection of agent skills that turn your LLM coding assistant into a fully functional SAST scanner to find in your codebase. Works natively with Claude Code, Codex, Opencode, Cursor and any other assistant that supports agent skills. No third-party tools required.
Claude Code with Opus model is recommended. But if the cost is a concern, use any IDE and model you trust.
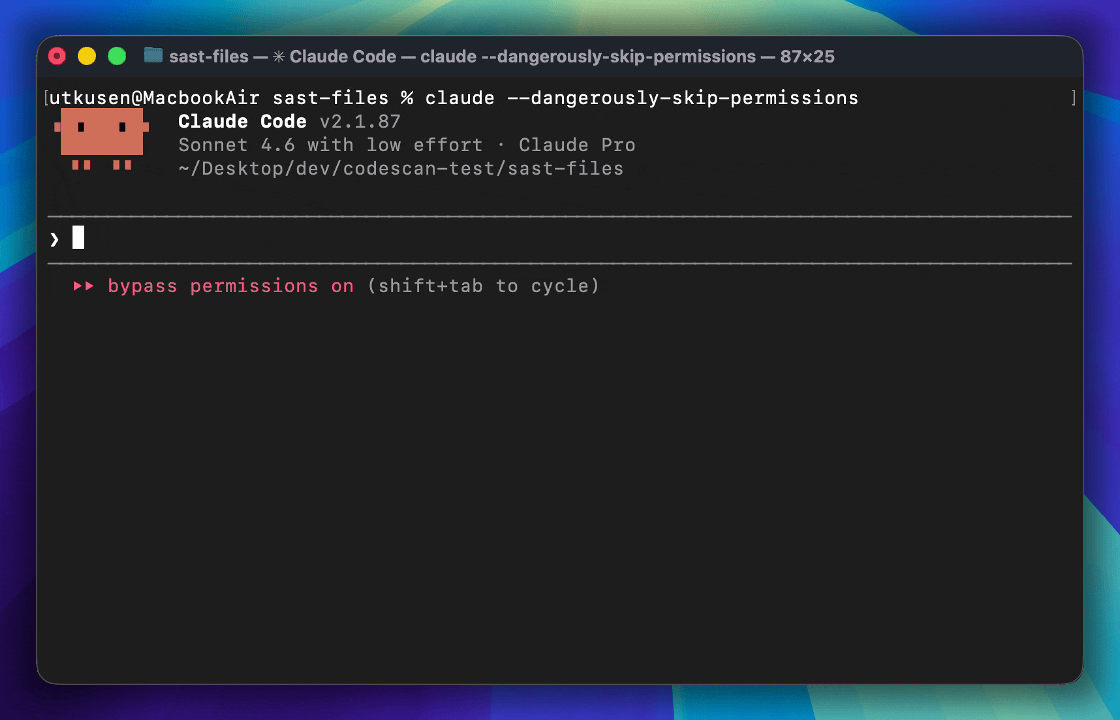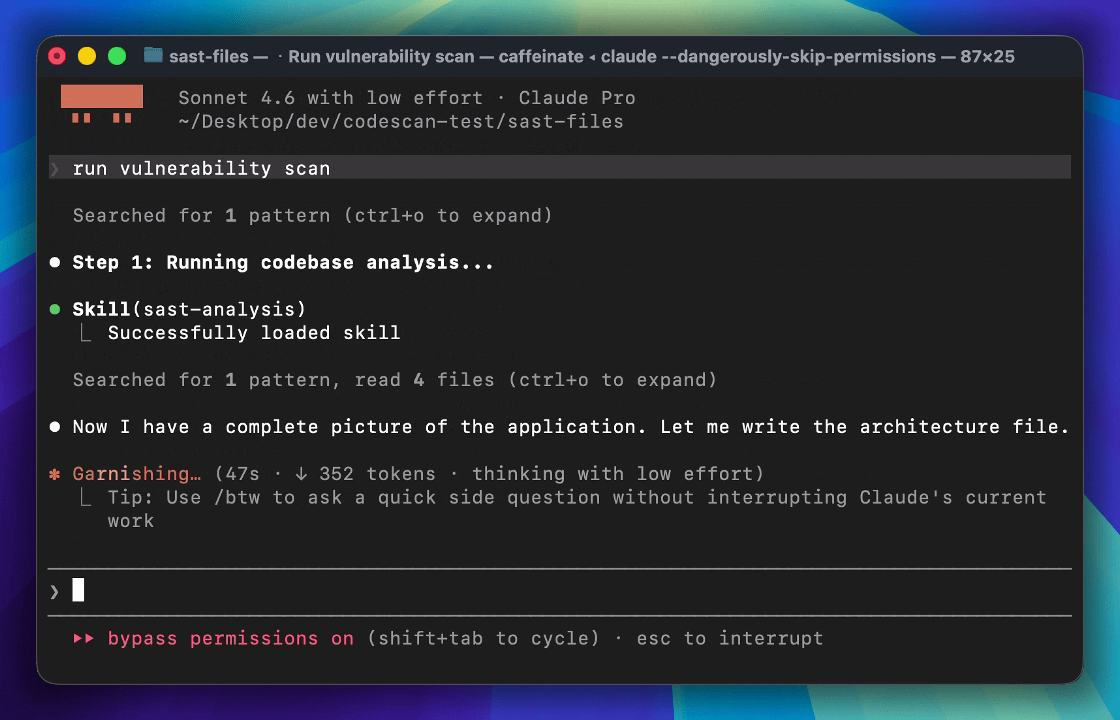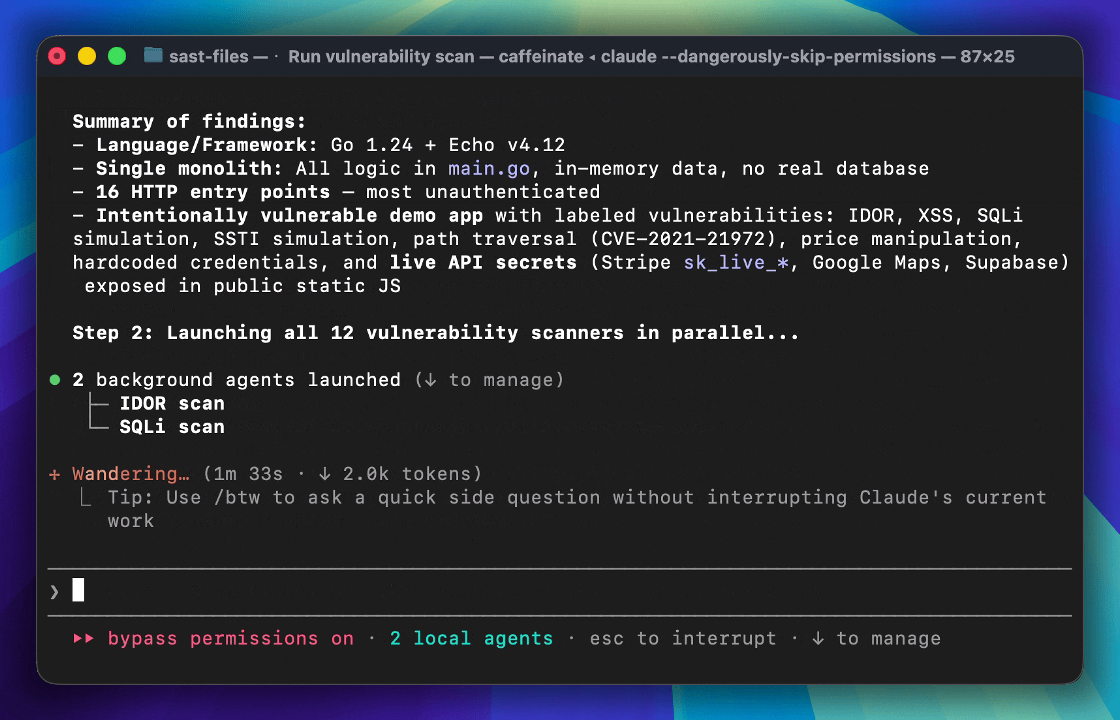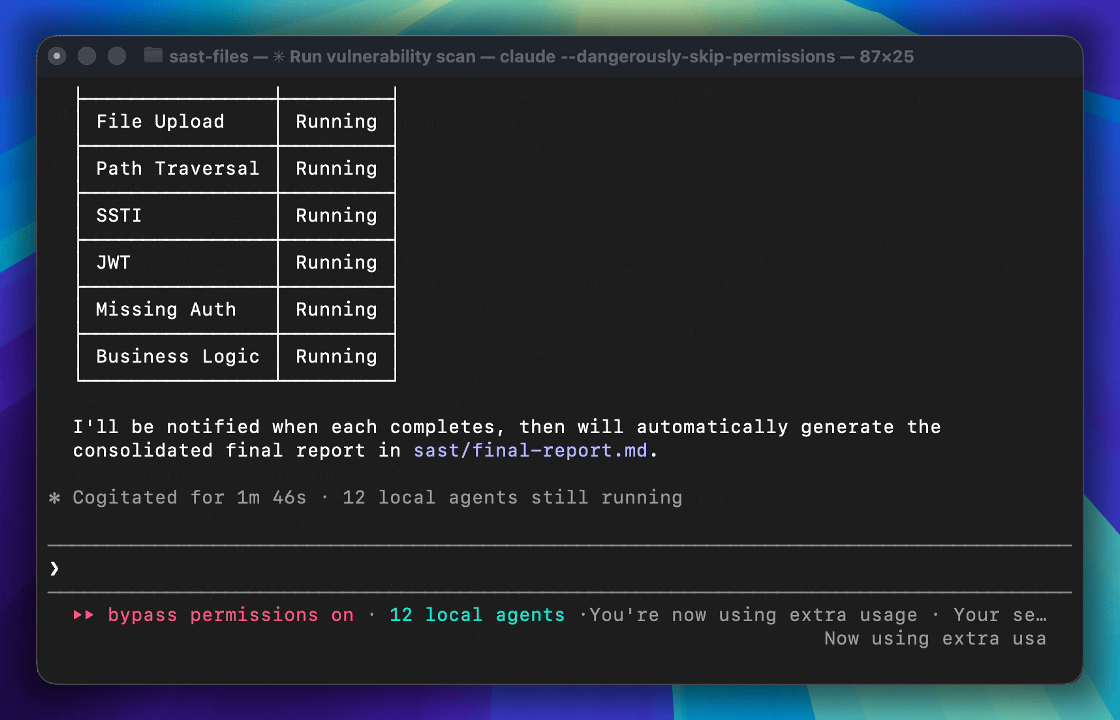
!Process in Claude Code
How It Works
CLAUDE.md (for Claude Code) or AGENTS.md (for Opencode and other IDEs) orchestrates the entire assessment workflow automatically. The assessment runs in three steps:
1. Codebase Analysis -- The sast-analysis skill maps the technology stack, architecture, entry points, data flows, and trust boundaries. It writes its findings to sast/architecture.md.
2. Detection (parallel) -- All 13 detection skills run in parallel as subagents. Each skill follows a two-phase approach: first a recon/discovery phase to find candidate sections, then a phase to confirm exploitability. Results are written to sast/*-results.md.
3. Report Generation -- The sast-report skill consolidates all findings into a single sast/final-report.md, ranked by se with full remediation guidance and dynamic test instructions.
What It Detects
| Skill | Class |
|---|---|
| sast-analysis | Codebase reconnaissance, architecture mapping, threat modeling |
| sast-sqli | SQL Injection |
| sast-graphql | GraphQL injection |
| sast-xss | Cross-Site Scripting (XSS) |
| sast-rce | Remote Code Execution (command injection, eval, unsafe deserialization) |
| sast-ssrf | Ser Request Forgery |
| sast-idor | Insecure Direct Object Reference |
| sast-xxe | XML External Entity |
| sast-ssti | Ser Template Injection |
| sast-jwt | Insecure JWT implementations |
| sast-missingauth | Missing authentication and broken function-le |
| sast-pathtra | Path / directory tra |
| sast-fileupload | Insecure file upload |
| sast-businesslogic | Business logic flaws (price manipulation, workflow bypass, race conditions, etc.) |
| sast-report | Consolidated final report ranked by se |
Installation
Copy your project into the sast-files folder, then open sast-files as your workspace in your AI coding assistant.
> Note: If your project already contains a CLAUDE.md or AGENTS.md file, remove it before running the assessment — otherwise it will conflict with the orchestration file provided by this toolkit.
Usage
After copying the files, open your project in your AI coding assistant and ask:
> Run scan
or
> Find in this codebase
The entry point file (CLAUDE.md or AGENTS.md) orchestrates the full workflow automatically. It will skip any steps whose output files already exist, so you can safely re-run it after fixing issues.
Output
All output is written to a sast/ folder in your project root:
| File | Description |
|---|---|
| sast/architecture.md | Technology stack, architecture, entry points, data flows |
| sast/*-results.md | Per- findings with proof and remediation |
| sast/final-report.md | Consolidated report ranked by se |
项目信息
开发语言:未知
Star 数:1325
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Collection of agent skills to find vulnerabilities inside your web/mobile apps.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | sast-skills - Collection of agent skills to find vulnerabilities |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:01:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 119 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |