 漏洞知识库
点击放大
singularity - A DNS rebinding attack framework.
项目说明
Singularity of Origin
Recent updates:
the Singularity of Origin.
Singularity of Origin is a tool to perform DNS rebinding attacks.
It includes the necessary components to rebind the IP address of the attack server DNS name to the target machine's IP address and to ser payloads to exploit software on the target machine.
It also ships with sample payloads to exploit several software , from the simple capture of a home page to performing remote code execution. It aims at pro a framework to facilitate the exploitation of software to DNS rebinding attacks and to raise awareness on how they work and how to protect from them.
Detailed documentation is on the wiki pages.
Core Features
- Custom DNS server to rebind DNS name and IP address
- HTTP server (manager web interface) to serve HTML pages and Ja code to targets and to manage the attacks
- Several sample attack payloads, ranging from grabbing the home page of a target application to performing remote code execution. These payloads can be easily adapted to perform new and custom attacks.
- Supports DNS CNAME in target specification in addition to IP addresses to evade DNS filtering solutions or to target internal resources for which the IP address is unknown.
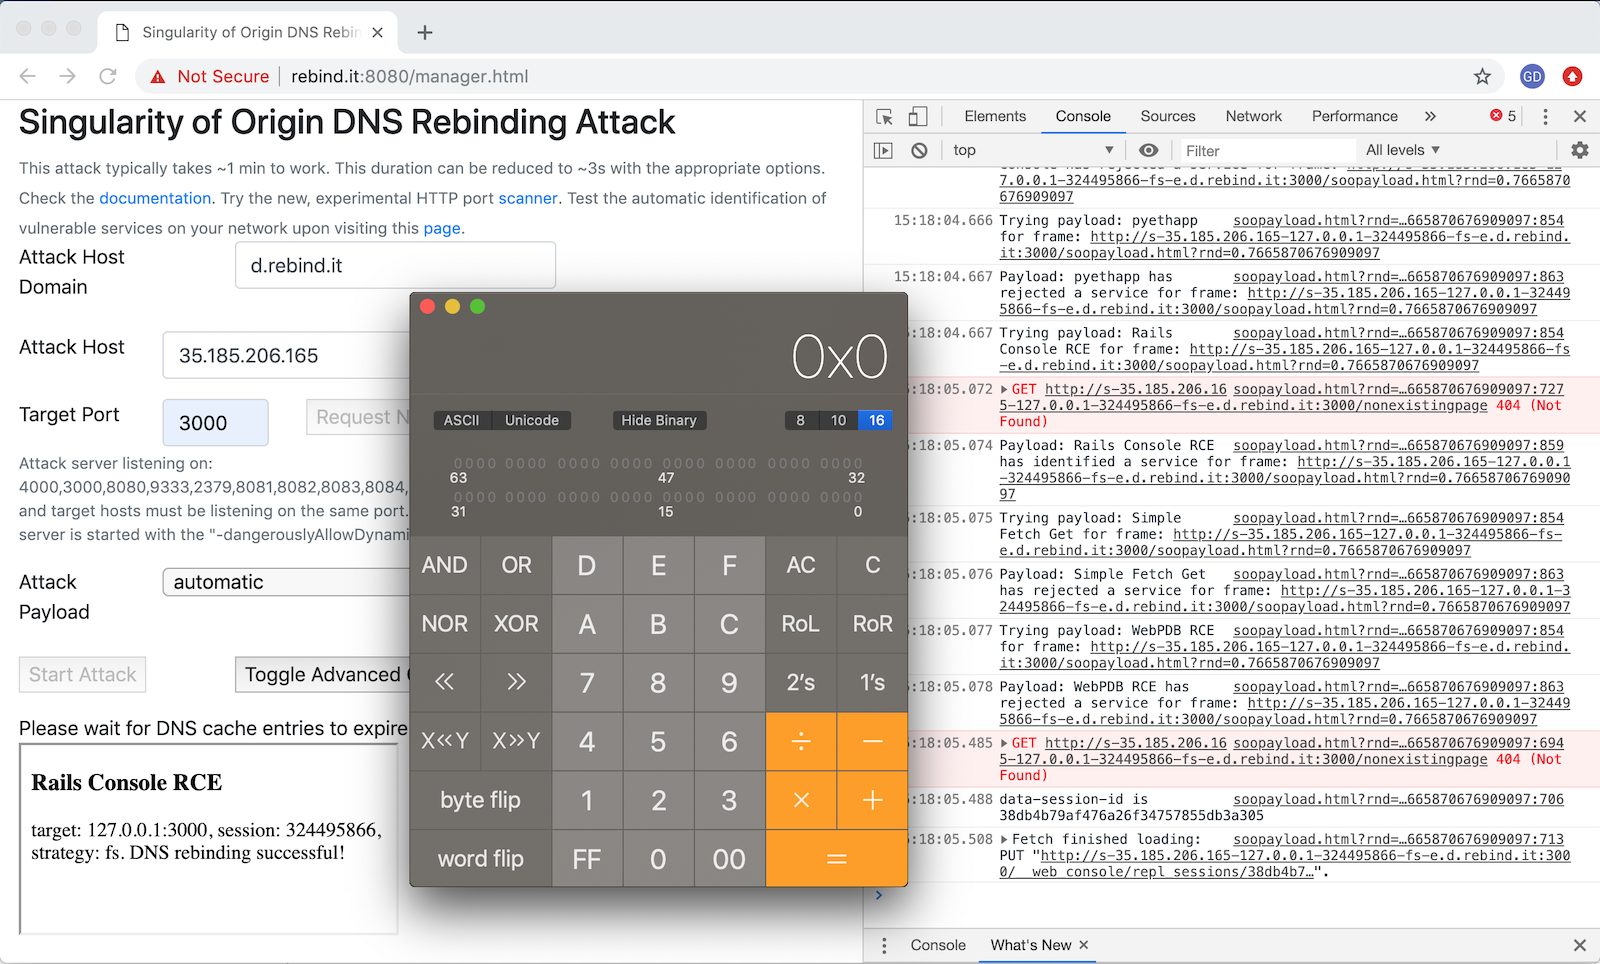
Singularity Manager Interface
!Singularity Manager Interface
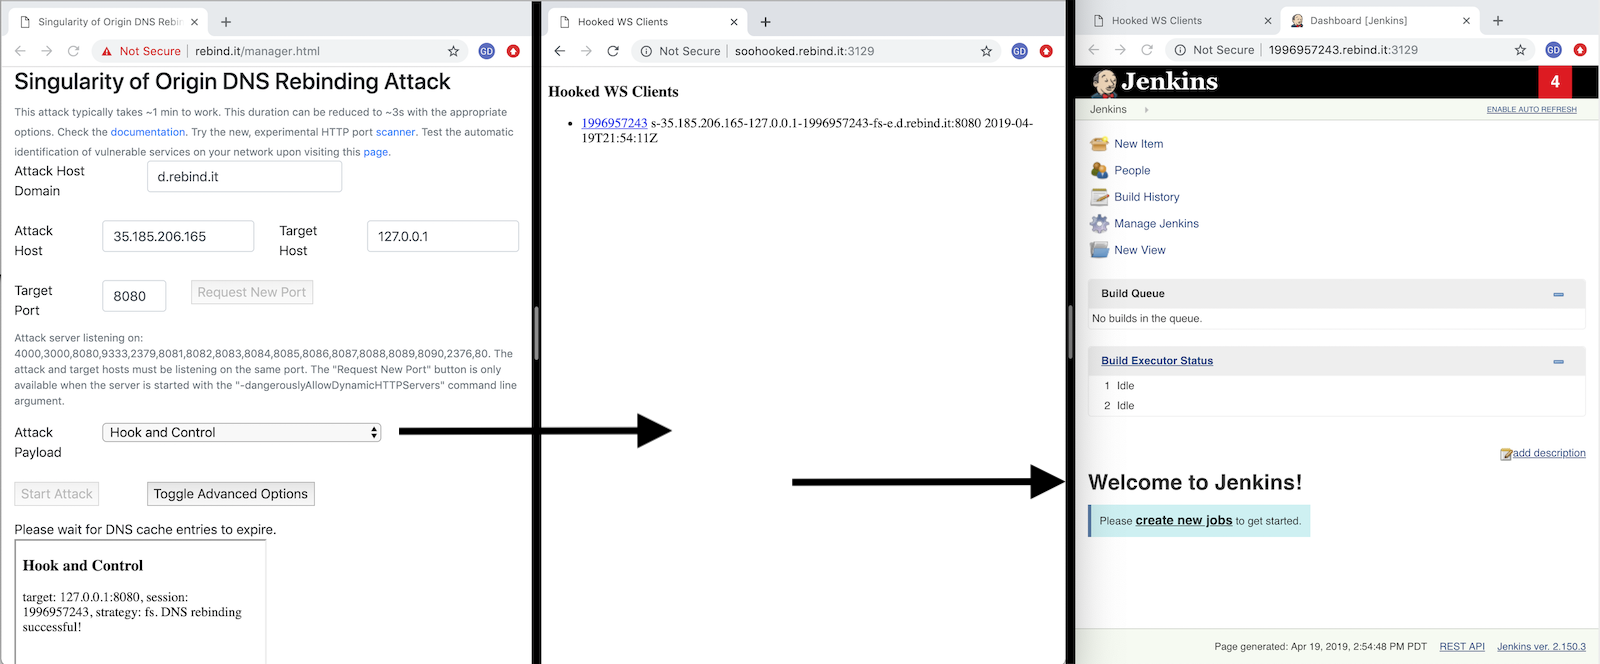
Hook and Control a Application on Localhost or Other Hosts
!Fetch an application home page
Automate the Scan and Compromise of All Applications
!Fetch an application home page
Usage
Setting up Singularity requires a DNS domain name where you can edit your own
DNS records for your domain and a Linux server to run it.
Please see the setup singularity wiki page for detailed instructions.
The documentation is on the wiki pages.
Here are a few pointers to start:
A test instance is a for demo purposes at
Speed
Singularity has been tested to work with the following browsers in optimal conditions in under 3 seconds:
| Browser | Operating System | Time to Exploit | Rebinding Strategy | Fetch Interval | Target Specification |
| --- | --- | --- | --- | ---| ---|
| ~~Chrome~~ | ~~Windows 10~~ | <s>~3s</s> | ~~Multiple answers (fast)~~ | ~~1s~~ | ~~127.0.0.1~~ |
| ~~Edge~~ | ~~Windows 10~~ | <s>~3s</s> | ~~Multiple answers (fast)~~ | ~~1s~~ | ~~127.0.0.1~~ |
| Firefox | Windows 10 | ~3s | Multiple answers (fast) | 1s | 127.0.0.1 |
| Chromium | Ubuntu | ~3s | Multiple answers (fast) | 1s | 0.0.0.0 |
| Firefox | Ubuntu | ~3s | Multiple answers (fast) | 1s | 0.0.0.0 |
| Chrome | macOS | ~3s | Multiple answers (fast) | 1s |0.0.0.0 |
| Firefox | macOS | ~3s | Multiple answers (fast) | 1s |0.0.0.0 |
| Safari | macOS | ~3s | Multiple answers (fast) | 1s |0.0.0.0 |
Payloads Description
Singularity supports the following attack payloads:
* Basic fetch request (simple-fetch-get.js): This sample payload
makes a GET request to the root directory ('/') and shows the ser
using the fetch API.
The goal of this payload is to function as example request to make additional
contributions as easy as possible.
* automatic: This payload automatically attempts to detect known services and exploit them using other payloads listed in this section or that were de and added to Singularity by users.
* Chrome De RCE (exposed-chrome-de.js): This payload
demonstrates a remote code execution (RCE) in Microsoft VS Code fixed in 1.19.3.
This payload can be adapted to exploit any software that exposes Chrome De on localhost.
* Etcd k/v dump (etcd.js): This payload retrieves the keys and from
the etcd key-value store.
* pyethapp (pyethapp.js): Exploits the Python implementation of the
Ethereum client Pyethapp to get the
list of owned eth addresses and retrieve the balance of the first eth address.
* Rails Console RCE (rails-console-rce.js): Performs a remote code
execution (RCE) attack on the Rails Web Console.
* AWS Metadata Exfil (aws-metadata-exfil.js): Forces a headless browser to exfiltrate AWS metadata
including private keys to a given host. Check the payload contents for additional details on how to setup
the attack.
* Duplicati RCE (duplicati-rce.js): This payload exploits the
Duplicati backup client and performs a remote code execution (RCE) attack.
For this attack to work, parameter targetURL in file payload-duplicati-rce.html must be updated to
point to a valid Duplicati backup containing the actual RCE payload,
a shell script.
* WebPDB (webpdb.js): A generic RCE payload to exploit PDB,
a python debugger exposed .
* Hook and Control (hook-and-control.js): Hijack target browsers and use them to access inaccessible resources from your own browser or other HTTP clients. You can retrieve the list of hooked browsers on the "soohooked" sub-domain of the Singularity manager host on port 3129 by default e.g. To authenticate, submit the secret value dumped to the console by the Singularity server at startup.
* Jenkins Script Console (jenkins-script-console.js): This payload exploits the
Jenkins Script Console
and displays the stored credentials.
* Docker API (docker-api.js): This payload exploits the
Docker API
and displays the /etc/shadow file of the Docker host.
* Ollama Llama2 Exfil (ollama-exfil.js): Exfiltrate files from hosts running Ollama, an open-source system for running and managing large language models (LLMs). See blog post.
* And more, check the payloads folder (html/payloads).
项目信息
开发语言:JavaScript
Star 数:1321
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A DNS rebinding attack framework.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | singularity - A DNS rebinding attack framework. |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:01:25 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 109 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |