 漏洞知识库
点击放大
secator - secator - the pentester's swiss knife
项目说明
<h1 align="center">
<img src=" width="400">
</h1>
<h4 align="center">The pentester's swiss knife.</h4>
<p align="center">
<!-- <a href=" src=" -->
<img src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
</p>
<p align="center">
<a href="#features">Features</a> •
<a href="#supported-commands">Supported commands</a> •
<a href="#install-secator">Installation</a> •
<a href="#usage">Usage</a> •
<a href=" •
<a href=" us on Discord !</a>
</p>
secator is a task and workflow runner used for security assessments. It supports dozens of well-known security tools
and it is designed to impro for pentesters and security researchers.
Features

* Curated list of commands
* Unified input options
* Unified output schema
* CLI and library usage
* Distributed options with Celery
* Complexity from simple tasks to complex workflows
* Customizable
Supported tools
secator integrates the following tools:
<!-- START_TOOLS_TABLE -->
| Name | Description | Category |
|-----------------------------------------------------------------|----------------------------------------------------------------------------------|-------------------|
| arjun | HTTP Parameter Discovery Suite. | url/fuzz/params |
| arp | Display the system ARP cache. | ip/recon |
| arpscan | Scan a CIDR range for ali using ARP. | ip/recon |
| bbot | Multipurpose scanner. | vuln/scan |
| bup | 40X bypasser. | url/bypass |
| cariddi | Crawl endpoints, secrets, api keys, extensions, tokens... | url/crawl |
| dalfox | Powerful open source XSS scanning tool. | url/fuzz |
| dirsearch | Ad web path brute-forcer. | url/fuzz |
| dnsx | dnsx is a fast and multi-purpose DNS toolkit designed for running retryabledns library. | dns/fuzz |
| feroxbuster | Simple, fast, recursi discovery tool written in Rust | url/fuzz |
| ffuf | Fast web fuzzer written in Go. | url/fuzz |
| fping | Send ICMP echo probes to network hosts, similar to ping, but much better. | ip/recon |
| gau | Fetch known URLs from AlienVault's Open Threat Exchange, the Wayback Machine, Common Crawl, and URLScan. | pattern/scan |
| getasn | Get ASN information from IP address. | ip/probe |
| gf | Wrapper around grep, to help you grep for things. | pattern/scan |
| gitleaks | Tool for detecting secrets like passwords, API keys, and tokens in git repos, files, and stdin. | secret/scan |
| gospider | Fast web spider written in Go. | url/crawl |
| grype | scanner for container images and filesystems. | vuln/scan |
| h8mail | Email information and password lookup tool. | user/recon/email |
| httpx | Fast and multi-purpose HTTP toolkit. | url/probe |
| jswhois | WHOIS in JSON format | domain/info |
| katana | Next-generation crawling and spidering framework. | url/crawl |
| maigret | Collect a dossier on a person by username. | user/recon/username |
| mapcidr | Utility program to perform multiple operations for a gi/cidr ranges. | ip/recon |
| msfconsole | CLI to access and work with the Metasploit Framework. | exploit/attack |
| naabu | Port scanning tool written in Go. | port/scan |
| nmap | Network Mapper is a free and open source utility for network discovery and security auditing. | port/scan |
| nuclei | Fast and customisable scanner based on simple YAML based DSL. | vuln/scan |
| search_vulns | Search for known in software by product name or CPE. | vuln/recon |
| searchsploit | Exploit searcher based on ExploitDB. | exploit/recon |
| sshaudit | SSH server & client security auditing (banner, key exchange, encryption, mac, compression, etc). | ssh/audit/security |
| subfinder | Fast passi enumeration tool. | dns/recon |
| testssl | SSL/TLS security scanner, including ciphers, protocols and cryptographic flaws. | dns/recon/tls |
| trivy | Comprehensive and security scanner. | vuln/scan |
| trufflehog | Tool for finding secrets in git repositories and filesystems using TruffleHog. | secret/scan |
| urlfinder | Find URLs in text. | pattern/scan |
| wafw00f | Web Application Firewall Fingerprinting tool. | waf/scan |
| whois | The whois tool retrie information about domain names and IP addresses. | |
| wpprobe | Fast wordpress plugin enumeration tool. | vuln/scan/wordpress |
| wpscan | Wordpress security scanner. | vuln/scan/wordpress |
| x8 | Hidden parameters discovery suite written in Rust. | url/fuzz/params |
| xurlfind3r | Discover URLs for a gi in a simple, passive and efficient way | url/recon |
<!-- END_TOOLS_TABLE -->
Feel free to request new tools to be added by opening an issue, but please
check that the tool complies with our selection criterias before doing so. If it doesn't but you still want to integrate it into secator, you can plug it in (see the de).
Installing secator
<details>
<summary>Bash</summary>
*Note: Supports optional flags --, --templates, --addons, and --tools — run the script with --help for details.*
</details>
<details>
<summary>Pipx</summary>
*Note: Make sure to have pipx installed.*
</details>
<details>
<summary>Pip</summary>
</details>
<details>
<summary>Docker</summary>
The mount -v is necessary to save all secator reports to your host machine, and--net=host is recommended to grant full access to the host network.
You can alias this command to run it easier:
Now you can run secator like if it was installed on baremetal:
</details>
<details>
<summary>Docker Compose</summary>
</details>
*Note:* If you chose the Docker or Docker Compose installation methods, you can skip the next sections and go straight to Usage.
Usage

Usage examples
To get a complete cheatsheet of what you can do with secator, please read the output of:
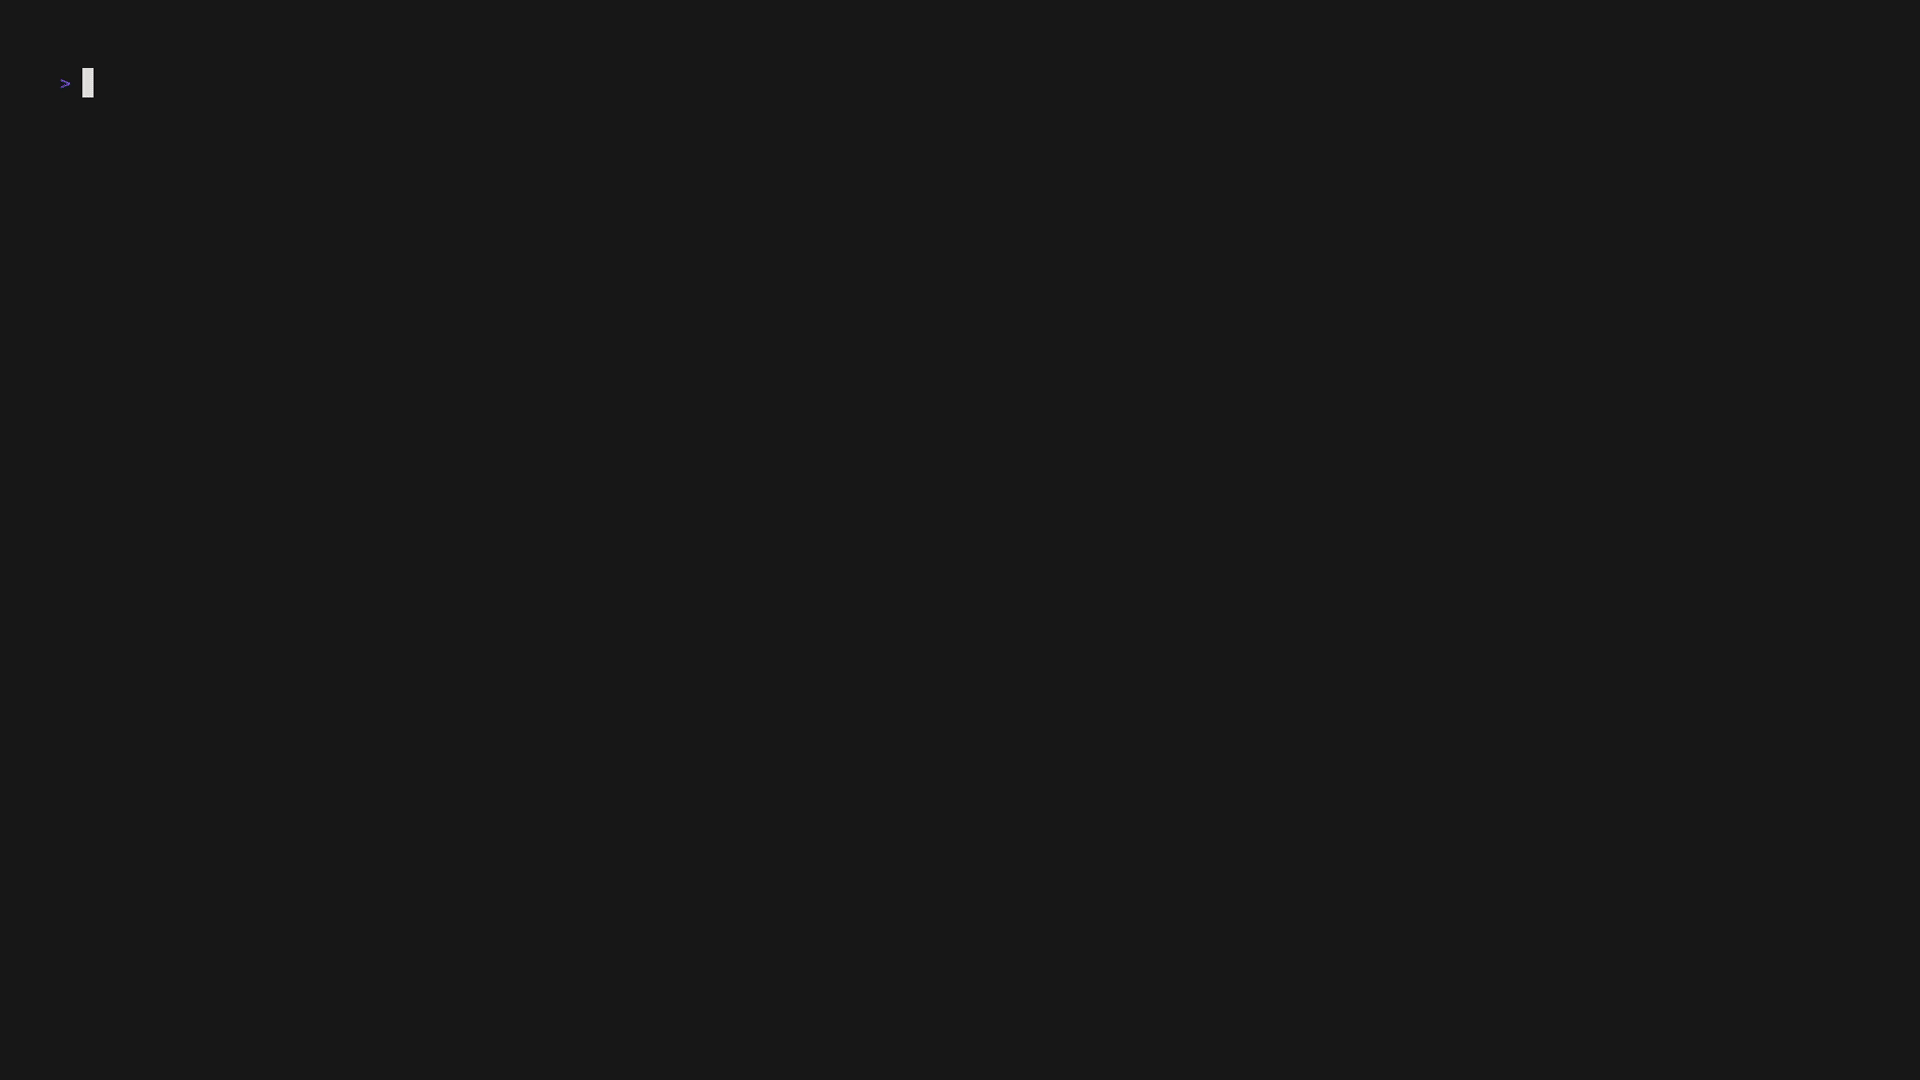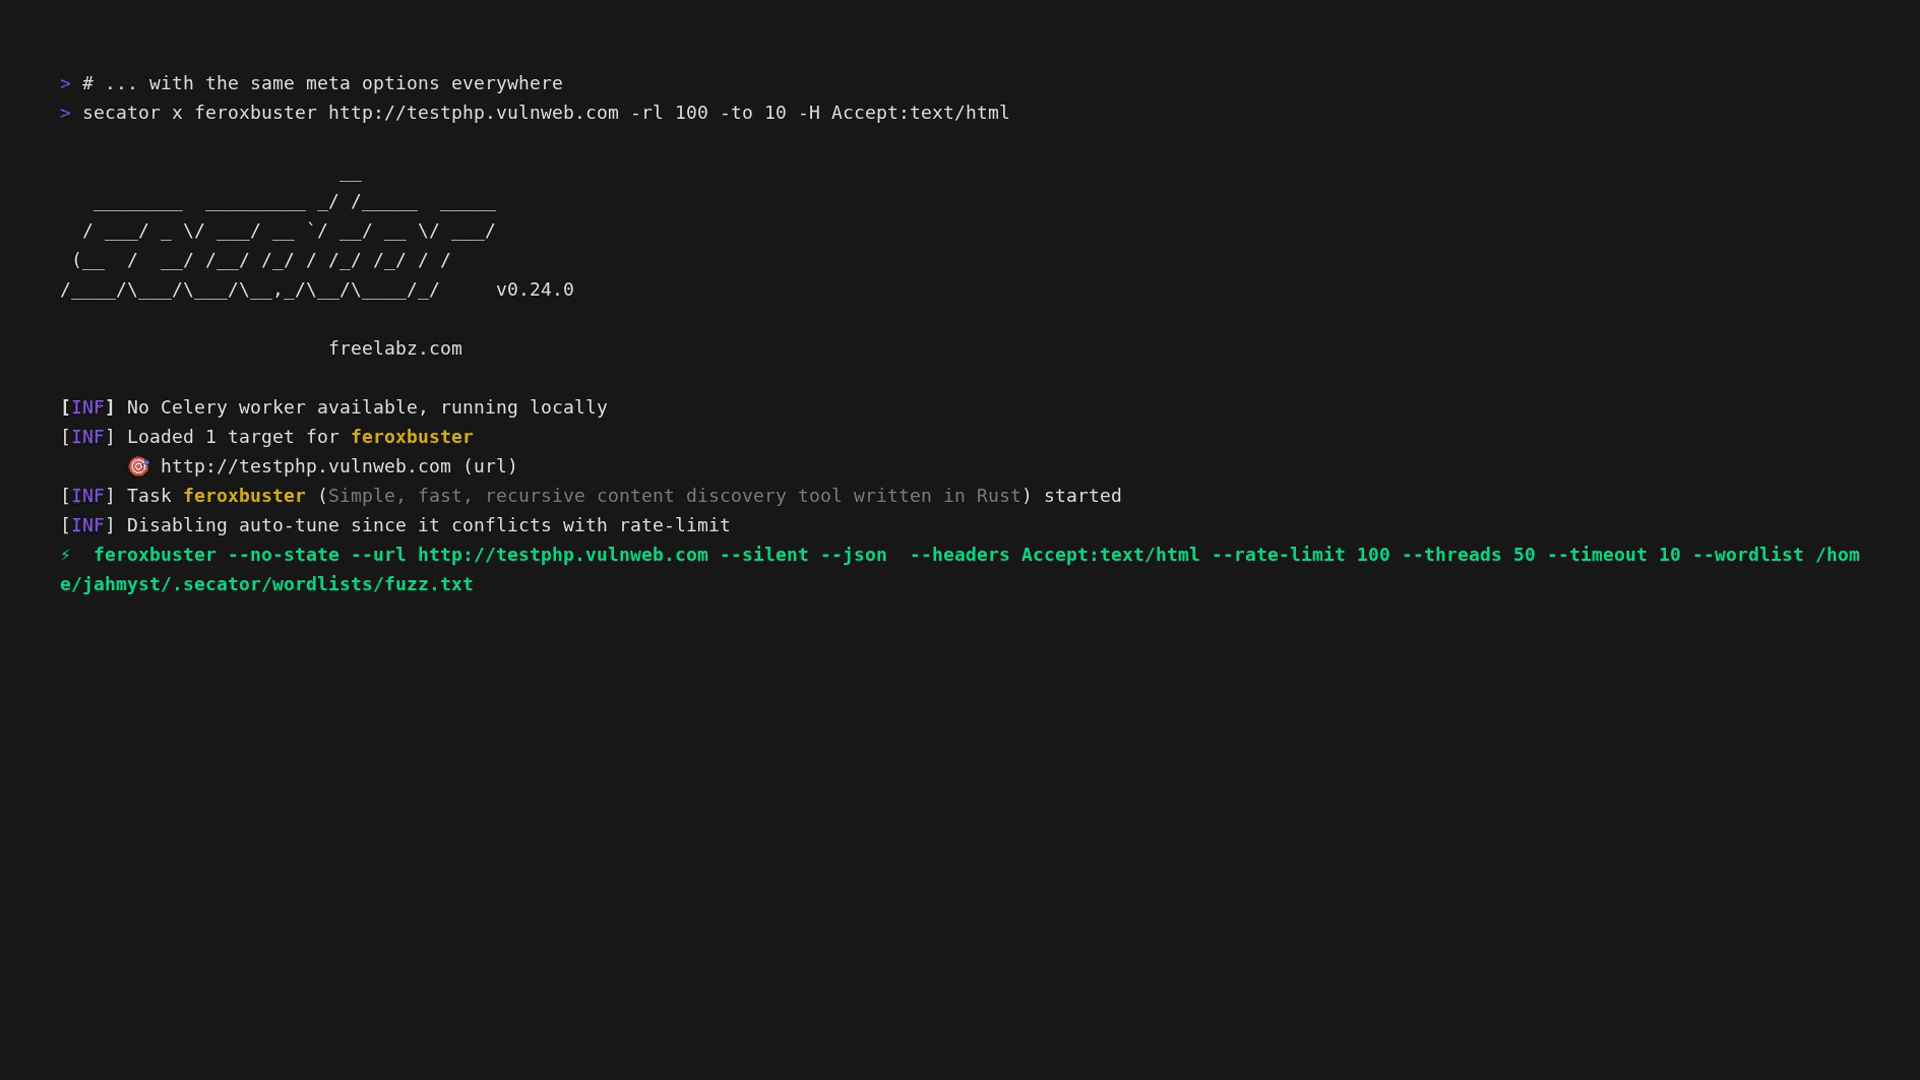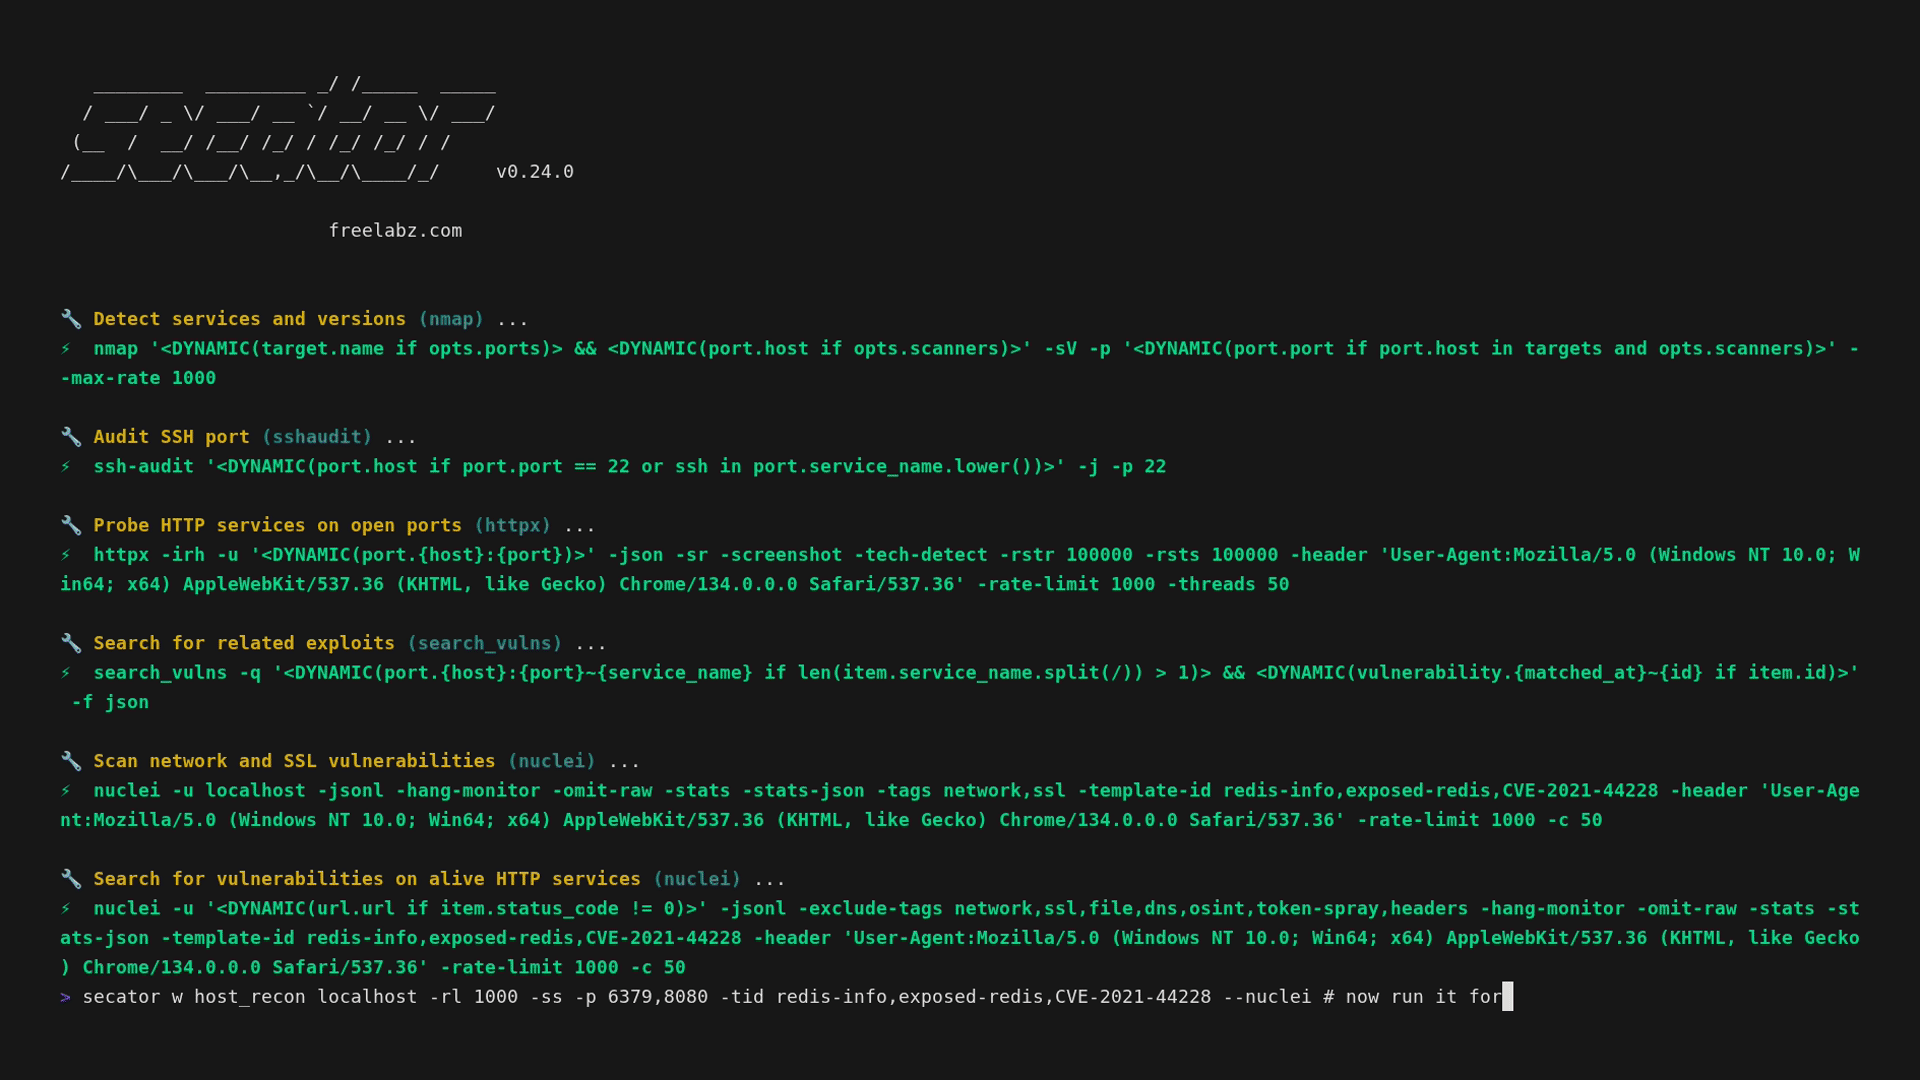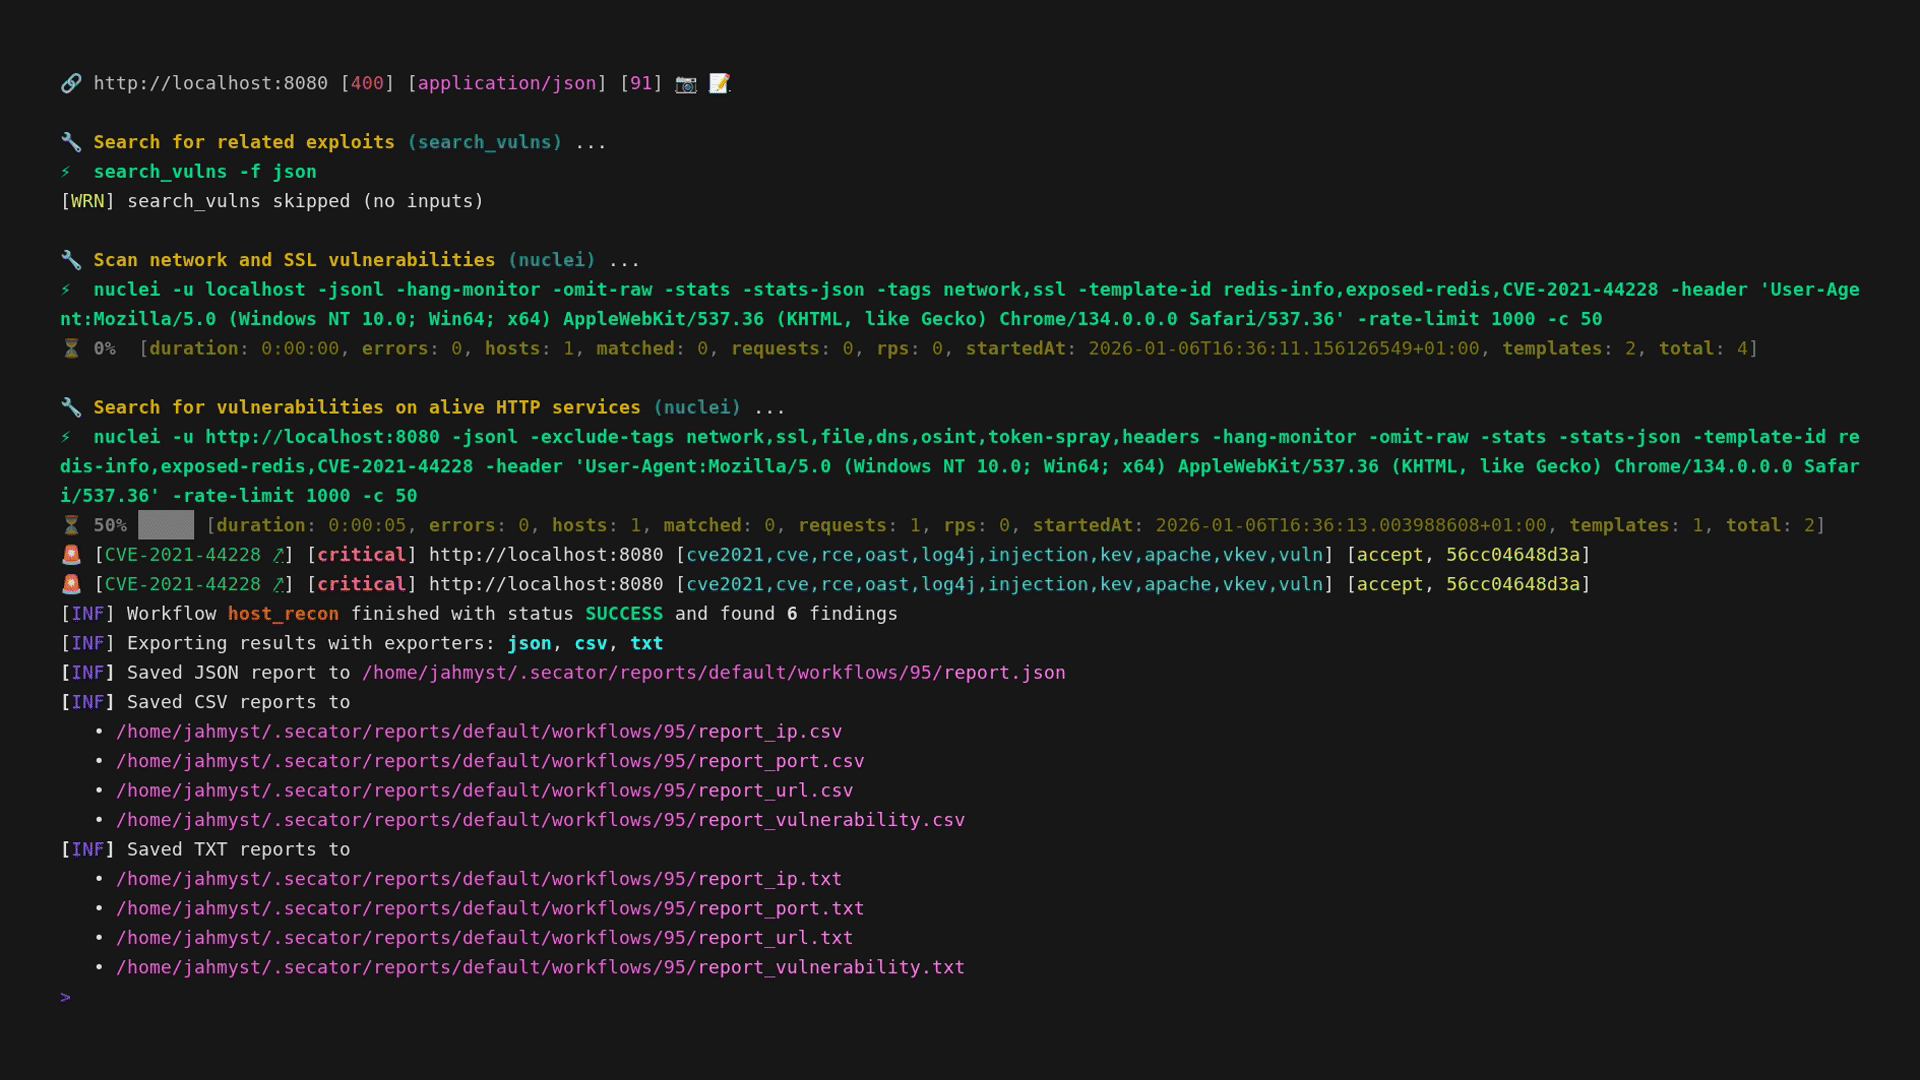
Run a fuzzing task (ffuf):
Run a url crawl workflow:
Run a host scan:
To list all tasks / workflows / scans that you can use:
To figure out which languages or tools are installed on your system (along with their ):
Queries
secator lets you query all previous reports with the secator query (or secator q) command, and re-use queries.
secator q <arg> resolves its argument in three steps:
1. Sa name — if <arg> matches a sa, its expression is used.
2. Filter expression — if <arg> looks like a filter (contains ==, <, ~=, &&, …), it is passed straight through.
3. Natural language — otherwise it is sent to AI chat (secator x ai --mode chat).
secator q accepts the same options as secator r show (-o/--output,-d/--time-delta, -f/--format, -w/-ws/--workspace, --driver, --dedupe),
plus -rf/--report-filter to scope the query to specific runner paths (the
equi of r show's REPORT_QUERY argument). On the AI-chat path only the
workspace and prompt are used.
Shell completion
secator supports shell completion for bash, zsh, and fish. This provides auto-completion for:
nmap, httpx, nuclei)url_crawl, subdomain_recon)host, domain, network)--profiles, --workspace, --driver, --outputTo install shell completion:
Bash:
Zsh:
Fish:
After installation, you can use tab completion:
Installing tools
secator auto-installs tools when you first use them.
You can prevent this behavior by setting security.autoinstall_commands to false using either secator config set security.autoinstall_commands false or SECATOR_SECURITY_AUTOINSTALL_COMMANDS=0.
To install all tools, you can still run:
Installing addons
Addons are a for
secator, please check our docs for details.For instance, using the mongodb addon allows you to send runner results to MongoDB.
Learn more
To go deeper with secator, check out:
* Our complete documentation
* Our getting started tutorial video
* Our Medium post
* Follow us on social media: on Twitter and on YouTube
Stats
<a href="
<picture>
<source media="(prefers-color-scheme: dark)" srcset=" />
<source media="(prefers-color-scheme: light)" srcset=" />
<img alt="Star History Chart" src=" />
</picture>
</a>
项目信息
开发语言:Python
Star 数:1314
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕secator - the pentester's swiss knife展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | secator - secator - the pentester's swiss knife |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:01:36 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 135 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |