 漏洞知识库
点击放大
dep-scan - OWASP dep-scan is a next-generation security and r
项目说明
Introduction
OWASP dep-scan is a next-generation security and risk audit tool based on known , ad, and license limitations for project dependencies. Both local repositories and container images are supported as the input, and the tool is ideal for integration with ASPM/ and in CI en.
<img src="depscan-logo.png" width="200" height="auto" />
![SBOM]() ![release]()
Contents
- Precise reachable data-flows
- Reachability matrix
- Rust reachability (via rusi)
- Go reachability ()
- .NET reachability ()
- J, Python, and PHP reachability (via atom)
- Data sources
- Linux distros
- Scanning projects locally (Python )
- Standalone binaries (no Python or Node.js required)
- Scanning containers locally (Python )
- Scanning projects locally (Docker container)
- Server mode
Features
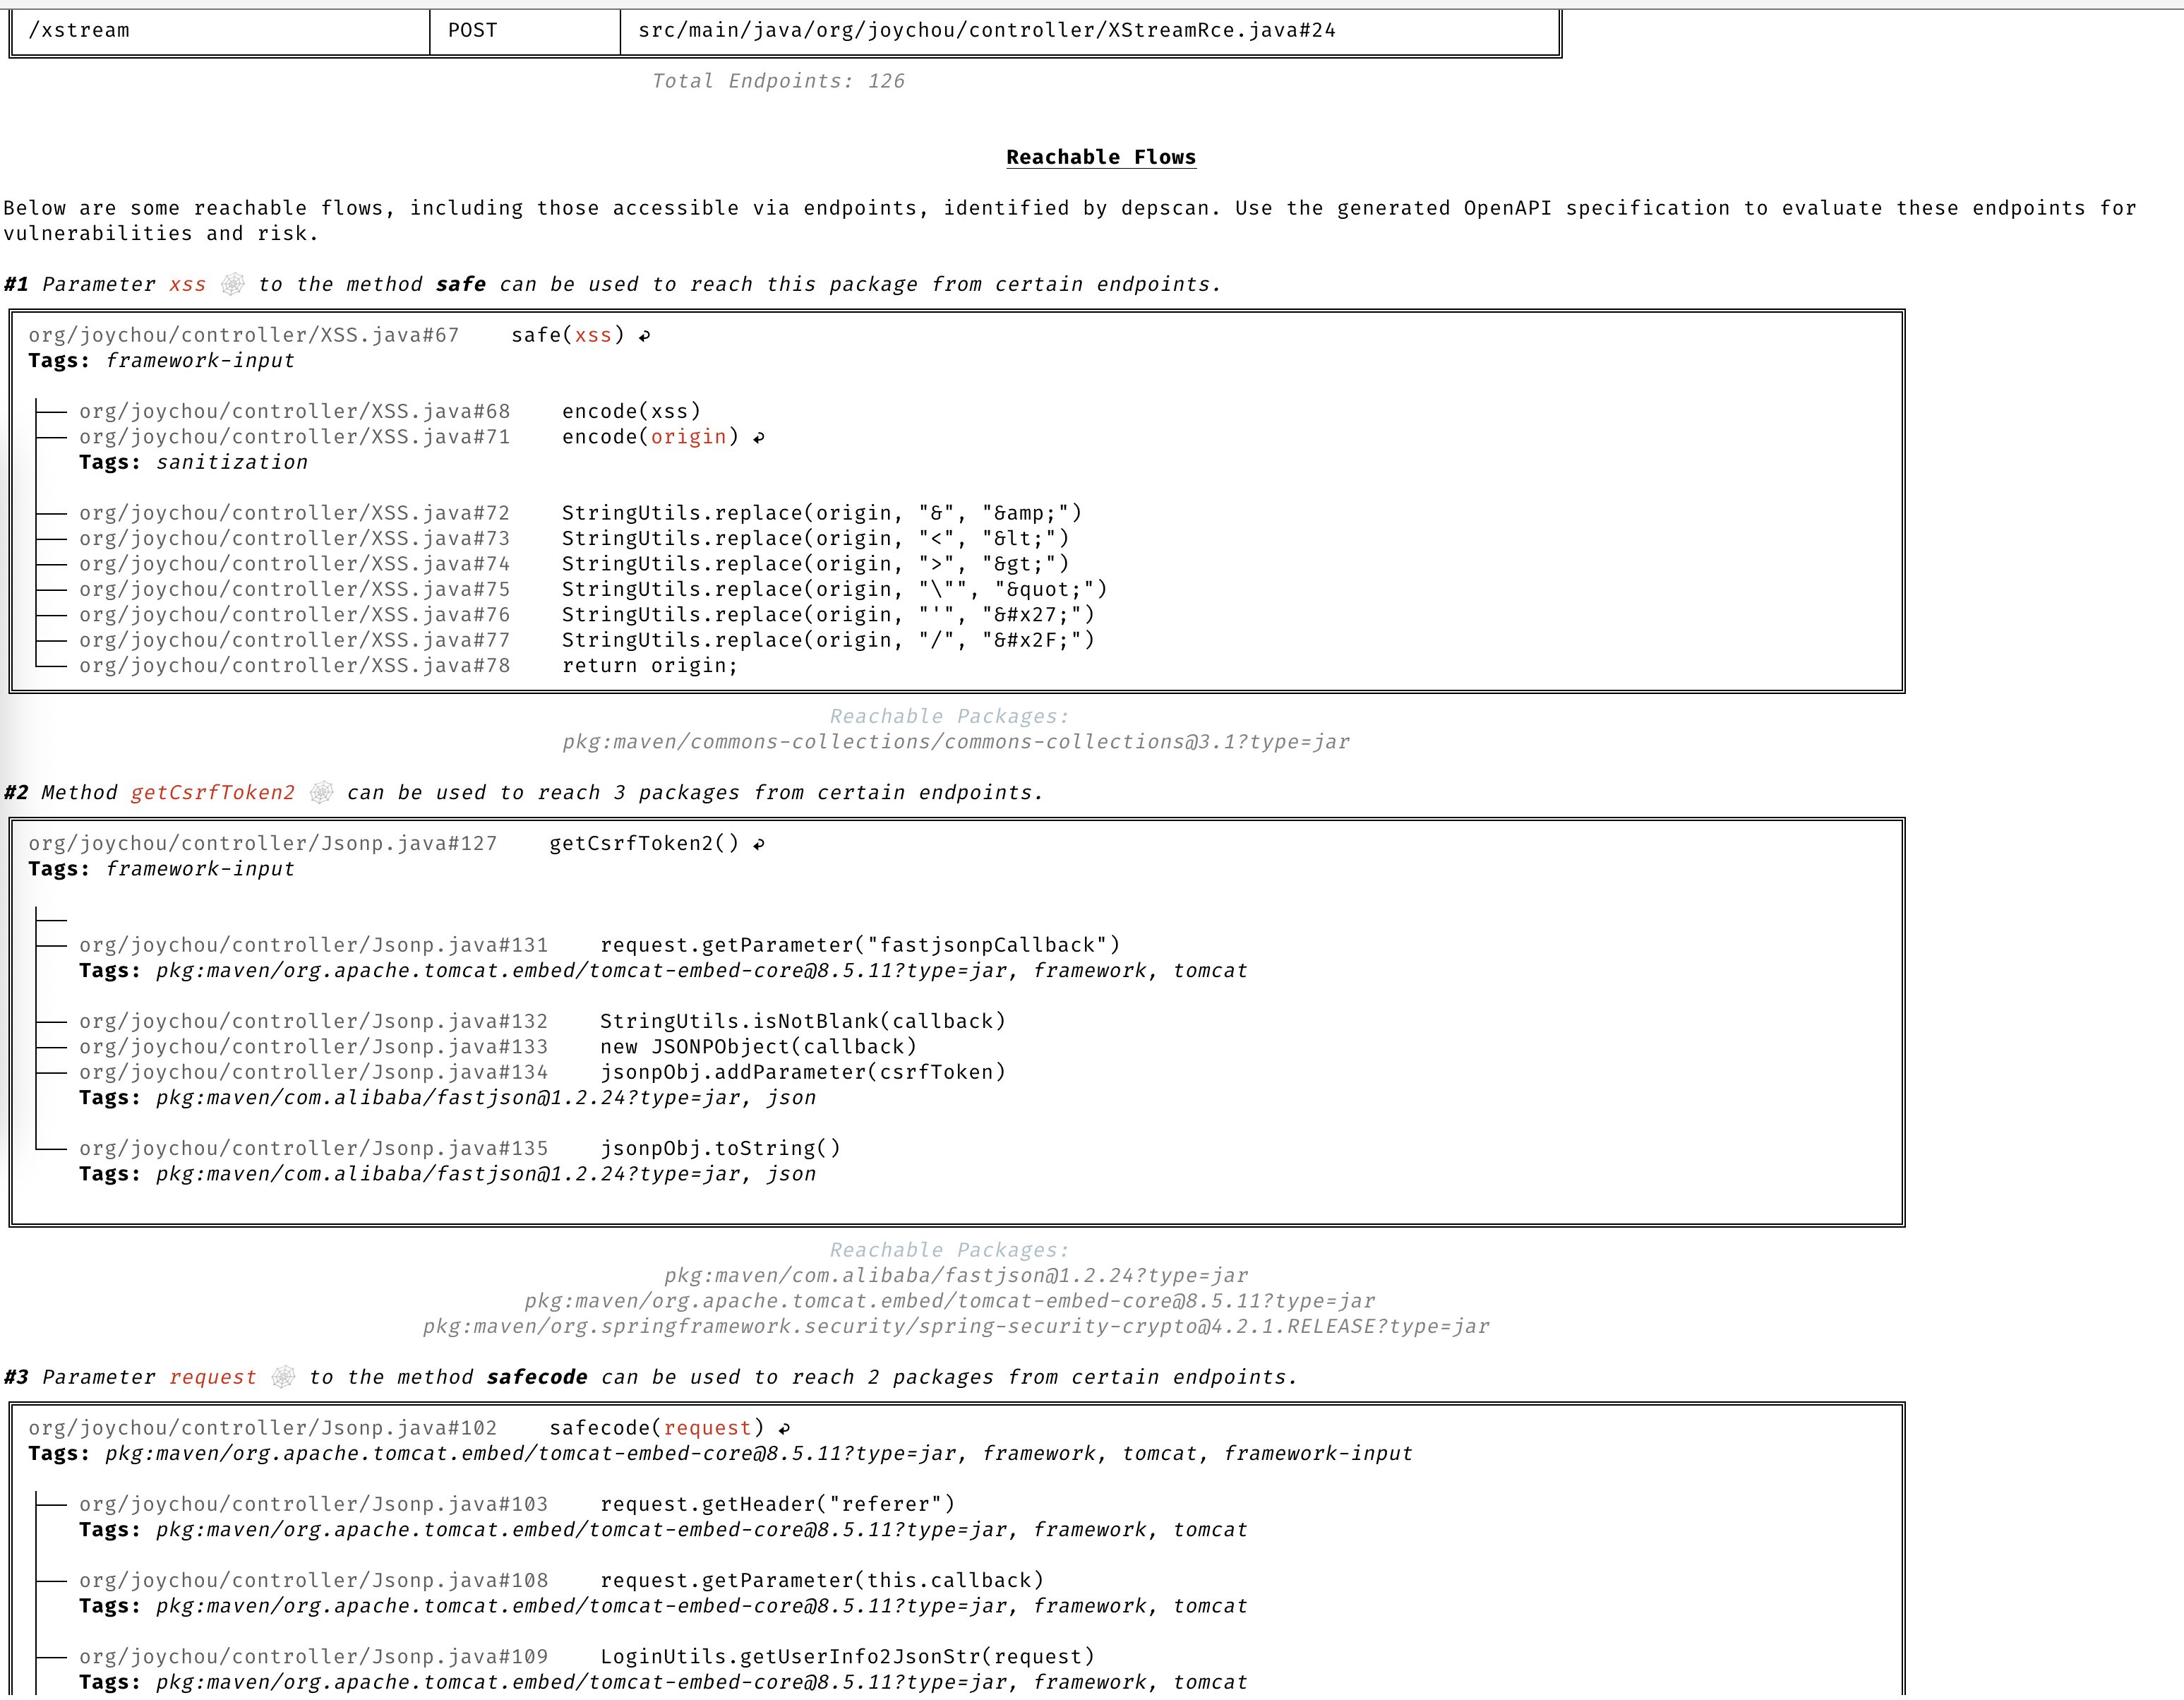
Precise Reachable data-flows
Detailed data flows to identify both reachable and non-reachable paths in your application based on the full context.
!Reachable Flows
Reachability matrix
dep-scan computes reachability for se ecosystems through four slicers. A package whose code is actually on an executed path is marked Reachable, while a package that is merely declared in the BOM but ne is not. Every slicer feeds the same shared, purl-keyed reachability engine, so the behavior is uniform across languages. Reachability is on by default (--reachability-analyzer FrameworkReachability); SemanticReachability additionally attributes reached services, endpoints, and post-build (binary/container) reachability.
| Language / ecosystem | Reachability engine | Default analyzer |
| ---------------------------------- | ----------------------------------------------------- | ----------------------- |
| Java / J, Kotlin, Scala) | atom | FrameworkReachability |
| Ja / TypeScript | atom | FrameworkReachability |
| Python | atom | FrameworkReachability |
| PHP | atom | FrameworkReachability |
| Rust | rusi | FrameworkReachability |
| Go | golem | FrameworkReachability |
| .NET (C#, VB, F#, R) | dosai | FrameworkReachability |
For the concepts behind reachability and prioritization, read the reachability model and prioritization chapters. For per-language worked examples, see the Language Guides. For the compliance story (VDR and CSAF VEX), see the and the CSAF .
Reachability is on by default under --profile research, which is what dep-scan uses when reachability is on. The commands below are enough to get started; the per-language guides co resolution, backend and network safety, restore requirements, and worked examples on the in-repo fixtures.
Rust (rusi). cdxgen runs rusi and persists its report, which dep-scan converts into the shared pipeline, so a crate that is actually called (for example time::now() for RUSTSEC-2020-0071) is Reachable while one merely present is not. See the Rust reachability guide.
Go (golem). dep-scan invokes golem directly for Go projects (needs go on PATH), marking a module Reachable when its functions are on a traced path. Use --go-analyzer-network offline for untrusted repos with a warm module cache. See the Go reachability guide.
.NET (dosai). cdxgen runs dosai, which emits an explicit per-package reachability (PackageReachability with ReachabilityKind and Confidence) that dep-scan treats as authoritative, so a NuGet package actually called (for example JsonConvert.DeserializeObject on a controlled input) is Reachable. Scan a restored tree for purls. See the .NET reachability guide.
J/TypeScript, Python, and PHP (atom). These four ecosystems share the atom slicer, which builds a language-agnostic intermediate representation and performs static slicing. See the JVM, JS, Python, and PHP reachability guide.
To mo framework-forward reachability to endpoint, service, and post-build tiers, pass --reachability-analyzer SemanticReachability with a --bom-dir of lifecycle BOMs. See the semantic reachability guide.
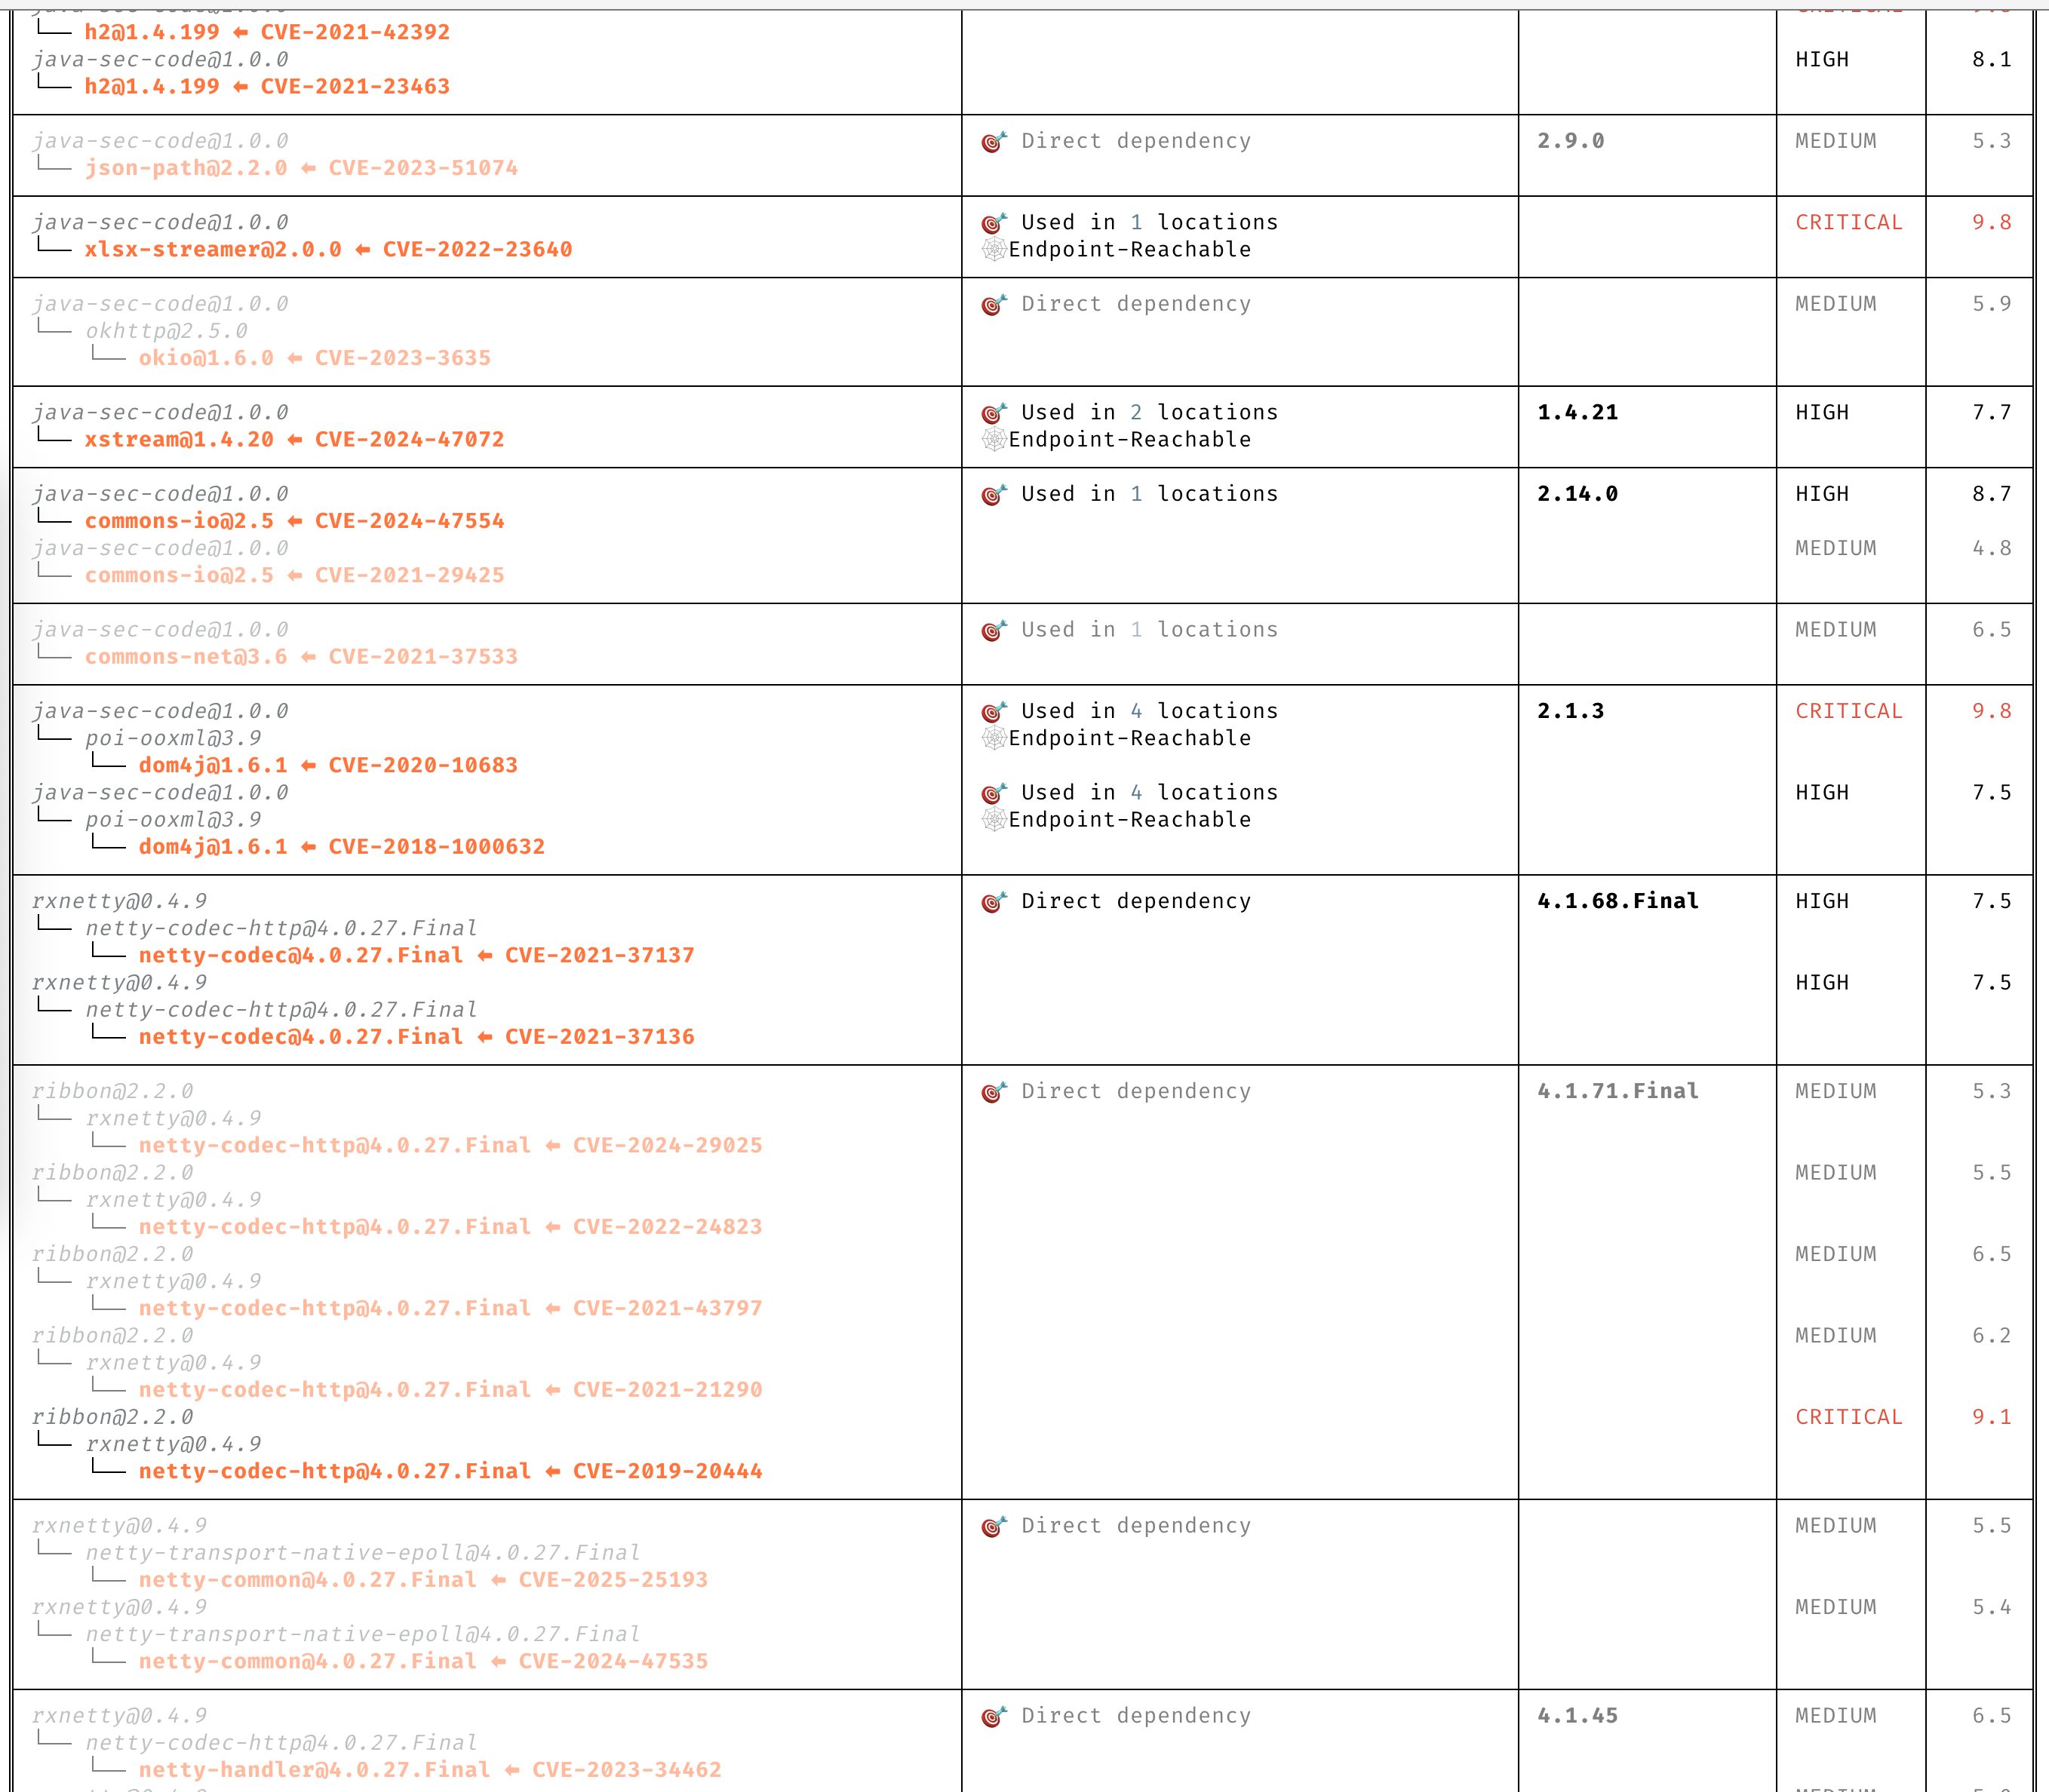
Clear insights about CVEs
Understand C without having to read through the description.
!Dependency Tree with Insights
Automatic prioritization
Only focus on CVEs that need your attention.
!Prioritization
Stay proactive
Always stay a step ahead with ad and exploit prediction.
!Proacti
Data sources
Linux distros
Quick Start
dep-scan is ideal for use during continuous integration (CI) and as a local de tool.
Scanning projects locally (Python )
This would install two commands called cdxgen and depscan.
You can invoke the scan command directly with the options.
The full list of options is below:
Standalone binaries (no Python or Node.js required)
Pre-built single-file executables are attached to each GitHub release. They bundle a matching cdxgen SEA binary, so BOM generation works out of the box without installing Python, Node.js, or cdxgen.
| Platform | Architecture | Asset |
| --------------------- | ------------- | --------------------------- |
| Linux (glibc) | x86_64 | depscan-linux-amd64 |
| Linux (glibc) | arm64 | depscan-linux-arm64 |
| Linux (musl / Alpine) | x86_64 | depscan-linux-amd64-musl |
| Linux (musl / Alpine) | arm64 | depscan-linux-arm64-musl |
| macOS | Apple silicon | depscan-darwin-arm64 |
| macOS | Intel | depscan-darwin-amd64 |
| Windows | x86_64 | depscan-windows-amd64.exe |
Each asset has a matching .sha256 file for .
> [!NOTE]
> The macOS binaries are currently unsigned. On first run macOS Gatekeeper may block them; clear the quarantine attribute with xattr -d com.apple.quarantine ./depscan-darwin-arm64 (or allow the binary under System Settings, Privacy & Security).
> [!NOTE]
> The database is still downloaded on first run. Only cdxgen is bundled, not the vuln DB. Use the depscan-vdb command to select a specific database , for example depscan- --scope app for a smaller app-only database. See the database guide for the full image matrix.
All standalone binaries bundle blint, but not its optional nyxstone disassembly backend (which has no wheels and no Windows support). Deep disassembly-based binary analysis is therefore una in the standalone binaries; use the Python package (pip install owasp-depscan[all]) if you need it.
Scanning containers locally (Python )
Scan a Ja.
Scan latest tag of the container shiftleft/scan-slim
Include license to the type to perform the license audit.
You can also specify the image using the sha256 digest
You can also sa images using docker or podman sa and pass the archive to depscan for scanning.
Refer to the docker tests under the GitHub action workflow for this repo for more examples.
Scanning projects locally (Docker container)
ghcr.io/owasp-dep-scan/dep-scan container image can be used to perform the scan.
To scan with default settings
To scan with custom en based configuration
In the abo, /tmp is mounted as /db into the container. This directory is then specified as for caching the information. This way the database can be cached and reused to impro.
Server mode
dep-scan and cdxgen could be run in server mode. Use the included docker-compose file to get started.
The bundled compose file sets DEPSCAN_SER to a de placeholder by default so the dep-scan service can bind to 0.0.0.0. O this value before exposing the service outside a local lab.
If you need to bind dep-scan to a non-local address, set an API key first:
> [!IMPORTANT]
> dep-scan refuses to bind to a non-local address without either DEPSCAN_SER or an explicit opt-in via DEPSCAN_SERD_BIND=true.
Use the /scan endpoint to perform scans.
> [!NOTE]
> The type parameter is mandatory in server mode. When API key authentication is enabled, send the key using X-API-Key or Authorization: Bearer <key>.
Scanning an SBOM file (present locally).
Local de
Setup uv by following the official documentation.
Local
Scan local depscan
This would automatically use the configuration specified in the local config file.
Documentation
Full documentation is at depscan.readthedocs.io. Key pages:
- The reachability model
- How dep-scan prioritizes
- SBOM and e
- Language guides: Rust, Go, .NET, JVM/JS/Python/PHP
- Analyzers: Framework reachability, Semantic reachability
License
MIT License
This project was donated to the OWASP Foundation in August 2023 by AppThreat Ltd.
Funding
This project is funded through NGI Zero Core, a fund established by NLnet with financial support from the European Commission's Next Generation Internet program. Learn more at the NLnet project page.
<img src=" alt="NLnet foundation logo" width="20%" />
<img src=" alt="NGI Zero Logo" width="20%" />
项目信息
开发语言:Python
Star 数:1295
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕OWASP dep-scan is a next-generation security and risk audit tool based on known vulnerabilities, advisories, and license limitations for project dependencies. Both local repositories and container images are supported as the input, and the tool is ideal for integration.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | dep-scan - OWASP dep-scan is a next-generation security and r |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:01:48 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 309 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |