 漏洞知识库
点击放大
nuclei-wordfence-cve - 80k+ WordPress Nuclei templates, updated daily fro
项目说明
<di="center">
<a href="
<img width="100" align=center src="
</a>
<h1>Nuclei + Wordfence = ♥</h1>
<h4><!-- START: __TOTAL_NUM_TEMPLATES -->84,997<!-- END: __TOTAL_NUM_TEMPLATES --> Nuclei Templates for WordPress Security Scanning 🥳</h4>
<img src=" height="20" alt="GitHub Workflow Status">
<img src=" height="20" alt="pre-commit">
<img src=" height="20" alt="Templates added">
</div>
<di="center">
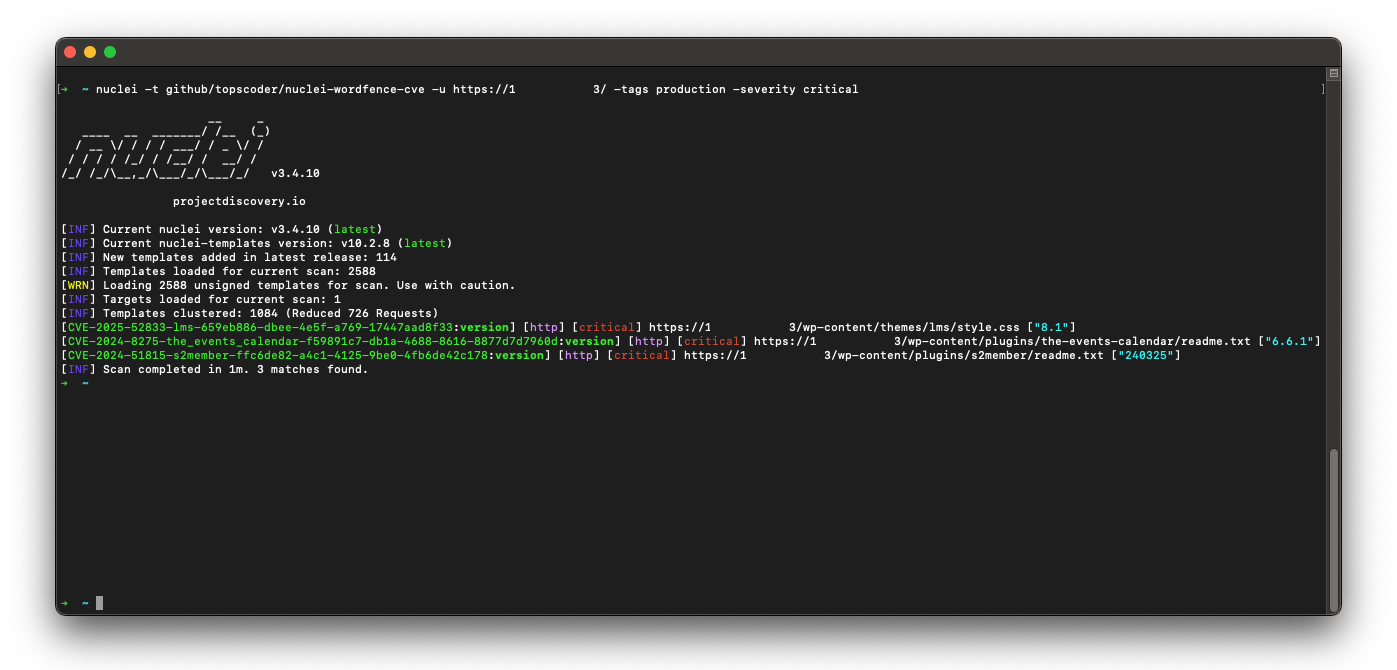
<img src=".github/screenshot.png" alt="Project Demo" width="1000">
</div>
---
Level up your WordPress security game! This project's got a treasure trove of fresh Nuclei templates for WordPress. Scan for weaknesses in Core, plugins, and themes – all based on the latest intel from Wordfence.com.
Here's why this is your new best friend:
* Massi: No more hunting for indi templates, you've got a whole arsenal at your fingertips.
* Always on point: These templates stay updated with the freshest threats, so you're ne the curve.
* Open source magic: Need to tweak a template for a specific situation? No problem, you've got full control.
If you're guarding a WordPress site, this project is your secret weapon to identify before the bad guys do. Stop wasting time and secure your sites like a pro!
---
> [!TIP]
> If you found this project helpful, please consider buying me a coffee.<br>
> <br>
> ![Buy Me A Coffee]()
✨ What's in it?!
<!-- START: __STATISTICS_TABLE -->
<table width="100%">
<tr>
<td width="50%" ="top">
<table>
<thead>
<tr><th align="left">category</th><th align="left">total</th></tr>
</thead>
<tbody>
<tr><td>wp-plugins</td><td><a href="
<tr><td>wp-themes</td><td><a href="
<tr><td>wp-core</td><td><a href="
<tr><td>other</td><td><a href="
</tbody>
</table>
</td>
<td width="50%" ="top">
<table>
<thead>
<tr><th align="left">se</th><th align="left">total</th></tr>
</thead>
<tbody>
<tr><td>critical</td><td><a href="
<tr><td>high</td><td><a href="
<tr><td>medium</td><td><a href="
<tr><td>low</td><td><a href="
<tr><td>info</td><td><a href="
</tbody>
</table>
</td>
</tr>
</table>
<!-- END: __STATISTICS_TABLE -->
🚀 Quick Start
To install this nuclei-wordfence-cve repository for use with Nuclei, you can use the following commands:
Once you ha this template repo using the commands above, you can run the following command to scan for using Nuclei:
Wordfence provides two separate feeds for . The first feed includes only production , each with an assigned CVE. The second feed contains candidate , which do not yet have a C and may or may not be promoted to the production feed. To differentiate templates generated from these feeds, a tag is assigned to each template—either production or candidate—allowing you to target them using a tag filter.
_Include only production templates:_
_Include only candidate templates:_
💻 Examples
Here are some examples how to use the templates:
* To scan for all known in WordPress, you can run the following command:
* To scan for a C , you can run the following command:
* To scan only for critical , you can run the following command:
* To scan only for WordPress core , you can run the following command:
* To scan only for WordPress plugin , you can run the following command:
* To scan only for WordPress theme , you can run the following command:
* To go wild, you can combine and combine and combine:
* To go e, you can use the template condition flag (-tc) that allows complex expressions like the following ones:
🤖 Se recalculation
Template se is adjusted by the parser to better reflect real-world impact. The determine_se function in src/lib/wordfence_api_parser.py inspects the title and description and will downscale issues that are limited to authenticated users (e.g., require login or elevated roles).
Example (simplified):
authenticated (and not unauthenticated), the function treats the issue as lower risk and returns Low instead of a higher C.This helps avoid assigning Medium/High se to that only affect logged-in users, which reduces noise when scanning publicly accessible sites.
👥 Contributing
If you would like to contribute to this project, please feel free to fork the repository and submit a pull request.
📚 License
This project is licensed under the MIT License.
> [!NOTE]
> ~~ Please use it responsibly!
项目信息
开发语言:Python
Star 数:1292
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | nuclei-wordfence-cve - 80k+ WordPress Nuclei templates, updated daily fro |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:01:51 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 331 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |