 漏洞知识库
点击放大
android-vts - Android Vulnerability Test Suite - In the spirit o
项目说明
#Android Test Suite
Download from Github
UPDATE 2015/12/15: AndroidVTS is currently not a in the Google Play™ store app, more info here.
O
This tool was meant to show the end user the attack surface that a gi is susceptible to. In implementing these checks we attempt to minimize or eliminate both false positi negati negatively affecting system stability.
Rationale for necessity
When a is discovered, Google receives word and applies a patch to Android. The Nexus devices are usually the devices that recei patches quickest as they deviate the least (read: not at all) from AOSP (Android Open Source Project - The core of Android, where Google commits to). The lag time between learning about a bug and the time when a patch is applied to a device can still be significant (for OEMs, it can be > 1 year or never). For example, the futex bug (C/Towelroot) was known about in late May, early June. This bug took multiple months to get patched on the flagship (at the time) Nexus 5. This lea extremely to attack from applications. Users mostly do not know that their devices are and this tool is meant to gi into the a gi is susceptible to.
Lifecycle of a patch
Samsung, HTC, and every other OEM keep heavily customized of Android. The patch deployment infrastructure from OEMS -> carriers -> users is in disarray. The OEMs receive the patches from Google and spend weeks or months applying these to some devices and testing. Then they ship off the device updates to the carrier who is responsible for pushing them to the end user. They then go through another QA cycle from the carrier.
Implementation
in a device can exist at many layers inside of Android. For example, a bug can exist in the kernel (Towelroot, for example) or it can exist in the Android specific framework (Android Masterkeys/FakeID). Some of the kernel bugs can sometimes be difficult to check for without potentially causing system instability. This implementation takes care to not include checks that could cause instability problems for the end user and therefore may omit checks that could cause these types of issues. The framework is very thin at the current time and consists of a of checks. Their concrete implementations vary wildly depending on the bug.
A list of current bug checks:
- ZipBug9950697
- Zip Bug 8219321 / Master keys
- Zip Bug 9695860
- Jar Bug 13678484 / Android FakeID
- C / put/get_user
- C / PSNueter / Ashmem Exploit
- [C / Futex bug / Towelroot] ()
- C / WeakSauce
- StumpRoot
- Stagefright bugs
- [x509 Serialization bug] ()
- [PingPong root - C] ()
- Stagefright - C
- [Samsung Remote Code Execution as System] ()
- C
- C
- C
- C
Previous work
There have been attempts before to solve this issue. xray.io Xray works by actually attempting the exploit which doesn't satisfy our system stability constraint. There also exist other applications which attempt to determine a devices attack surface by simply using a lookup based on Android /build information. This causes both false negatives and false positives. Imagine the case where an OEM has back ported a fix to a device, but the check solely relies on an Android device; false positive. The case where an OEM upgrades to an Android /kernel which includes patches, but manages to break them causes the case of a false negative.
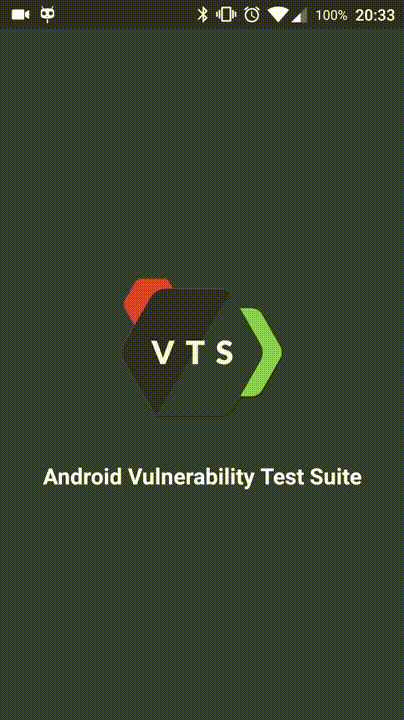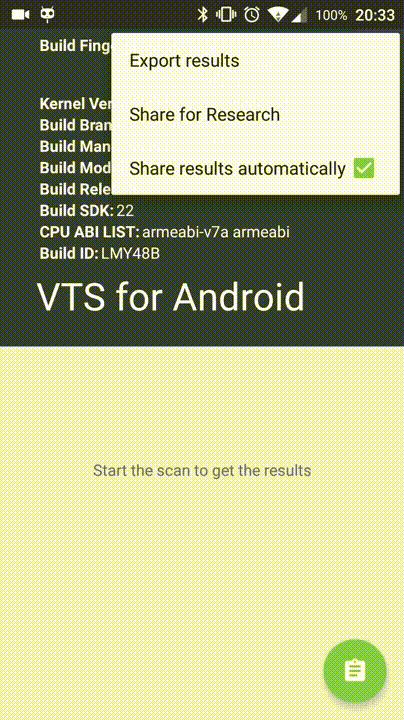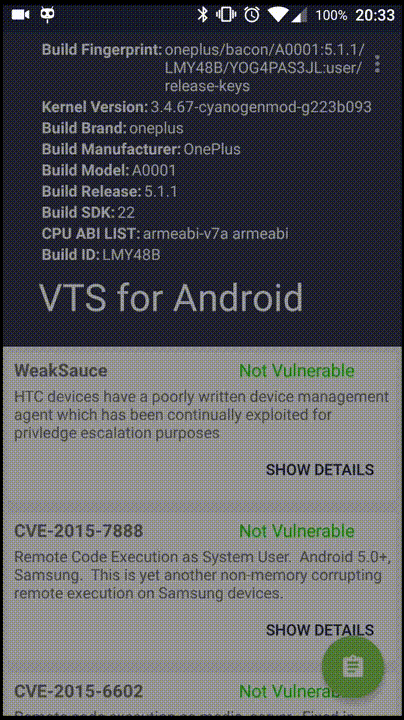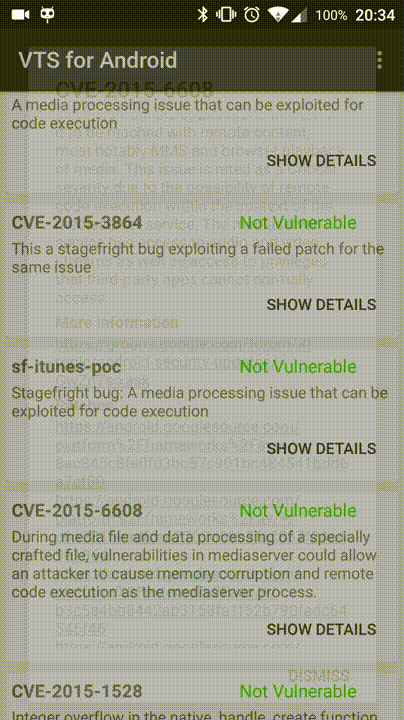
!Device Screencast
Contributions
See CONTRIBUTING.md
Building
You can import this project into AndroidStudio or use gradle from the CLI. You need the Android SDK and NDK installed to properly build this project.
The gradle build files look for a local.properties:
cat local.properties
To build a debug APK with test signing keys:
Build and install a debug build:
Build a release (unsigned):
```
./gradlew assembleRelease
项目信息
开发语言:Java
Star 数:1039
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Android Vulnerability Test Suite - In the spirit of open data collection, and with the help of the community, let's take a pulse on the state of Android security. NowSecure presents an on-device app to test for recent device vulnerabilities.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | android-vts - Android Vulnerability Test Suite - In the spirit o |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:03:32 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 113 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |