 漏洞知识库
点击放大
Damn-Vulnerable-RESTaurant-API-Game - Damn Vulnerable Restaurant is an intentionally vul
项目说明
*For theoretical materials, quizzes, descriptions, walkthroughs with practical challenges, I recommend my project API Security Champion.*
---
!Damn RESTaurant Logo
An intentionally API service designed for learning and training purposes dedicated to de, ethical hackers and security engineers. The idea of the project is to provide an en that can be easily extended with new endpoints and mechanisms that could be used in trainings for detecting and exploiting identified .
It's a training playground:
* For De - engage in a dedicated game where you will identify and fix interactively.
* For Ethical Hackers - exploit manually or use automated tools. Treat it as a CTF challenge, you can start from low pri API user and escalate to root user. There is one path to achieve this. API docs are provided to facilitate your hacking ad.
* For Security Engineers - utilise security automation tools such as SAST, DAST, IaC, etc., to test detection mechanisms.
🏆 Hall of Fame
Participants who were able to complete this challenge are listed in Hall of Fame. Submit your solution and become one of them!
*Solutions and walkthroughs published before 14.11.2024 may refer to the a in the linked commit.*
🚀 Starting the Game
The application can be launched locally in two alternative ways: De can play an interactive game where they will in and fix , or Ethical Hackers can identify and exploit . Furthermore, GitHub Codespaces can be used to run the application easily without a local en! GitHub Codespaces offers up to 60 hours a month for free.
The following sections present how to start the game.
👨💻 De Approach
For de, I created a dedicated game where you can identify and fix in FastAPI based app in an interactive way.
1. Install Docker and Docker Compose V2.
2. Start the game by executing the following commands:
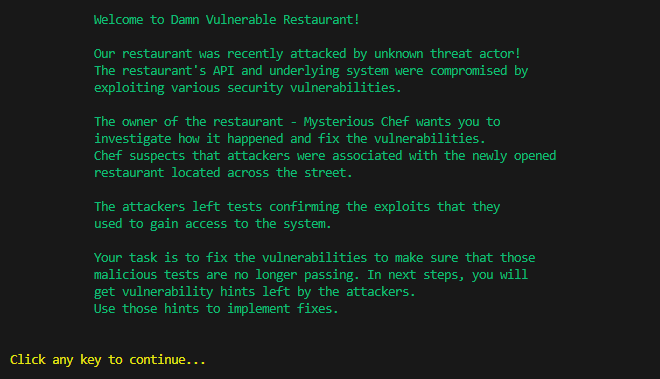
3. You should observe the following screen:
!The Game Entry Screen
4. You can implement the fixes without needing to restart the Docker instance. Since changes to models are not required, there should be no need for restarts related to migrations.
At this point, the application is running locally. You can take a look at step 3 in next section for more details about accessing the API and documentation.
👾 Ethical Hackers Approach
You can open RESTaurant easily just with a few steps, you don't need to have a large budget, rented place, cooks or waitress...
You just need to find a Chef and follow the steps:
1. Install Docker and Docker Compose V2.
2. Deploy RESTaurant locally with Docker by executing the following commands:
3. The API service will be exposed at by default. API documentation can be found at the following endpoints:
* Swagger -
* Redoc -
4. To close the restaurant at the end of the hacking day, just run:
Data will persist between stops and starts.
You're ready to serve the dishes now, make the Chef mad by exploiting vulns or make the Chef happy by fixing them!
☁️ Launch in Github Codespaces
To launch the game in GitHub Codespaces, follow the steps:
1. Click on:
![Damn RESTaurant Logo]()
2. To create a codespace, click the Code green drop down button in the upper-right of your repository na bar.
3. Click the Create codespace on main.
4. After creating a codespace, you can execute ./start_game.sh or ./start_app.sh respectively in the terminal and follow instructions presented in previous sections.
5. The application can be accessed via a dedicated link. Example codespace en is shown below (take a look at web app URL scheme):
!Damn RESTaurant Logo
📖 Learning Resources
Based on the Damn RESTaurant, I created a Web API Security Champion series about OWASP Top 10 API Security Risks presenting each in a practical manner with exploitation steps, remedial and pre actions. Enjoy!
🛠️ De Stack
It is de with Python FastAPI framework and uses PostgreSQL database. The en is containerised and can be easily deployed locally with Docker. With Python and FastAPI it's rather simple to extend the application with new features in a short amount of time.
Damn RESTaurant is not actually limited to any specific type of API, as endpoints may utilize REST API, GraphQL, and others. It's a restaurant, so dishes might be ser over a time!
🗺️ Roadmap
There are several ideas for improving the project such as:
🤝 De / Contribution
Damn RESTaurant was de with having flexibility in mind. It can be extended with new security issues by following CONTRIBUTING.md.
⚠️ Warning and Disclaimer!
Damn RESTaurant is damn ! Do not ser from this RESTaurant on a public streets... ekhm... networks!
Do not upload it to your hosting provider's public html folder or any Internet facing servers, as they will be compromised. It is recommended to deploy RESTaurant locally with Docker.
The usage of the Damn RESTaurant application, which is intentionally insecure by design, is at your own risk. We do not assume any responsibility for any potential harm, damage, or security breaches that may arise from using RESTaurant. This application is specifically created for educational and training purposes within controlled en, such as learning about and practicing ethical hacking techniques. It is RESTaurant to use RESTaurant responsibly and exclusively in en that you have the right to access and modify. By using RESTaurant, you acknowledge that any unintended usage or consequences are your sole responsibility, and we disclaim liability for any such actions.
🧾 License
Damn RESTaurant is proudly de under the terms of the GNU General Public License 3.0 (GNU GPL v3.0). This license empowers the open-source community by promoting the principles of software freedom, collaboration, and transparency. With GNU GPL v3.0, RESTaurant encourages learning, sharing, and contributions from ethical hackers, security engineers, and de to collectively enhance their skills and understanding of security . Please review the LICENSE file for a detailed o of the rights and responsibilities associated with using and contributing to this project.
项目信息
开发语言:Python
Star 数:939
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Damn Vulnerable Restaurant is an intentionally vulnerable Web API game for learning and training purposes dedicated to developers, ethical hackers and security engineers.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Damn-Vulnerable-RESTaurant-API-Game - Damn Vulnerable Restaurant is an intentionally vul |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:04:29 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 366 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |