 漏洞知识库
点击放大
ApacheTomcatScanner - A python script to scan for Apache Tomcat server v
项目说明

<p align="center">
A python script to scan for Apache Tomcat ser.
<br>
<img alt="PyPI" src="
<img alt="GitHub release (latest by date)" src="
<img alt="Python pip build" src="
<a href=" title="Follow"><img src="
<a href=" title="Subscribe"><img alt="YouTube Channel Subscribers" src="
<br>
</p>
Features
- [x] Multithreaded workers to search for Apache tomcat servers.
- [x] Multiple target sources accepted:
+ [x] Retrieving list of computers from a Windows domain through an LDAP query to use them as a list of targets.
+ [x] Reading targets line by line from a file.
+ [x] Reading indi targets (IP/DNS/CIDR) from -tt/--target option.
+ [x] Reading indi targets URLs from -tu/--target-url option.
- [x] Custom list of ports to test.
- [x] Tests for /manager/html accessibility.
- [x] Tests for default credentials to access the Tomcat Manager.
- [x] List the CVEs of each with the --list-cves option, print detailed C with --show-c
Installation
You can now install it from PyPI (latest is <img alt="PyPI" src=") with this command:
Usage
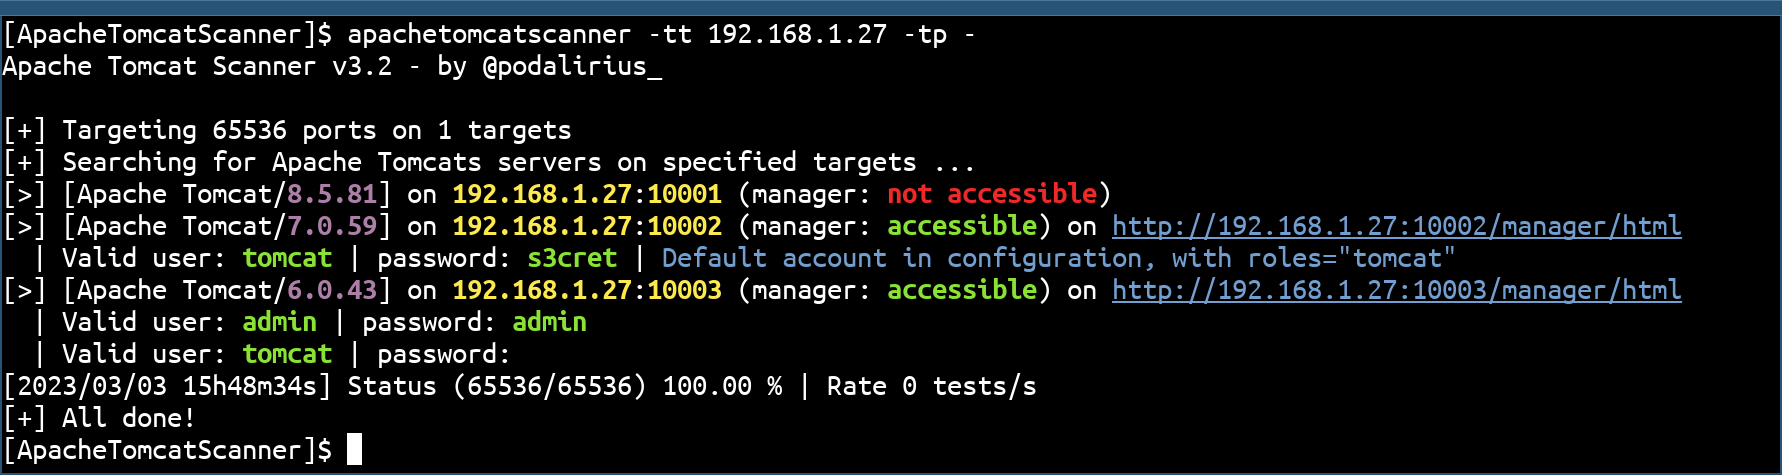
Example

You can also list the CVEs of each with the --list-cves option:

C Auto-Update
The scanner includes an automatic C update check to ensure you always have the latest data.
How It Works
When you run the scanner, it automatically checks if the C is older than 30 days. If outdated, you'll see:
Type y to update immediately, or press Enter to skip and continue scanning.
Disable Auto-Update Check
To skip the update check entirely, use the --no-auto-update flag:
Manual Database Update
You can manually update the C anytime:
Note: Updates use the official NVD API with rate limiting (5 requests per 30 seconds). The process may take several minutes but can be interrupted and resumed anytime. Consider getting a free NVD API key for faster updates:
Contributing
Pull requests are welcome. Feel free to open an issue if you want to add other features.
项目信息
开发语言:Python
Star 数:891
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A python script to scan for Apache Tomcat server vulnerabilities. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ApacheTomcatScanner - A python script to scan for Apache Tomcat server v |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:04:56 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 193 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |