 漏洞知识库
点击放大
Java-Deserialization-Scanner - All-in-one plugin for Burp Suite for the detection
项目说明
Ja Scanner
Ja Scanner is a Burp Suite plugin aimed at detect and exploit Ja . It was written by Federico Dotta, Principal Security Analyst at HN Security.
The plugin is made up of three different components:
1. Integration with Burp Suite active and passi
2. Manual tester, for the detection of Ja on custom insertion points
3. Exploiter, that allow to actively exploit Ja , using frohoff ysoserial ()
Author
Contributors
Mini walkthrough (24/05/17)
A brief article containing a mini walkthrough on how to use the components of the plugin can be found at the following URL:
Integration with Burp Suite active and passi
Ja Scanner uses custom payloads generated with a modified of "ysoserial", tool created by frohoff and gebl, to detect Ja . The original tool () generate payloads for the execution of commands on the system, using the Runtime.exec function. Usually, however, it is not possible to see the output of the command and consequently it is not simple to write a scanner based on this kind of function. For this reason, a modified of ysoserial is used to generate different types of payloads, usefull for the detection of the issue instead of the exploitation:
1. Payloads that execute a syncronous sleep function, in order to the presence of the issue depending on the time of the response
2. Payloads that execute a DNS resolution, in order to the presence of the issue using the Burp Suite Collaborator integrated in Burp Suite
Currently, the passi of the Ja Scanner reported the presence of serialized Ja in the HTTP requests and the acti actively scan for the presence of weak deserialization functions in conjuction with the presence of the following weak libraries:
1. Apache Commons Collections 3 (up to 3.2.1), with fi chains
2. Apache Commons Collections 4 (up to 4.4.0), with two different chains
3. Spring (up to 4.2.2), with two different chains
4. Java 6 and Java 7 (up to Jdk7u21) without any weak library
5. Hibernate 5
6. JSON
7. Rome
8. Java 8 (up to Jdk8u20) without any weak library
9. Apache Commons BeanUtils
10. Ja/Weld
11. JBoss Interceptors
12. Mozilla Rhino (two different chains)
13.
Furthermore, URLSNDS payload has been introduced to actively detect Ja without any libraris. If the plugin find only the URLDNS issue (and no libraries), the attacker probably can execute DoS attacks but to achie Code Execution it is necessary more effort. Refer to this link for more details.
All the components of the plugin supports the following encodings:
1. Raw
2. Base64
3. Ascii Hex
4. GZIP
5. Base64 GZIP
In the test folder there are some simple Ja applications that can be used to test the plugin. Every application employ a different Ja.
Manual tester
The plugin offer a dedicated tab to launch the detection with the sleep and DNS payloads on custom insertion points, in order to check the Ja in particular situations in which strange entry points do not allow the detection with the scanner. The results of the manual tester can be inserted between Burp Suite scanner results.
The manual tester offers an extra detection method: CPU detection. The CPU detection method is based on Wouter Coekaerts’ SerialDOS work () and it is able to detect deserialization issues without the presence of any library, using an object that employs many CPU cycles for the deserialization task and checking the time of the response. The CPU detection method is not included by default in the active scan checks, because it must be used with caution: sending a huge number of “light” SerialDOS payloads may still cause problems on old or highly-loaded systems.
Exploiter
After that a Ja has been found, it is possible to actively exploit the issue with the Exploiting dedicated tab. The “Exploiting” tab offers a comfortable interface to exploit deserialization . This tab uses the ysoserial tool to generate exploitation and includes the generated payload in a HTTP request. ysoserial takes as argument a library and a command and generates a serialized object in binary form that can be sent to the application to execute the command on the target system (ob if the target application is ). The Exploiting tab supports the same encoding formats as the detection sections of the plugin.
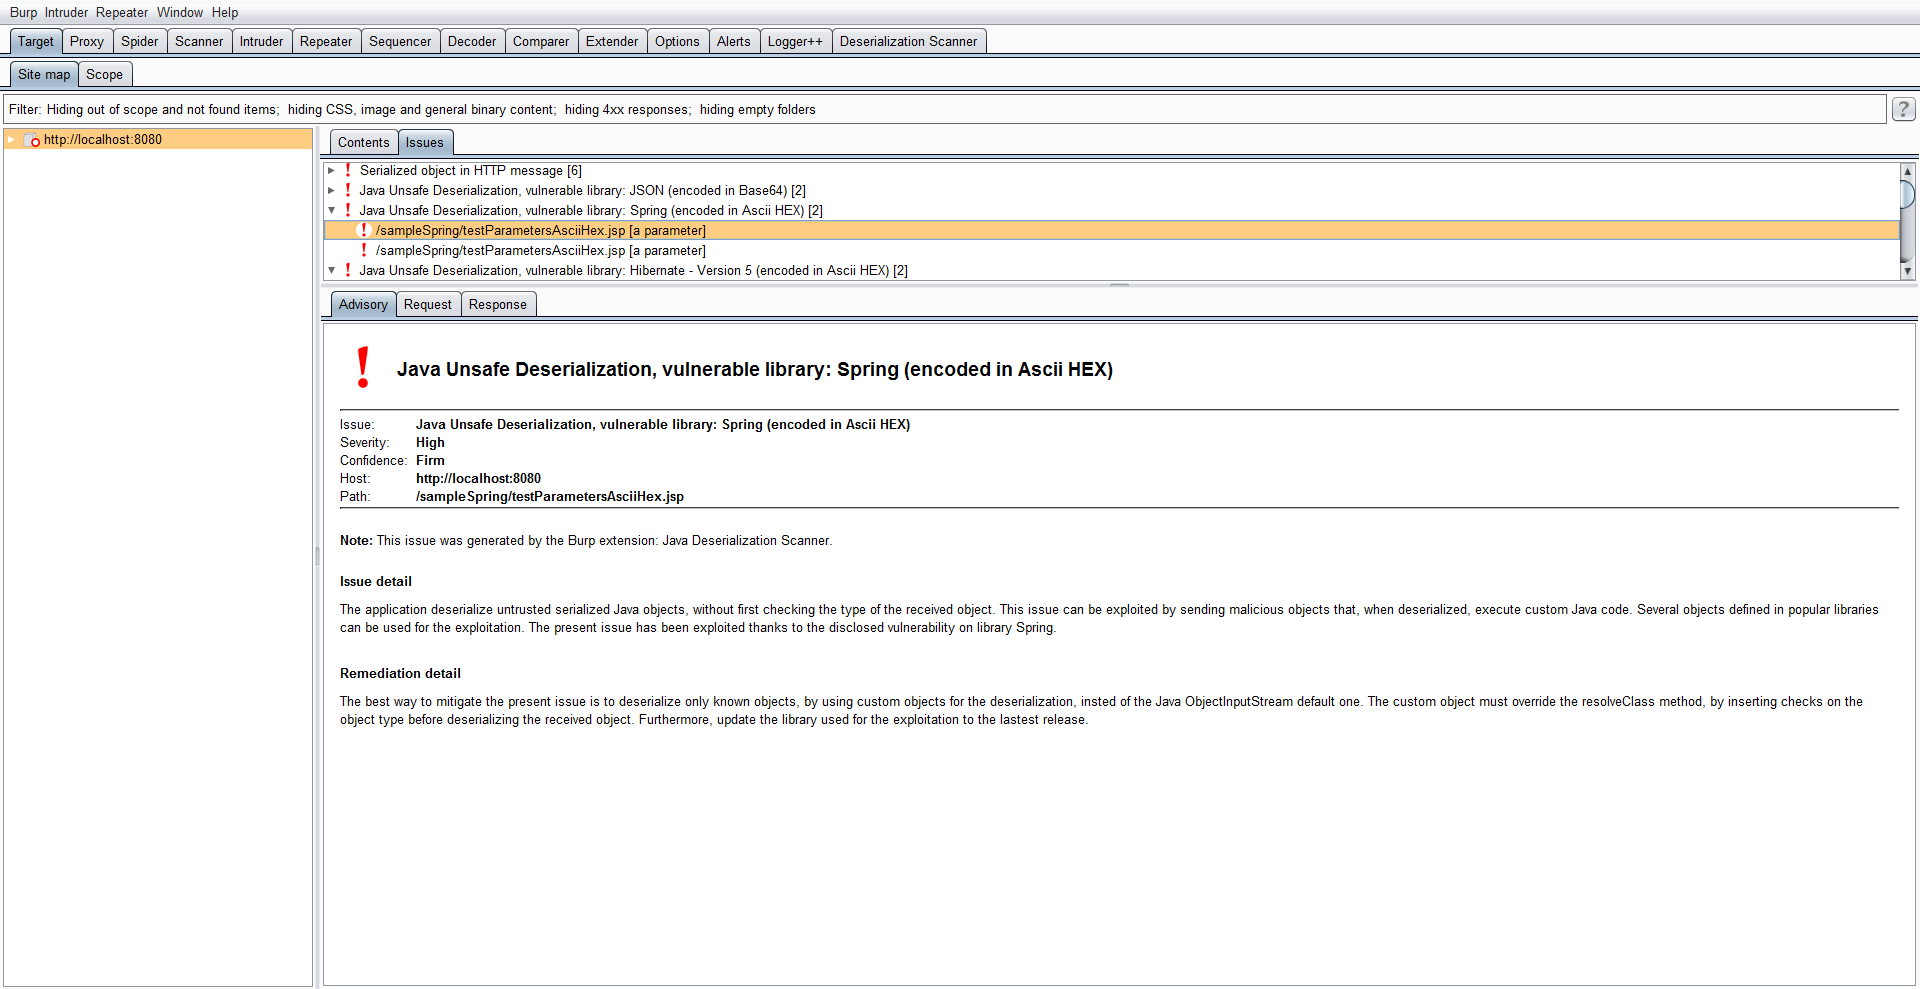
Screenshot
!alt tag
Installation
1. Download Burp Suite:
2. Install Ja Scanner from the BApp Store or follow these steps:
3. Download the last release of Ja Scanner
4. Open Burp -> Extender -> Extensions -> Add -> Choose JaXX.jar file
User Guide
1. After installation, the Ja Scanner active and passi will be added to the Burp Suite scanner (it is possible to disable the checks in the options tab)
2. Simply run the active or passi in order to check also for weak Ja
3. With the dedicated tab "Manual testing" it is possible to set the injection point and executing the attack with all the payloads
4. With the dedicated tab "Exploiting" it is possibile to actively exploit Ja
5. The "Configuration" contains all the needed configuration for the correct working of the plugin
Improving Ja Scanner
In order to improve this extension, please report any issue founded in the plugin. Furthermore if you want report me any disclosed Ja usefull for the exploitation of this weakness and, if I have the time, I will add an acti for it in my plugin.
Disclaimer
This software has been created purely for the purposes of academic research and for the de of effecti techniques, and is not intended to be used to attack systems except where explicitly authorized. Project maintainers are not responsible or liable for misuse of the software. Use responsibly.
MIT License
Copyright (c) 2020 Ja Scanner
Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions:
The abo notice and this permission notice shall be included in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
项目信息
开发语言:Java
Star 数:804
技术要点
该项目属于漏洞知识库方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Java-Deserialization-Scanner - All-in-one plugin for Burp Suite for the detection |
| 所属分类 | 漏洞知识库 |
| 发布作者 | admin |
| 发布时间 | 2026-10-06 01:05:59 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 152 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |